Cybersecurity Maturity Model Certification Online Framework

Table of Contents
- Definition and Core Components of Cybersecurity Maturity Models
- Key Stages in a Generic Cybersecurity Maturity Model Framework
- Integration of NIST CSF, ISO/IEC 27001, and CIS Controls with Cybersecurity Maturity Models
- Online Certification Pathways for Cybersecurity Maturity Models
- Top 5 Online Certifications Validating Cybersecurity Maturity Model Proficiency
In an era where digital threats evolve at unprecedented speeds, organizations must adopt structured approaches to cybersecurity that transcend reactive measures. The Cybersecurity Maturity Model Certification (CMMC) and its online certification pathways provide a rigorous framework for assessing and elevating an entity’s defensive posture, aligning technical controls with governance principles. This model transcends industry boundaries, offering scalable benchmarks from foundational compliance to optimized resilience—yet its true value lies in translating maturity into actionable, measurable outcomes.
The integration of global standards such as NIST CSF, ISO/IEC 27001, and CIS Controls further complicates the landscape, demanding clarity on how each certification pathway validates proficiency across maturity stages. From leadership commitment to technical implementation, the distinction between an immature and a mature cybersecurity posture hinges on tangible metrics, audit readiness, and adaptive risk management. This guide dissects the core components of these models, maps online certification trajectories, and equips stakeholders with tools to self-assess, train, and certify their organizations against evolving threats.

Definition and Core Components of Cybersecurity Maturity Models
Cybersecurity Maturity Models (CMMs) provide a structured framework for organizations to evaluate, improve, and sustain their cybersecurity posture over time. These models are rooted in the principle that cybersecurity effectiveness is not static but evolves through deliberate stages of development, akin to organizational growth in other domains (e.g., process improvement frameworks like CMMI). By defining measurable criteria for each maturity level, CMMs enable leadership to prioritize investments, align security practices with business objectives, and demonstrate compliance with regulatory or industry-specific requirements. The core premise is that higher maturity correlates with reduced risk exposure, enhanced resilience, and proactive threat mitigation—rather than reactive incident response.The foundational principles of CMMs include continuous improvement, risk-based prioritization, and scalability to accommodate organizational growth or changing threat landscapes. Unlike one-size-fits-all checklists, CMMs emphasize adaptive governance, where controls and processes are tailored to the organization’s risk tolerance, industry context, and technological maturity. For example, a healthcare provider may prioritize patient data protection (e.g., HIPAA alignment) differently than a financial institution focused on fraud prevention (e.g., PCI DSS). The models also integrate feedback loops to refine strategies based on emerging threats, technological advancements, or regulatory updates.
Key Stages in a Generic Cybersecurity Maturity Model Framework
A generic CMM typically follows a five-stage progression, inspired by the Capability Maturity Model Integration (CMMI) and adapted for cybersecurity. Each stage builds on the previous one, transitioning from ad-hoc practices to optimized, data-driven security operations. Below is a structured breakdown of the stages, their characteristics, objectives, and measurable outcomes, presented in a comparative table for clarity.| Stage | Characteristics | Objectives | Measurable Outcomes | Risk Exposure Level |
|---|---|---|---|---|
| Initial (Ad Hoc) |
|
|
|
High (vulnerable to exploits, compliance gaps, and reputational damage). |
| Managed (Repeatable) |
|
|
|
Moderate (reactive to known threats; limited resilience to zero-day attacks). |
| Defined (Standardized) |
|
|
|
Low (proactive threat detection; aligned with regulatory expectations). |
| Quantitatively Managed (Measured) |
|
|
|
Minimal (adaptive to emerging threats; quantifiable ROI on security investments). |
| Optimizing (Continuous Improvement) |
|
|
|
Negligible (proactive threat neutralization; aligned with future-proofing strategies). |
Integration of NIST CSF, ISO/IEC 27001, and CIS Controls with Cybersecurity Maturity Models
While traditional CMMs provide a high-level maturity roadmap, frameworks like the NIST Cyber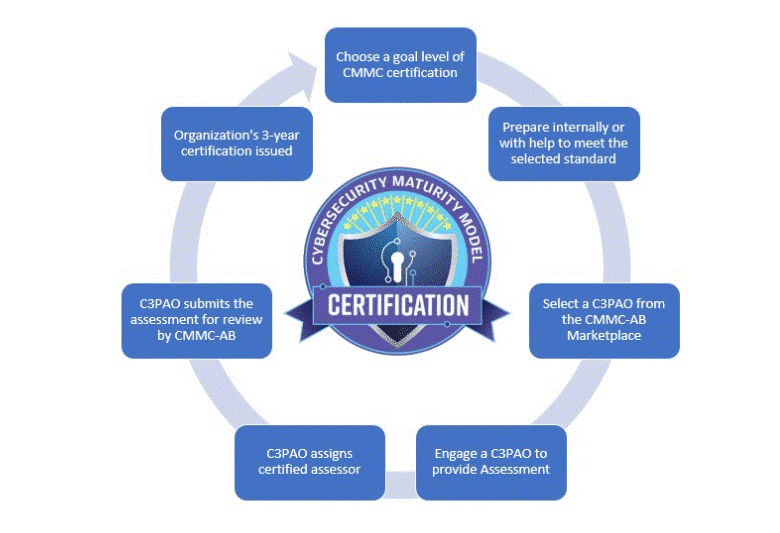
Online Certification Pathways for Cybersecurity Maturity Models
Cybersecurity maturity models, such as CMMC (Cybersecurity Maturity Model Certification), ISO/IEC 27001, and NIST SP 800-171, require structured validation through globally recognized certifications to ensure alignment with industry standards. Online certification pathways provide flexible, scalable, and accessible means for professionals and organizations to achieve compliance while demonstrating proficiency in maturity model frameworks. These certifications not only validate technical and managerial expertise but also ensure that organizations can systematically assess, implement, and improve their cybersecurity posture.The following section outlines the top 5 globally recognized online certification programs relevant to cybersecurity maturity models, their prerequisites, exam formats, cost structures, and their direct or indirect validation of maturity model proficiency. Additionally, it provides a step-by-step self-assessment methodology using the CMMC framework, a tag-based mapping system for online training courses, and a certification roadmap template for organizational upskilling. Audit and compliance requirements for online certifications, including remote assessment challenges, are also detailed with documentation checklists and best practices.
Top 5 Online Certifications Validating Cybersecurity Maturity Model Proficiency
The following table compares five globally recognized certifications that either directly align with maturity models (e.g., CMMC, ISO 27001) or indirectly validate proficiency through risk management, control implementation, and governance frameworks. Each certification is evaluated based on prerequisites, exam logistics, cost, and relevance to maturity model domains.| Certification | Prerequisites | Exam Format | Cost Breakdown (USD) | Maturity Model Validation |
|---|---|---|---|---|
| Certified Information Systems Security Professional (CISSP) |
|
|
|
The CISSP validates expertise across 8 domains, including security governance, risk management, and control implementation, which are foundational to maturity models like CMMC and ISO 27001. While not a maturity-specific certification, CISSP holders demonstrate the ability to design and manage cybersecurity programs aligned with frameworks such as NIST SP 800-53 (used in CMMC) and ISO/IEC 27002 controls. |
| Certified in Risk and Information Systems Control (CRISC) |
|
|
|
CRISC focuses on risk identification, assessment, and mitigation, directly aligning with maturity model requirements for risk management (CMMC L2/L3) and control implementation (ISO 27001 Clause 6/7). The certification emphasizes governance and compliance, making it ideal for professionals responsible for aligning cybersecurity programs with regulatory and contractual obligations (e.g., DFARS, FAR). |
| ISO 27001 Lead Auditor |
|
|
|
This certification directly validates proficiency in ISO 27001, a maturity model framework for information security management systems (ISMS). Lead Auditors are trained to assess organizational maturity against ISO 27001 controls, including risk treatment, policy implementation, and continuous improvement—key pillars of CMMC L3 and other high-maturity frameworks. |
| Certified Cloud Security Professional (CCSP) |
|
|
|
CCSP validates expertise in cloud-specific security controls, which are increasingly integrated into maturity models (e.g., CMMC L4/L5 for cloud environments). The certification covers architecture, governance, and compliance, aligning with NIST SP 800-171 Rev. 2 and ISO 27017/27018 for cloud-based risk management. |
| Certified Information Security Manager (CISM) |
The journey toward cybersecurity maturity is not a one-time achievement but a continuous evolution requiring strategic alignment, resource investment, and relentless vigilance. Online certifications serve as milestones along this path, offering verifiable proof of competence while bridging gaps between theoretical frameworks and real-world application. By leveraging structured self-assessments, role-specific training roadmaps, and compliance-ready documentation, organizations can transform maturity model certifications from abstract benchmarks into operational strengths. The result is not merely compliance—it is a fortified, adaptive cybersecurity culture capable of withstanding the next wave of digital adversaries. |
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.