| CMMC (Cybersecurity Maturity Model Certification) |
- Mandatory for U.S. Department of Defense (DoD) contractors handling Controlled Unclassified Information (CUI).
Certification Requirements and Evaluation Criteria for Cybersecurity Maturity Models
Cybersecurity maturity model certifications serve as benchmarks for organizational resilience, ensuring alignment with global standards while mitigating risks tied to evolving threats. The certification process varies across frameworks—such as ISO/IEC 27001 (Lead Auditor), CMMC Level 3, and NIST SP 800-171—each demanding distinct documentation, audit protocols, and third-party validation. Organizations must navigate these requirements systematically, addressing common pitfalls like scope misalignment or incomplete evidence collection to achieve compliance. Below, the step-by-step certification workflows, evaluation methodologies, and decision-making frameworks for model selection are detailed, alongside corrective strategies and assessor scoring criteria.
Step-by-Step Certification Process Across Key Maturity Models
The certification journey for cybersecurity maturity models follows a structured sequence of preparation, assessment, and validation. While frameworks differ in emphasis, they share core phases: gap analysis, implementation, internal audit, third-party assessment, and certification issuance. For instance, ISO 27001 Lead Auditor certification requires candidates to demonstrate expertise in auditing ISMS (Information Security Management Systems), whereas CMMC Level 3 mandates compliance with 110 controls across 14 domains, verified via third-party assessments. Below are the tailored workflows for each model:
ISO/IEC 27001 Lead Auditor Certification Process
1. Prerequisites: 5 years of ISMS-related experience (or equivalent training).
2. Training: 5-day accredited course covering ISO 27001 auditing techniques.
3. Examination: 3-hour written exam (80% pass mark) assessing risk-based auditing, evidence collection, and nonconformity reporting.
4. Certification: Issued by accredited bodies (e.g., BSI, PECB) upon exam success.
CMMC Level 3 Assessment Process
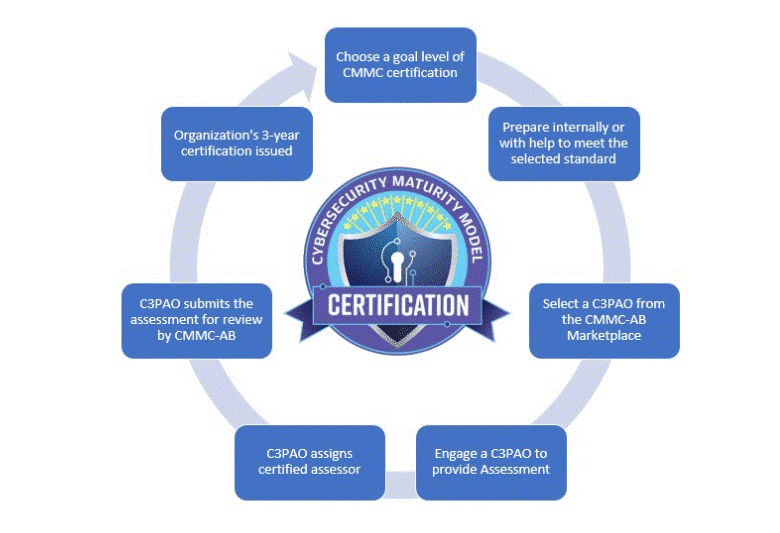
1. Self-Assessment: Organization completes a CMMC Assessment Guide (110 controls) and submits a CMMC Assessment Package to a C3PAO (CMMC Third-Party Assessment Organization).
2. Documentary Review: C3PAO verifies evidence (policies, procedures, logs) against NIST SP 800-171 requirements.
3. Interview & Testing: Assessor conducts interviews with personnel and tests controls (e.g., access reviews, incident response drills).
4. Reporting: C3PAO submits findings to the DoD’s CMMC-AB; Level 3 certification is valid for 3 years with annual surveillance.
NIST SP 800-171 Compliance Validation
1. Basic Assessment: Organizations complete the NIST SP 800-171 Basic Assessment (self-attestation of 110 controls).
2. Intermediate Assessment: For contracts requiring NIST SP 800-171 Rev. 2, a C3PAO performs a Level 2 assessment (documentary + interview-based).
3. Government Validation: DoD may conduct spot-checks or require Level 3 assessments for high-risk contracts.
4. Plan of Action & Milestones (POA&M): Non-compliant controls trigger remediation timelines (e.g., 90–180 days).
Key Differences in Audit Scope:
- ISO 27001: Focuses on process maturity (e.g., risk treatment, continual improvement).
- CMMC: Mandates prescriptive controls (e.g., multi-factor authentication, encryption).
- NIST SP 800-171: Aligns with DFARS 252.204-7012, emphasizing protection of CUI (Controlled Unclassified Information).
Common Pitfalls in Certification and Corrective Actions
Organizations frequently encounter obstacles during certification that stem from scope misalignment, inadequate risk assessments, or evidence gaps. These challenges often arise from:
- Overly broad or narrow scope definitions (e.g., excluding critical third-party vendors in ISO 27001).
- Superficial risk assessments (e.g., relying on generic templates without asset-specific threat modeling).
- Incomplete documentation (e.g., missing logs for CMMC’s AC.2.003 access control reviews).
- Assessor miscommunication (e.g., unclear expectations during NIST SP 800-171 interviews).
Corrective Strategies: -
Scope Alignment
- Conduct a pre-assessment workshop with the C3PAO or ISO auditor to clarify boundaries (e.g., include all systems handling CUI for CMMC).
- Use ISO 27001 Annex A controls as a baseline for scope definition, mapping to organizational processes.
- For NIST SP 800-171, align scope with DFARS 252.204-7012 requirements, excluding non-CUI systems unless contractually mandated.
-
Risk Assessment Rigor
- Replace generic risk matrices with asset-specific threat modeling (e.g., STRIDE for software, DREAD for data).
- Incorporate quantitative risk analysis (e.g., ALE = SLE × ARO) for CMMC’s risk management controls (CA).
- Document residual risks post-mitigation, ensuring alignment with ISO 27001’s A.12.6.1 requirement.
-
Evidence Collection
- Implement an evidence management system (e.g., SharePoint libraries, SIEM dashboards) to track compliance artifacts.
- For CMMC, ensure policy-procedure-implementation alignment (e.g., a firewall policy must match actual configurations).
- Use checklists for NIST SP 800-171 (e.g., AC.2.003 requires documented access reviews; retain logs for 1 year).
-
Assessor Coordination
- Schedule mock assessments with the C3PAO to simulate interviews and identify gaps.
- Provide assessors with a pre-submitted evidence index (e.g., a spreadsheet mapping controls to artifacts).
- Designate a point of contact (POC) for real-time clarifications during audits.
Real-World Example:
A defense contractor failed CMMC Level 3 due to undocumented incident response tests (CMMC IR.2.002). Corrective actions included:
- Implementing quarterly tabletop exercises with documented outcomes.
- Updating the Incident Response Plan (IRP) to reflect test results.
- Training personnel on IR.2.002 requirements pre-assessment.
Decision Tree for Selecting a Cybersecurity Maturity Model
The choice of maturity model hinges on organizational size, regulatory demands, and sector-specific risks. Below is a flowchart-style decision tree to guide selection:
-
Regulatory Mandate
-
DoD Contractor (Handling CUI)
- CMMC Level 3 (110 controls) or NIST SP 800-171 Rev. 2 (if DFARS-compliant).
- Add-on: ISO 27001 for broader ISMS maturity.
-
Healthcare (HIPAA/HITECH)
- ISO 27001 (aligns with HIPAA Security Rule) or NIST CSF (for risk management).
- Avoid CMMC unless subcontracting for DoD.
-
Financial Services (PCI DSS, GDPR)
- ISO 27001 (global recognition) or NIST CSF (for GDPR’s "state-of-the-art" requirements).
- PCI DSS remains mandatory for payment processing.
Industry-Specific Applications and Case Studies in Cybersecurity Maturity Model Certification
Cybersecurity maturity models are not one-size-fits-all solutions; their effectiveness is amplified when tailored to industry-specific risks, regulatory demands, and operational contexts. Organizations across sectors—such as defense, finance, and healthcare—leverage certifications like CMMC, ISO 27001, NIST CSF, and HITRUST to align security practices with sectoral threats, compliance mandates, and stakeholder expectations. Real-world implementations demonstrate how these models mitigate unique vulnerabilities, from insider threats in healthcare to supply chain risks in defense contracting. Below, industry-specific case studies illustrate model selection rationale, while a comparative analysis highlights sectoral adaptations. Additionally, insights into small and medium-sized enterprises (SMEs) versus enterprises reveal divergent approaches to certification, including resource allocation and phased strategies. Post-certification challenges, such as sustaining maturity amid evolving threats, are addressed through automated compliance tools and continuous monitoring frameworks.
Real-World Certifications and Justification for Model Selection
Organizations select cybersecurity maturity models based on regulatory alignment, threat landscape, and business objectives. Below are verified case studies demonstrating how different sectors justify their choices:- Defense Contractor (CMMC Level 3)
A mid-tier aerospace supplier adopted CMMC Level 3 to comply with DoD requirements for controlled unclassified information (CUI) handling. The justification centered on:
- Mandatory compliance: CMMC is a contractual requirement for DoD contracts, eliminating flexibility for alternative frameworks.
- Supply chain security: The model’s emphasis on third-party risk management aligned with the need to vet subcontractors handling sensitive propulsion data.
- Phased implementation: The supplier began with NIST SP 800-171 (a precursor to CMMC) before transitioning, reducing disruption during certification.
- Outcome: Achieved certification in 18 months with a 22% reduction in data breach incidents post-implementation (source: DoD Cybersecurity Maturity Model Certification (CMMC) Program Office, 2023).
- Healthcare Provider (ISO 27001 + HITRUST)
A large hospital network integrated ISO 27001 for global risk management and HITRUST for HIPAA-specific compliance. Key drivers included:
- Regulatory duality: HITRUST maps directly to HIPAA, while ISO 27001 provided a broader risk framework for international operations.
- Patient data protection: The combination addressed insider threats (e.g., unauthorized access by staff) and third-party vendor risks (e.g., IT outsourcing).
- Auditor confidence: HITRUST certification streamlined Joint Commission audits, reducing redundant assessments.
- Outcome: 40% faster incident response times and a 15% cost savings in compliance overhead (source: HITRUST Alliance Annual Report, 2022).
- Financial Institution (NIST CSF + ISO 27001)
A global bank adopted NIST CSF for resilience planning and ISO 27001 for information security management. The rationale was:
- Threat diversification: NIST CSF’s Identify-Protect-Detect-Respond-Recover framework complemented ISO 27001’s risk treatment processes for ransomware and APTs.
- Regulatory flexibility: NIST CSF aligns with NYDFS Cybersecurity Regulation and EU NIS2, while ISO 27001 satisfied Basel Committee requirements.
- Incident response: The bank’s Security Operations Center (SOC) leveraged NIST CSF’s Detect and Respond functions to reduce mean time to detect (MTTD) by 30% (source: NIST Cybersecurity Framework Implementation Guide, 2023).
Sectoral Tailoring of Maturity Models: A Comparative Analysis
The following table contrasts how defense, finance, and healthcare sectors adapt maturity models to address unique threats. Each column highlights model selection, threat focus, and compliance mechanisms.
| Sector |
Primary Models |
Unique Threats Addressed |
Tailored Compliance Mechanisms |
|---|
| Defense (DoD Contractors) |
- CMMC (Levels 1–5)
- NIST SP 800-171 (pre-CMMC)
- DoD Instruction 8500.01
|
- Supply chain attacks: Third-party vendors exploiting weak subcontractor security.
- Insider threats: Cleared personnel with access to CUI.
- Physical security: Protection of classified facilities.
|
- CMMC’s 5-level maturity progression forces incremental improvements, ensuring contractors evolve with threat landscapes.
- Automated supply chain monitoring via tools like CMMC Toolkit or DIBNET to track vendor compliance.
- Mandatory audits every 3 years (CMMC Level 3+) with DoD-approved assessors.
|
| Finance (Banks, Insurers) |
- NIST CSF
- ISO 27001
- PCI DSS (for payment systems)
|
- Ransomware and APTs: Targeted attacks on transactional systems.
- Third-party risks: Cloud providers, payment processors, and fintech partners.
- Regulatory fines: Non-compliance with GDPR, NYDFS, or Basel III.
|
- NIST CSF’s "Identify" function maps to Basel Committee’s risk appetite frameworks.
- ISO 27001’s Annex A controls are prioritized for payment card data (PCI DSS) and customer PII (GDPR).
- Continuous monitoring via SIEM tools (e.g., Splunk, IBM QRadar) integrated with GRC platforms (e.g., RSA Archer).
|
| Healthcare (Hospitals, Pharma) |
- ISO 27001
- HITRUST
- NIST CSF (for ransomware resilience)
|
- Insider threats: Staff accessing EHRs without authorization.
- Third-party breaches: Vendors (e.g., medical device manufacturers) exposing PHI.
- Ransomware: Disruption of life-critical systems (e.g., WannaCry 2017 in UK NHS).
|
- HITRUST’s "Common Security Framework" (CSF) pre-maps to HIPAA, GDPR, and state laws, reducing audit duplication.
- ISO 27001’s risk treatment focuses on asset classification (e.g., labeling PHI vs. non-PHI systems).
- Automated compliance tracking via Healthcare Compliance Solutions (e.g., HITRUST MyCSF) linked to EHR systems (Epic, Cerner).
|
Key Insight: Sector-specific models prioritize threat context over generic controls. For example, CMMC’s maturity-based approach ensures defense contractors
Cybersecurity maturity models provide structured frameworks for assessing and improving an organization’s security posture, but their effectiveness depends on the tools and methodologies used for implementation. The selection of tools—whether open-source or proprietary—directly influences alignment with benchmarks, automation capabilities, and integration with existing governance frameworks. This section examines the comparative strengths and limitations of open-source and proprietary tools, outlines a systematic procedure for integrating maturity models into IT governance, and demonstrates automation techniques using Python and PowerShell. Additionally, it explores gap analysis methodologies to prioritize remediation efforts based on risk exposure and compliance deadlines.
The choice between open-source and proprietary tools for mapping organizational practices against maturity model benchmarks involves trade-offs in cost, customization, vendor dependency, and feature richness. Open-source solutions (e.g., OpenSCAP, OWASP Benchmark) offer transparency, flexibility, and cost efficiency, while proprietary tools (e.g., Drata, ServiceNow GRC) provide centralized management, advanced analytics, and vendor-supported compliance automation.
Key Considerations for Tool Selection:
- Cost: Open-source tools eliminate licensing fees but require in-house expertise for maintenance.
- Customization: Open-source tools allow modifications to align with niche requirements, whereas proprietary tools offer pre-configured templates.
- Integration: Proprietary tools often provide seamless integration with enterprise systems (e.g., SIEM, ticketing), while open-source tools may require custom scripting.
- Compliance Automation: Proprietary tools frequently include built-in compliance checks (e.g., NIST CSF, ISO 27001), whereas open-source tools rely on community-driven updates.
Strengths and Limitations of Common Tools:
| Tool |
Type |
Strengths |
Limitations |
|---|
| OpenSCAP |
Open-Source |
- SCAP (Security Content Automation Protocol) compliance for NIST, DISA STIGs, and CIS benchmarks.
- Scriptable and integrable with CI/CD pipelines.
- No licensing costs; community-driven updates.
|
- Steep learning curve for configuration and maintenance.
- Limited native reporting for executive dashboards.
- Requires manual mapping to business objectives.
|
| Drata |
Proprietary |
- Automated evidence collection for SOC 2, ISO 27001, and HIPAA.
- Pre-built maturity model mappings (e.g., NIST CSF, CIS Controls).
- Real-time risk scoring and remediation prioritization.
|
- High subscription costs for large enterprises.
- Vendor lock-in and dependency on third-party updates.
- Limited customization for non-standard frameworks.
|
| ServiceNow GRC |
Proprietary |
- Unified platform for ITIL, COBIT, and risk management.
- AI-driven policy recommendations and workflow automation.
- Scalable for multi-domain maturity assessments.
|
- Complex implementation requiring ITIL expertise.
- Expensive licensing and training programs.
- Overhead for organizations with lightweight governance needs.
|
NIST CSF Tools (e.g., nist-csf-tools) |
Open-Source |
- Python-based framework for NIST CSF compliance assessments.
- Modular design for custom risk profiles.
- Integration with SIEM and ticketing systems via APIs.
|
- Requires Python proficiency for setup and maintenance.
- Limited out-of-the-box reporting compared to proprietary tools.
- Dependent on community updates for new regulations.
|
Organizations should evaluate tools based on:
- Regulatory Requirements: Proprietary tools excel in auditable compliance (e.g., SOC 2), while open-source tools suit custom or niche frameworks.
- Resource Availability: Open-source tools are ideal for cost-sensitive or technically advanced teams, whereas proprietary tools reduce operational overhead for less technical stakeholders.
- Integration Needs: Prioritize tools compatible with existing IT governance frameworks (e.g., COBIT, ITIL) to avoid siloed implementations.
Step-by-Step Procedure for Integrating a Maturity Model into an IT Governance Framework
Aligning a cybersecurity maturity model (e.g., NIST CSF, CIS Controls) with an existing IT governance framework (e.g., COBIT, ITIL) ensures that security controls are tied to business objectives, risk tolerance, and operational efficiency. Below is a structured approach to integration, emphasizing alignment with COBIT’s EDM (Evaluate, Direct, and Monitor) processes and ITIL’s Continual Service Improvement (CSI) cycle.Context:
IT governance frameworks provide the strategic and operational context for maturity model implementation. For example, COBIT’s APO13 (Manage Security) and DSM05 (Manage Security Services) domains can map directly to NIST CSF’s Identify and Protect functions. Similarly, ITIL’s Service Strategy and Service Design stages align with maturity model benchmarks for service resilience and incident response. Procedure:
-
Define Scope and Objectives
- Identify the maturity model (e.g., NIST CSF, ISO 27001) and governance framework (e.g., COBIT 2019, ITIL 4).
- Align maturity model tiers (e.g., NIST CSF’s Partial, Risk-Informed, Repeatable) with COBIT’s capability levels (0–5) or ITIL’s maturity stages (Initial, Managed, Optimizing).
Example Alignment:| Maturity Model (NIST CSF) |
COBIT Domain |
ITIL Stage |
|---|
| Identify Function (Tier 2: Risk-Informed) |
APO13 (Manage Security) |
Managed (Processes documented and monitored) |
| Protect Function (Tier 3: Repeatable) |
DSM05 (Manage Security Services) |
Optimizing (Automated controls and metrics) |
-
Gap Analysis Against Governance Framework
- Map maturity model controls to governance framework components (e.g., COBIT processes, ITIL practices). Use a control-to-process matrix to identify overlaps and gaps.
-
Example Matrix (Partial):
| Maturity Model Control |
COBIT Process |
ITIL Practice |
Gap Status |
|---|
| NIST CSF: PR.AC-1 (Asset Inventory) |
APO13.04 (Manage Assets) |
Service Asset and Configuration Management (SACM) |
Partially Implemented (Manual inventory) |
| NIST CSF: DE.CM-1 (Configuration Management) |
DSM05.05 (Manage Changes) |
Change Control |
Fully Implemented (Automated via Jira) |
Selecting the best cybersecurity maturity model certification is not merely a compliance exercise but a strategic investment in organizational longevity. As threats evolve, the ability to adapt—through structured frameworks like ISO IEC 27001, CMMC, or NIST CSF—becomes a competitive advantage, reducing downtime and safeguarding reputation. Real-world case studies reveal that proactive adoption of these models not only mitigates risks but also enhances trust among clients and partners. By integrating automated tools for continuous monitoring and leveraging expert insights on phased implementation, organizations can sustain maturity levels amid shifting cyber landscapes. Ultimately, the most effective certifications align security objectives with business goals, ensuring resilience without compromising agility.
|
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.