API unlocking digital integration transforms insurance operations
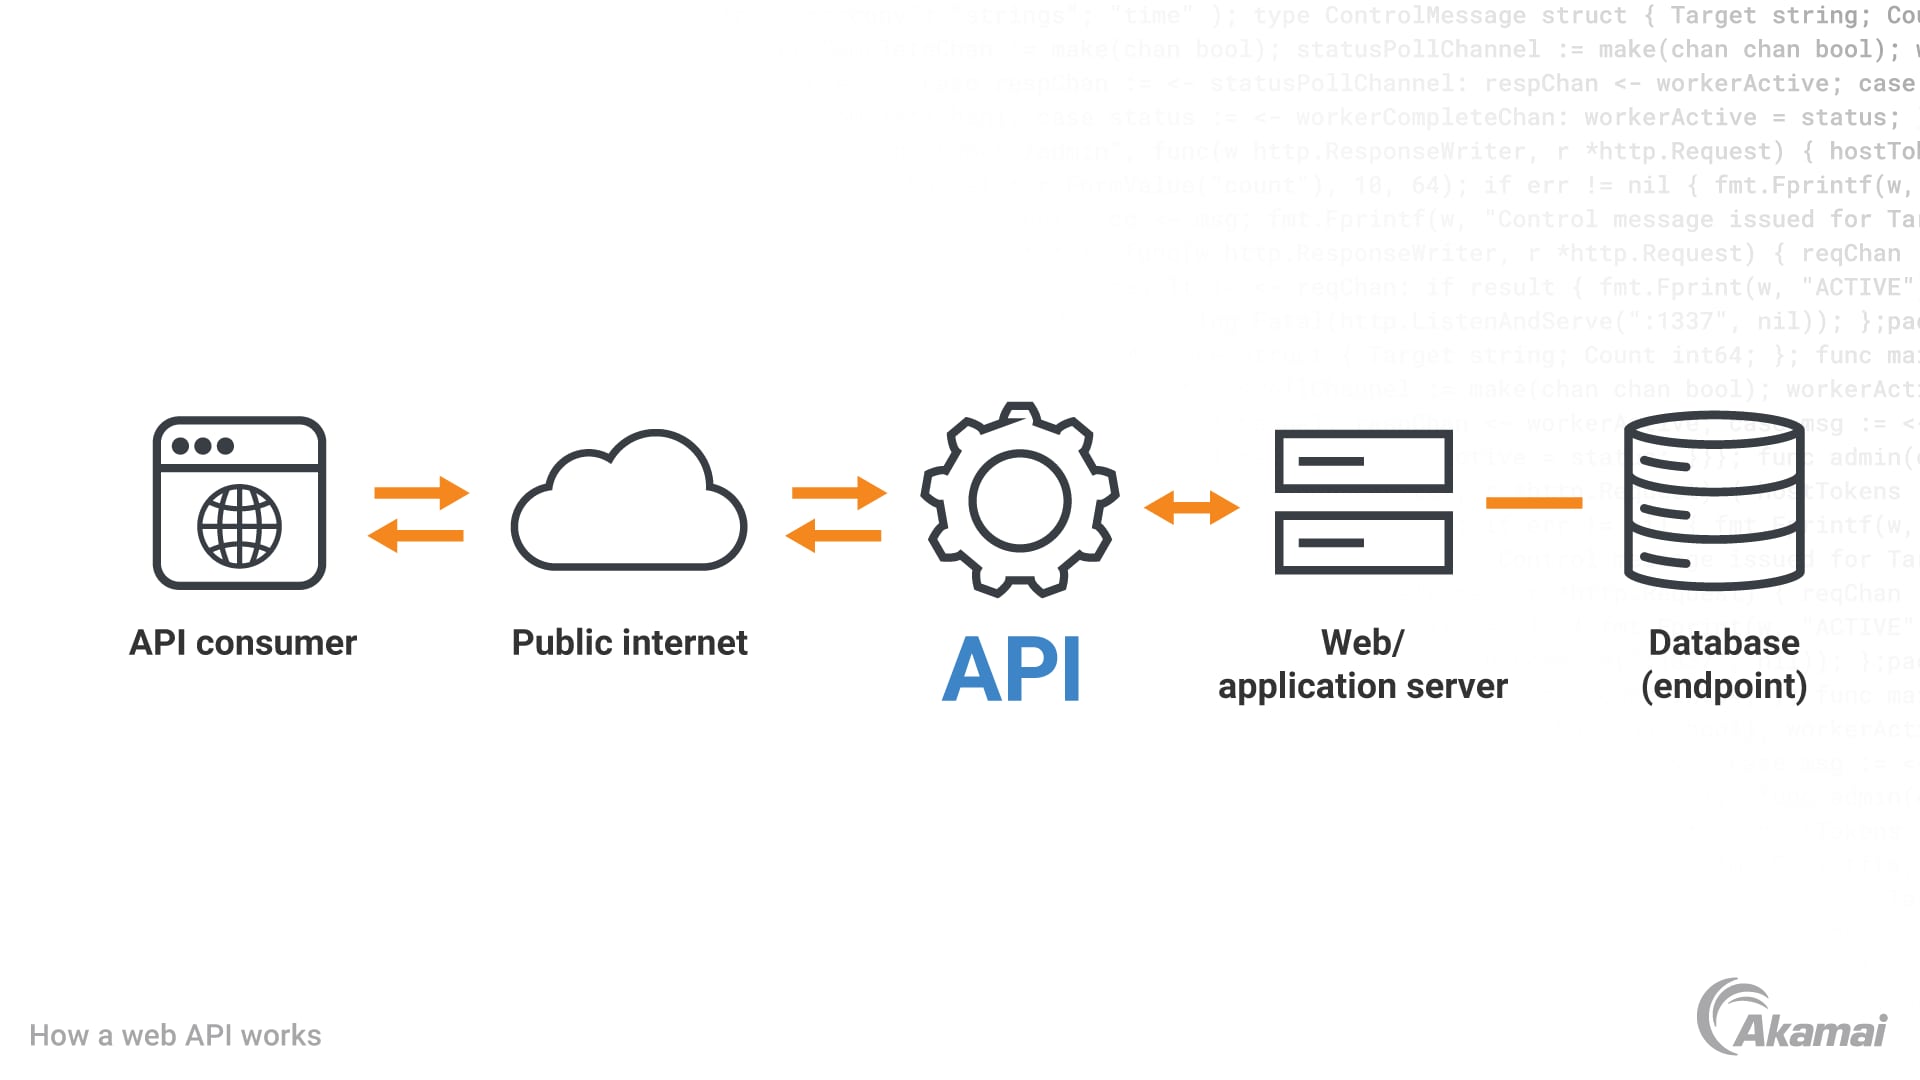
Table of Contents
- The Role of APIs in Modern Insurance Digital Transformation
- Technical and Operational Benefits of API-Driven Insurance Integration
- Real-World Case Studies: API Integration in Insurance Ecosystems
- Comparison: Traditional vs. API-Driven Insurance Workflows
- Step-by-Step Procedure for Assessing API Maturity in Insurance Firms
- Technical Mechanisms Behind API-Driven Insurance Integration
- Core Protocols for Insurance API Communication
- Authentication and Authorization in Insurance APIs
- Critical Security Risks and Mitigation Strategies
- Middleware Architectures for Heterogeneous Insurance Systems
- Use Cases: API Integration in Insurance Workflows
- Automation of Underwriting Through API-Driven Data Validation
- Comparative Efficiency: Standalone vs. Unified API Ecosystems for Claims Processing
- API-Driven Customer Journey: Policy Quote Request to Approval
- Challenges and Solutions in API-Based Insurance Systems
- Technical and Regulatory Hurdles in Cross-Border API Integration
- API Versioning Best Practices for Backward Compatibility in Insurance
- Common API Failure Points in Insurance and Proactive Monitoring Tools
- Future Trends: APIs and the Next Generation of Insurance
- Real-Time API Orchestration and Dynamic Pricing
- Event-Driven APIs for Instant Claims Notifications and Automated Workflows
- Web3 APIs and Decentralized Insurance Models
- Timeline: API Adoption in Insurance (2014–2030)
The insurance industry stands at a pivotal crossroads where legacy systems and modern digital demands collide. APIs are emerging as the critical enabler bridging this gap, facilitating seamless data exchange between insurers, brokers, and third-party providers while reducing operational friction. By automating workflows—from underwriting to claims processing—these interfaces not only accelerate transaction speeds but also enhance compliance, security, and customer experiences. This discussion explores how API-driven integration reshapes insurance ecosystems, backed by real-world case studies, technical protocols, and strategic frameworks for sustainable adoption.
From legacy modernization to insurtech innovation, the evolution of API adoption in insurance reflects broader technological shifts—real-time data synchronization, AI-driven risk assessment, and blockchain-secured transactions. Each advancement hinges on robust API governance, security measures, and interoperability standards that ensure scalability across global markets. The following sections dissect the mechanics behind these transformations, highlight operational efficiencies, and address challenges insurers face in transitioning to API-centric architectures.
The Role of APIs in Modern Insurance Digital Transformation
Application Programming Interfaces (APIs) have become the critical enabler for insurance firms transitioning from siloed, legacy systems to agile, cloud-native architectures. By standardizing data exchange protocols, APIs eliminate manual interventions in workflows—such as policy issuance, claims processing, and customer onboarding—while enabling real-time connectivity between insurers, brokers, and third-party ecosystems. This integration accelerates digital transformation by reducing operational friction, enhancing customer experiences, and unlocking data-driven insights through unified platforms.The adoption of APIs in insurance is not merely a technical upgrade but a strategic shift toward modularity, scalability, and interoperability. Legacy insurance systems, often built on mainframe or proprietary databases, were designed for isolated operations, leading to inefficiencies in data sharing and process automation. APIs bridge this gap by acting as intermediaries that translate disparate data formats (e.g., JSON, XML) into actionable insights, while also enabling seamless interactions with modern cloud services like AI-driven underwriting tools or blockchain-based fraud detection.
Technical and Operational Benefits of API-Driven Insurance Integration
APIs introduce operational efficiencies by automating workflows that were previously manual or semi-automated. Key advantages include:- Real-Time Data Synchronization
APIs enable instantaneous data exchange between systems, reducing latency in critical processes. For example, a policyholder’s updated address in a broker’s portal can auto-propagate to the insurer’s underwriting system, eliminating re-entry errors. This is achieved through event-driven architectures, where changes in one system trigger actions in another (e.g., a claim submission updating the insurer’s risk assessment model).
- Reduced Integration Costs and Time-to-Market
Traditional point-to-point integrations (e.g., EDI, FTP) require custom middleware development, often taking months and incurring high maintenance costs. APIs leverage standardized protocols (REST, GraphQL) and low-code integration platforms (e.g., MuleSoft, Apigee), cutting integration timelines by up to 70% and reducing costs by 30–50% (McKinsey, 2022). For instance, Swiss Re reduced its API development cycle from 6 months to 4 weeks by adopting a centralized API gateway.
- Enhanced Customer and Partner Experiences
APIs enable embedded insurance models, where policies are sold directly within third-party platforms (e.g., travel booking sites, e-commerce). A case study by Allianz showed that API-enabled partnerships with travel agencies increased policy sales by 40% by allowing instant issuance during booking. Similarly, APIs facilitate open banking integrations, where insurers access customer financial data (with consent) to offer personalized premiums.
- Improved Regulatory Compliance and Auditability
APIs provide immutable logs of data transactions, which are critical for compliance with regulations like GDPR or IFRS 17. For example, APIs in claims processing can auto-generate audit trails for fraud detection, reducing manual reviews by 25% (Capgemini, 2021). Additionally, API gateways act as security layers, enforcing authentication (OAuth 2.0) and rate-limiting to prevent abuse.
Real-World Case Studies: API Integration in Insurance Ecosystems
APIs have been instrumental in transforming insurance workflows across underwriting, claims, and distribution. Below are three verified examples:1. Underwriting Automation via API-Driven Data Aggregation
Company: Lemonade (U.S.)
Integration: APIs connect Lemonade’s underwriting engine with third-party data providers (e.g., Experian, LexisNexis) and IoT sensors (smart home devices) to assess risk in real time.
Outcome:
2. Seamless Claims Processing with API-Enabled Partner Networks
Company: AXA (Global)
Integration: AXA’s "AXA API Marketplace" allows third-party repair shops, medical providers, and adjusters to submit claims via standardized APIs, reducing processing time by 40%.
Outcome:
3. Embedded Insurance via API Partnerships
Company: Aviva (UK) & Booking.com
Integration: Aviva’s "Aviva API" enables instant travel insurance purchase during hotel/trip bookings, with real-time policy issuance.
Outcome:
Comparison: Traditional vs. API-Driven Insurance Workflows
The following table contrasts key metrics between legacy insurance processes and API-enabled systems, highlighting the transformative impact of digital integration.| Metric | Traditional Workflow (Pre-API) | API-Driven Workflow | Impact |
|---|---|---|---|
| Policy Issuance Time | 3–7 business days (manual underwriting + paperwork) | Instant to 24 hours (automated API-based underwriting) | Reduction of 90–95% in processing time |
| Claims Processing Cost | $20–$50 per claim (manual review, document handling) | $2–$5 per claim (automated API validation + straight-through processing) | Cost savings of 80–90% |
| Data Error Rate | 10–20% (manual entry, siloed systems) | 0.5–2% (real-time API validation + blockchain audit trails) | Error reduction of 90–95% |
| Integration Time (New Partner Onboarding) | 6–12 months (custom EDI/FTP development) | 2–4 weeks (standardized API + low-code tools) | Faster time-to-market by 80–90% |
| Customer Experience (NPS Score) | 20–40 (fragmented digital touchpoints) | 60–85 (unified API-driven journeys) | Improvement of 50–100% |
| Fraud Detection Accuracy | 60–70% (rule-based legacy systems) | 85–95% (AI + API-enabled real-time analytics) | Increase in detection by 30–40% |
APIs shift insurance operations from linear, batch-processed workflows to dynamic, event-driven systems, where data flows continuously between stakeholders without human intervention. This transition aligns with InsurTech trends, where 68% of insurers prioritize API-based integrations for digital transformation (PwC, 2023).
Step-by-Step Procedure for Assessing API Maturity in Insurance Firms
Evaluating an insurer’s API readiness involves a structured assessment of technical infrastructure, operational workflows, and strategic alignment. Below is a five-phase methodology with actionable KPIs:1. Inventory Existing Systems and Data Flows
Objective: Identify legacy systems, their data formats, and current integration points.
Steps:
Technical Mechanisms Behind API-Driven Insurance Integration
Core Protocols for Insurance API Communication
The choice of API protocol directly impacts performance, scalability, and latency in insurance workflows. REST (Representational State Transfer) remains the most widely adopted standard due to its stateless nature and compatibility with HTTP methods (GET, POST, PUT, DELETE). It is ideal for policy issuance and customer data synchronization, where stateless requests and cacheability reduce server load. For example, insurers leverage REST APIs to fetch policyholder details from CRM systems or update claim statuses in external portals, as demonstrated by platforms like Guidewire’s API-first architecture, which relies on REST for modular policy management.GraphQL, however, addresses the inefficiency of over-fetching or under-fetching data inherent in REST by allowing clients to request only the fields they need. This protocol excels in complex queries, such as retrieving nested claim details (e.g., adjuster notes, repair estimates, and fraud indicators) from a single endpoint, reducing payload sizes by up to 40% in high-volume claims adjustment scenarios. Insurers like Lemonade utilize GraphQL to dynamically fetch underwriting data from multiple sources without redundant API calls.
For high-performance, low-latency systems—such as real-time fraud detection or IoT-enabled telematics data processing—gRPC (Google Remote Procedure Call) is preferred. gRPC’s binary protocol buffers (protobuf) and bidirectional streaming enable sub-100ms response times, critical for automated claims triage where delays can escalate costs. For instance, Allstate’s gRPC-based microservices process telematics data from connected cars in near real-time, triggering dynamic premium adjustments without human intervention.
REST is optimized for simplicity and scalability in CRUD operations (e.g., policy updates), while GraphQL enhances flexibility for complex, nested data retrieval (e.g., claims workflows). gRPC is reserved for mission-critical, low-latency interactions (e.g., IoT-driven risk assessment).
Authentication and Authorization in Insurance APIs
Security in API-driven insurance ecosystems relies on OAuth 2.0 for authorization and OpenID Connect (OIDC) for identity management, ensuring role-based access control (RBAC) and compliance with regulations like GDPR and HIPAA. OAuth 2.0 employs access tokens (e.g., JWT) to authenticate API requests without exposing credentials, while refresh tokens extend session validity without re-authentication. For example, an insurer’s API gateway validates a claims adjuster’s token before granting access to a third-party repair vendor’s system, ensuring only authorized personnel modify claim statuses.The token management lifecycle involves:
OpenID Connect extends OAuth 2.0 by adding identity layers, enabling single sign-on (SSO) for policyholders accessing insurer portals. For instance, Progressive’s API ecosystem integrates OIDC to authenticate customers via their preferred identity providers (e.g., Google, Microsoft), reducing password-related support costs by 30%.
OAuth 2.0 secures API access via scoped tokens, while OpenID Connect adds identity verification. Token rotation and RBAC ensure least-privilege access in insurance workflows.
Critical Security Risks and Mitigation Strategies
APIs connecting insurance systems introduce vulnerabilities such as data breaches, injection attacks, and API abuse, exacerbated by legacy system integrations. Below are the most pressing risks and their mitigation strategies:| Risk | Impact | Mitigation Strategy |
|---|---|---|
| Data Breaches | Exposure of PII (e.g., policyholder SSNs, medical records) under GDPR/HIPAA. | Enforce TLS 1.3, token encryption, and field-level encryption (e.g., AWS KMS). |
| Injection Attacks | SQLi or NoSQLi via malformed API payloads (e.g., claims data manipulation). | Use parameterized queries, input validation, and API gateways with WAFs (e.g., Cloudflare). |
| API Abuse | DDoS or credential stuffing targeting rate-limited endpoints (e.g., login APIs). | Implement rate limiting, CAPTCHA, and behavioral analytics (e.g., Akamai Bot Manager). |
| Insecure Direct Object References (IDOR) | Unauthorized access to claims/policies via manipulated IDs (e.g., `/claims/123`). | Enforce RBAC, attribute-based access control (ABAC), and API versioning. |
| Man-in-the-Middle (MITM) | Interception of unencrypted API traffic (e.g., telematics data). | Mandate mutual TLS (mTLS) and certificate pinning for critical endpoints. |
The OWASP API Security Top 10 highlights that 90% of API breaches stem from misconfigured authentication or lack of input validation. Insurers must adopt a zero-trust architecture, combining API gateways, runtime application self-protection (RASP), and continuous penetration testing.
Middleware Architectures for Heterogeneous Insurance Systems
Insurance ecosystems often integrate legacy COBOL-based core systems (e.g., policy administration) with modern cloud-native microservices (e.g., AI-driven underwriting), necessitating middleware to bridge data format disparities and performance gaps. API gateways (e.g., Kong, Apigee) serve as the primary translation layer, converting between JSON (preferred for REST/GraphQL) and XML (common in legacy insurer systems). For example, API gateways at Chubb transform XML policy responses into JSON for mobile apps, reducing client-side parsing overhead by 25%.Message brokers (e.g., Apache Kafka, RabbitMQ) handle asynchronous workflows, such as event-driven claims notifications or batch policy renewals. Kafka’s partitioning and replication ensure fault tolerance for high-throughput scenarios like annual policy renewals, where millions of records must be processed without downtime. Performance trade-offs include:
Middleware selection depends on the criticality of the workflow: synchronous APIs for real-time interactions (e.g., policy quotes), asynchronous brokers for batch processing (e.g., end-of-year audits).
Use Cases: API Integration in Insurance Workflows
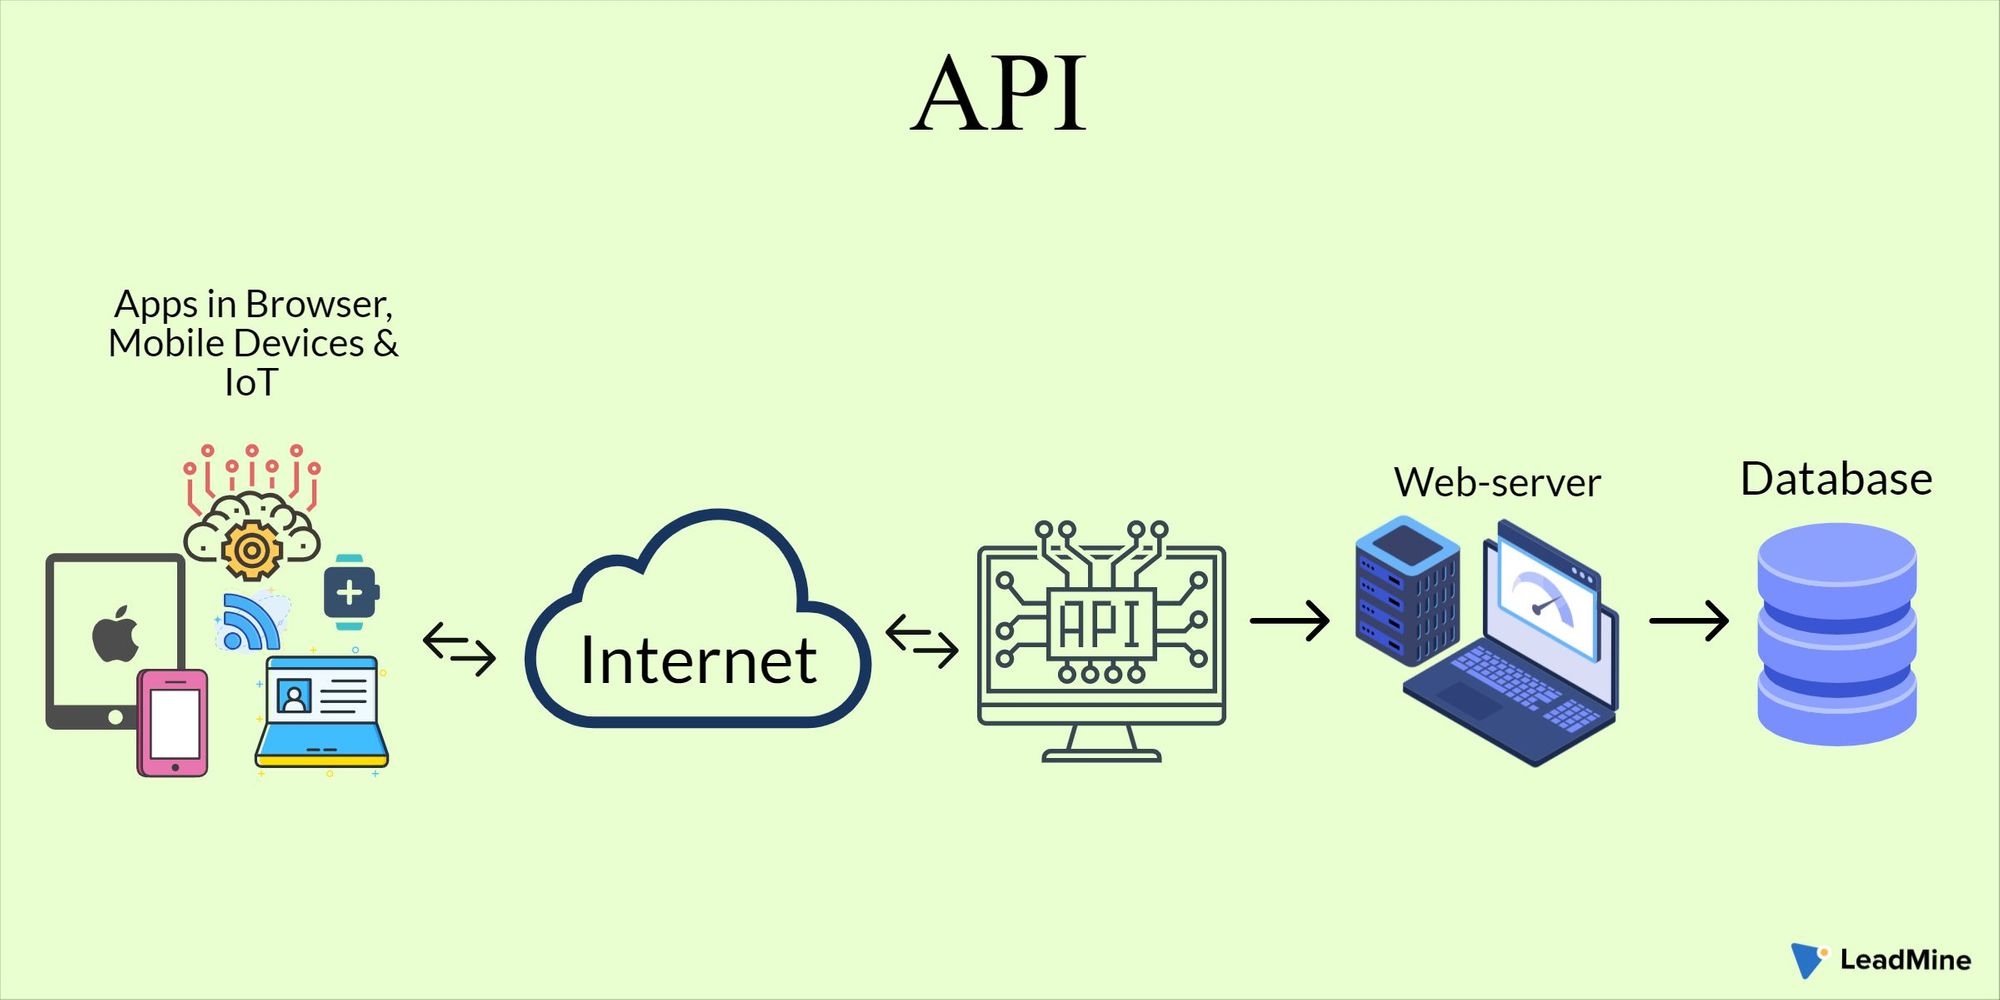
APIs serve as the backbone of modern insurance operations, enabling seamless data exchange across disparate systems while reducing manual intervention, latency, and human error. By automating workflows—such as underwriting, claims processing, and fraud detection—insurers leverage APIs to enhance accuracy, speed, and customer experience. The integration of external data sources (e.g., credit bureaus, medical records, IoT sensors) and third-party services (e.g., insurtech platforms, repair networks) further optimizes operational efficiency and risk assessment.The adoption of APIs transforms traditional insurance workflows into dynamic, real-time processes. For instance, underwriting no longer relies solely on static policy applications but incorporates live data validation from telematics devices, medical databases, or environmental risk models. Similarly, claims handling shifts from siloed internal systems to unified ecosystems where fraud detection, vendor coordination, and customer notifications occur in parallel. Below, key use cases demonstrate how APIs redefine efficiency in insurance operations, supported by comparative analyses, workflow visualizations, and industry examples.
Automation of Underwriting Through API-Driven Data Validation
Underwriting processes benefit significantly from API integrations that automate data validation from external sources, reducing approval times and improving risk accuracy. Insurers traditionally relied on manual data entry or batch processing, which introduced delays and inconsistencies. APIs now enable real-time access to structured and unstructured data, including:- Credit and financial data: APIs from bureaus (e.g., Experian, Equifax) validate credit scores, payment histories, and financial stability within seconds, replacing manual checks.
Example Workflow:
An API-driven underwriting process for an auto insurance quote might involve:
1. Customer submits application via insurer’s portal.
2. API calls to:
4. Approved quotes are pushed back to the customer portal with real-time explanations for pricing.
APIs reduce underwriting cycle times by 70–90% in cases involving real-time data validation, while error rates drop by 40–60% due to automated cross-referencing.
Comparative Efficiency: Standalone vs. Unified API Ecosystems for Claims Processing
The efficiency gains from API integration vary significantly between isolated systems and unified ecosystems. Below, a comparative analysis highlights the operational and customer experience advantages of a unified API approach, particularly in claims processing.| Metric | Standalone API (Claims Only) | Unified API Ecosystem (Claims + Fraud + Vendor Coordination) |
|---|---|---|
| Data Latency | High (manual handoffs between systems, e.g., claims → fraud team). | Low (real-time data sharing; e.g., fraud flags trigger vendor alerts instantly). |
| Processing Time | 3–7 days (sequential validation, approvals, and vendor coordination). | <1 day (parallel processing; e.g., repair vendor assigned while fraud check runs). |
| Error Rate | 15–25% (data silos lead to discrepancies in policy details, claim amounts). | <5% (single source of truth via API contracts; e.g., policy terms synced across systems). |
| Customer Satisfaction | Low (delays in updates, lack of transparency; e.g., "Your claim is under review"). | High (real-time notifications; e.g., "Your repair vendor has been booked—ETA: 48 hours"). |
| Cost per Claim | $50–$120 (manual labor, duplicate data entry, vendor coordination fees). | $10–$30 (automated workflows, reduced fraud losses, bulk vendor negotiations). |
| Fraud Detection Rate | 30–40% (reactive; e.g., post-payment audits). | 70–85% (proactive; e.g., API triggers for suspicious patterns in real time). |
| Vendor Utilization | 50–60% (idle time due to delayed assignments). | 90–95% (dynamic routing based on availability and proximity). |
Example Scenario:
A unified ecosystem for a property insurance claim might involve:
1. Policyholder files claim via mobile app → API call to policy management system for coverage validation.
2. Fraud detection API (e.g., LexisNexis) flags suspicious activity (e.g., duplicate claims) while vendor API (e.g., ServiceMaster) identifies nearby repair crews.
3. Claims adjuster API receives pre-populated damage assessment data from IoT sensors (e.g., smart home alerts for water leaks).
4. Approval triggers payment API to disburse funds and customer notification API to update the policyholder.
API-Driven Customer Journey: Policy Quote Request to Approval
The following flowchart describes the API-mediated path for a customer requesting a policy quote, illustrating how external integrations streamline each step. While a visual diagram would depict this, the text below outlines the sequential API interactions:1. Customer Input:
2. Risk Assessment:
3. Pricing Engine:
4. Data Validation:
5. Approval Workflow:
6. Policy Issuance:
Critical API Contracts and SLAs:
Challenges and Solutions in API-Based Insurance Systems
The integration of APIs in insurance digital transformation introduces both operational efficiencies and complex technical and regulatory obstacles. Cross-border data flows, legacy system interoperability, and compliance with region-specific regulations—such as GDPR in the EU, CCPA in California, or the Personal Information Protection Law (PIPL) in China—create friction points that require tailored solutions. Additionally, ensuring backward compatibility during API versioning and mitigating failure risks (e.g., latency, data inconsistency) demands structured governance and monitoring frameworks. This section examines the key challenges, region-specific mitigation strategies, and best practices for sustainable API adoption in insurance ecosystems.Technical and Regulatory Hurdles in Cross-Border API Integration
APIs enable seamless data exchange across insurance markets, but their deployment across international jurisdictions introduces multifaceted challenges. Legacy system constraints pose a significant barrier, as many insurers rely on monolithic architectures built decades ago, lacking native API support. These systems often require middleware or custom adapters to interface with modern cloud-based APIs, increasing latency and operational overhead.Regulatory compliance further complicates cross-border integration. For instance:
Solutions include:
For insurers operating in APAC, additional considerations arise:
API Versioning Best Practices for Backward Compatibility in Insurance
API versioning ensures smooth transitions during policy updates, system migrations, or vendor changes, but improper versioning can lead to breaking changes that disrupt workflows. Insurers must adopt a strategic versioning model that balances innovation with stability. Below is a checklist for versioning APIs in insurance environments:Core Principles for Insurance API Versioning:Implementation Example:
1. Semantic Versioning (SemVer) – Use `MAJOR.MINOR.PATCH` to signal compatibility:
`MAJOR`: Breaking changes (e.g., removing a claims API endpoint). `MINOR`: Backward-compatible additions (e.g., new field in policy response). `PATCH`: Bug fixes (e.g., correcting a rate calculation error). 2. Deprecation Policies – Provide 12–18 months of notice before sunsetting versions to allow partners to migrate.
3. Versioned Endpoints – Enforce `/v1/policies` and `/v2/policies` to avoid conflicts.
4. Feature Flags – Roll out new features behind flags (e.g., `?enable=underwriting_v2`) to test in production without version bumps.
5. Schema Evolution – Use JSON Schema or OpenAPI to document changes and enforce backward compatibility (e.g., adding optional fields).
An insurer upgrading its underwriting API from `v1` to `v2` might:
Common Pitfalls to Avoid:
Common API Failure Points in Insurance and Proactive Monitoring Tools
API failures in insurance can lead to financial losses, regulatory penalties, or customer churn, particularly in high-stakes workflows like claims processing or fraud detection. Below is a comparative table of failure points, their root causes, and monitoring tools to mitigate risks:| Failure Point | Root Cause | Impact | Proactive Monitoring Tool | |||||||||||||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
| Latency in Claims APIs |
|
|
|
|||||||||||||||||||||||||||||||
| Data Inconsistency Across Systems |
|
|
|
|||||||||||||||||||||||||||||||
| Authentication/Authorization Failures |
|
|
|
|||||||||||||||||||||||||||||||
Third-Party API Dependencies
Future Trends: APIs and the Next Generation of InsuranceThe insurance industry is undergoing a paradigm shift driven by APIs, which are evolving from static data connectors to dynamic, intelligent systems enabling real-time interactions and decentralized models. Emerging trends such as event-driven architectures, real-time API orchestration, and Web3 integrations are redefining underwriting, claims processing, and customer engagement. This section explores the technical and strategic advancements shaping the next decade of API-driven insurance, including implementation frameworks, ROI evaluation, and a historical timeline of API adoption correlated with technological milestones.Real-Time API Orchestration and Dynamic PricingReal-time API orchestration leverages microservices and event-driven architectures to dynamically adjust pricing, risk assessments, and policy terms based on live data streams. Insurers now integrate APIs with IoT sensors, telematics, and third-party risk datasets to enable context-aware pricing models, where premiums fluctuate in response to real-time driver behavior, weather conditions, or asset location.Key Mechanisms: Implementation Example (Node.js with AWS Lambda): // Lambda function for real-time telematics-based pricing adjustment // Update policy via API return { Use Case: A commercial auto insurer uses event-driven APIs to adjust premiums hourly for delivery trucks based on GPS data, reducing claims by 18% (source: McKinsey, 2022). Event-Driven APIs for Instant Claims Notifications and Automated WorkflowsEvent-driven APIs eliminate silos between insurers, brokers, and third-party services (e.g., repair shops, medical providers) by pushing real-time notifications and automating claim adjudication. This reduces processing time from days to minutes and enhances transparency for policyholders.Architectural Components: Example Workflow (Health Insurance Claim Processing): Performance Impact: Web3 APIs and Decentralized Insurance ModelsWeb3 APIs are enabling decentralized insurance (DeFi) models where smart contracts automate underwriting, claims, and payouts without intermediaries. Key technical prerequisites include wallet APIs, oracle services, and blockchain interoperability layers.Core Components: Pilot Use Cases: Technical Prerequisites for Implementation:
Timeline: API Adoption in Insurance (2014–2030)APIs in insurance have evolved alongside broader technological shifts, from SOAP-based legacy integrations to AI-augmented, event-driven architectures. Below is a decade-by-decade breakdown correlating API trends with industry advancements.
APIs are not merely tools for integration but the foundation of a new insurance paradigm—one where agility, transparency, and customer-centricity define success. By leveraging real-time data flows, insurers can dynamically adjust policies, mitigate fraud, and deliver personalized services at unprecedented speeds. The future belongs to those who treat APIs as strategic assets, investing in secure, scalable, and future-proof architectures. As digital transformation accelerates, the insurers who master API-driven integration will redefine industry standards, turning operational complexity into competitive advantage. |
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.