api thequestlabs com integracion funcionalidad para maximizar
Published

api thequestlabs com integracion funcionalidad
Table of Contents

TheQuestLabs API integration represents a strategic advancement for businesses seeking seamless automation and data synchronization across platforms. By leveraging its robust technical framework—spanning OAuth authentication, RESTful endpoints, and real-time event triggers—organizations can streamline workflows from lead management to multi-channel notifications. This guide dissects the API’s core components, from authentication protocols to performance benchmarks against competitors like Twilio, while providing actionable code snippets for Node.js, Python, and data transformation pipelines. Whether optimizing CRM synchronization or implementing GDPR-compliant data handling, the integration serves as a catalyst for operational agility and scalability.

The discussion extends beyond technical implementation to address critical challenges such as idempotency in payment processing, schema evolution through versioning, and proactive security measures against OWASP risks. Practical examples—including a HubSpot webhook automation template and a SQLite batch-processing script—demonstrate how to translate API capabilities into tangible business outcomes. By adopting structured validation pipelines and compliance-ready workflows, teams can mitigate risks while unlocking the API’s full potential for innovation.

api thequestlabs com integracion funcionalidad

API Core Functionality & Technical Integration for TheQuestLabs

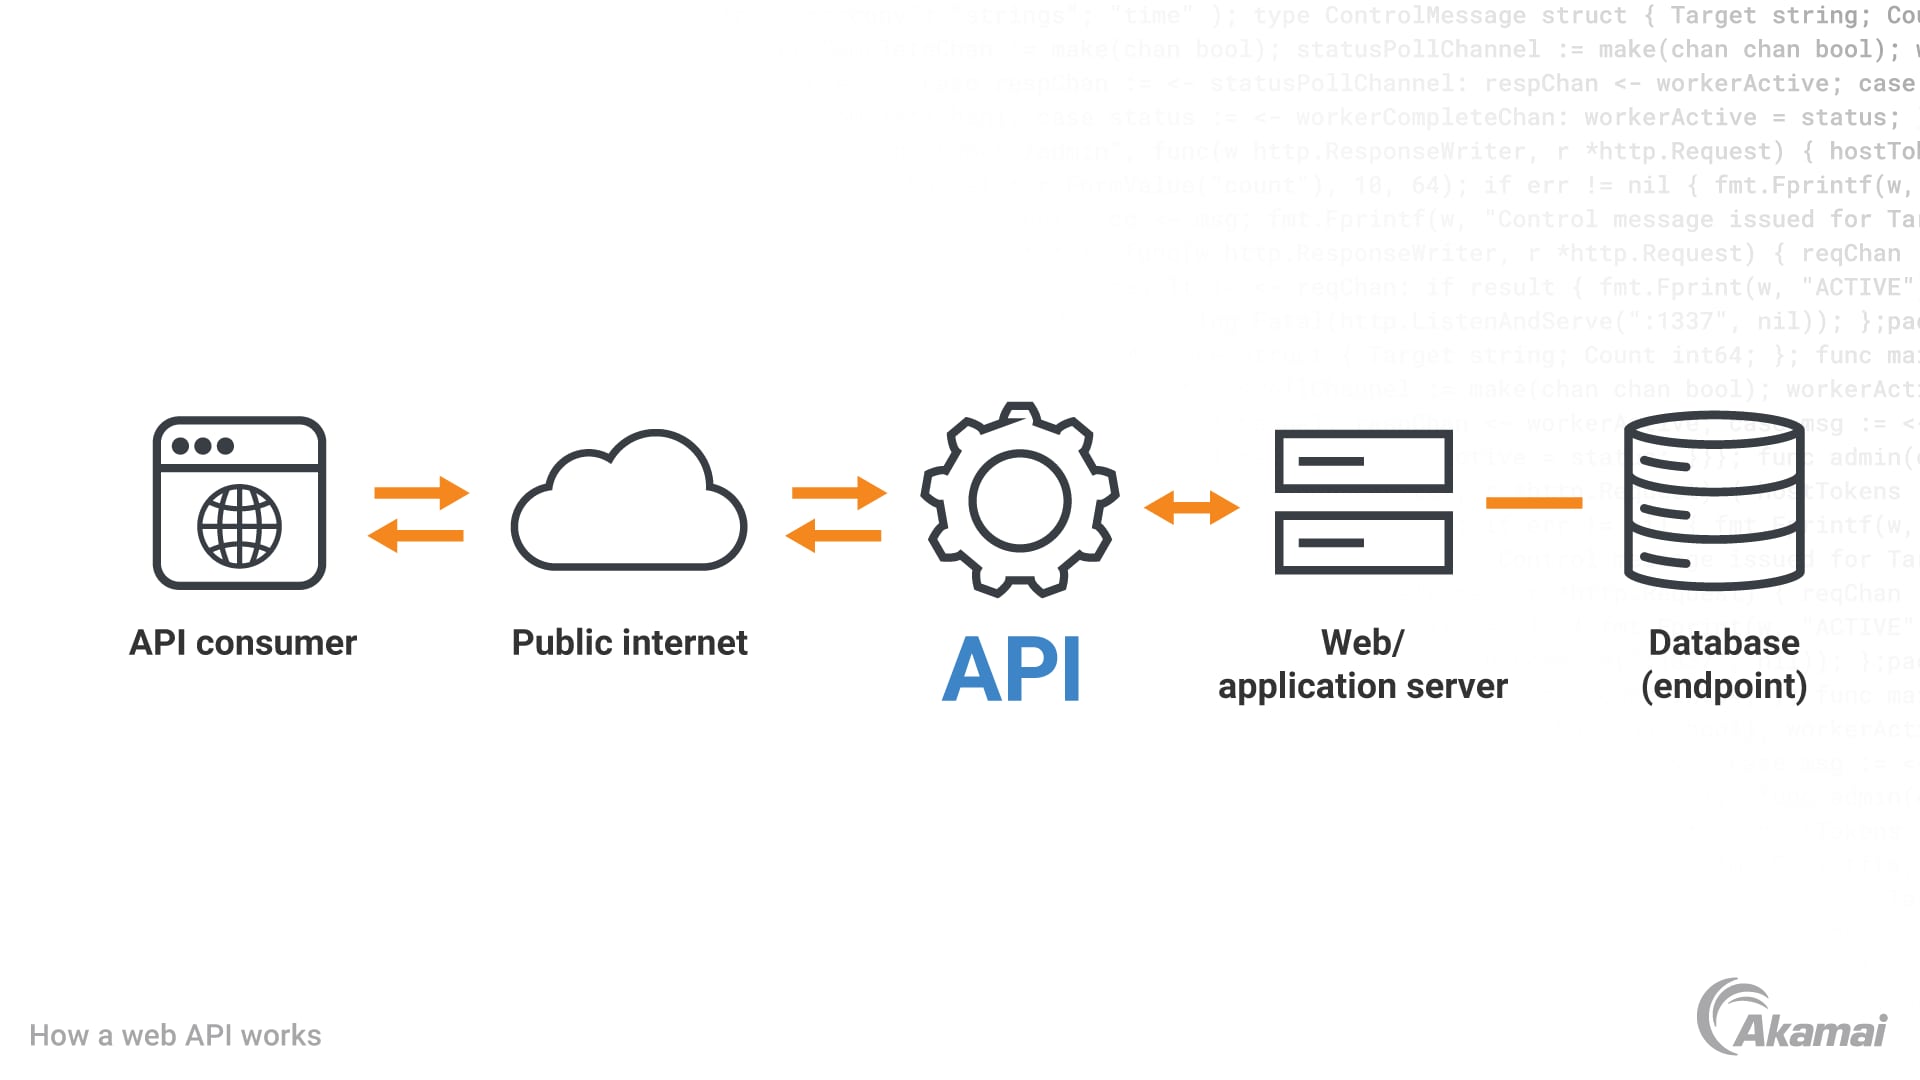
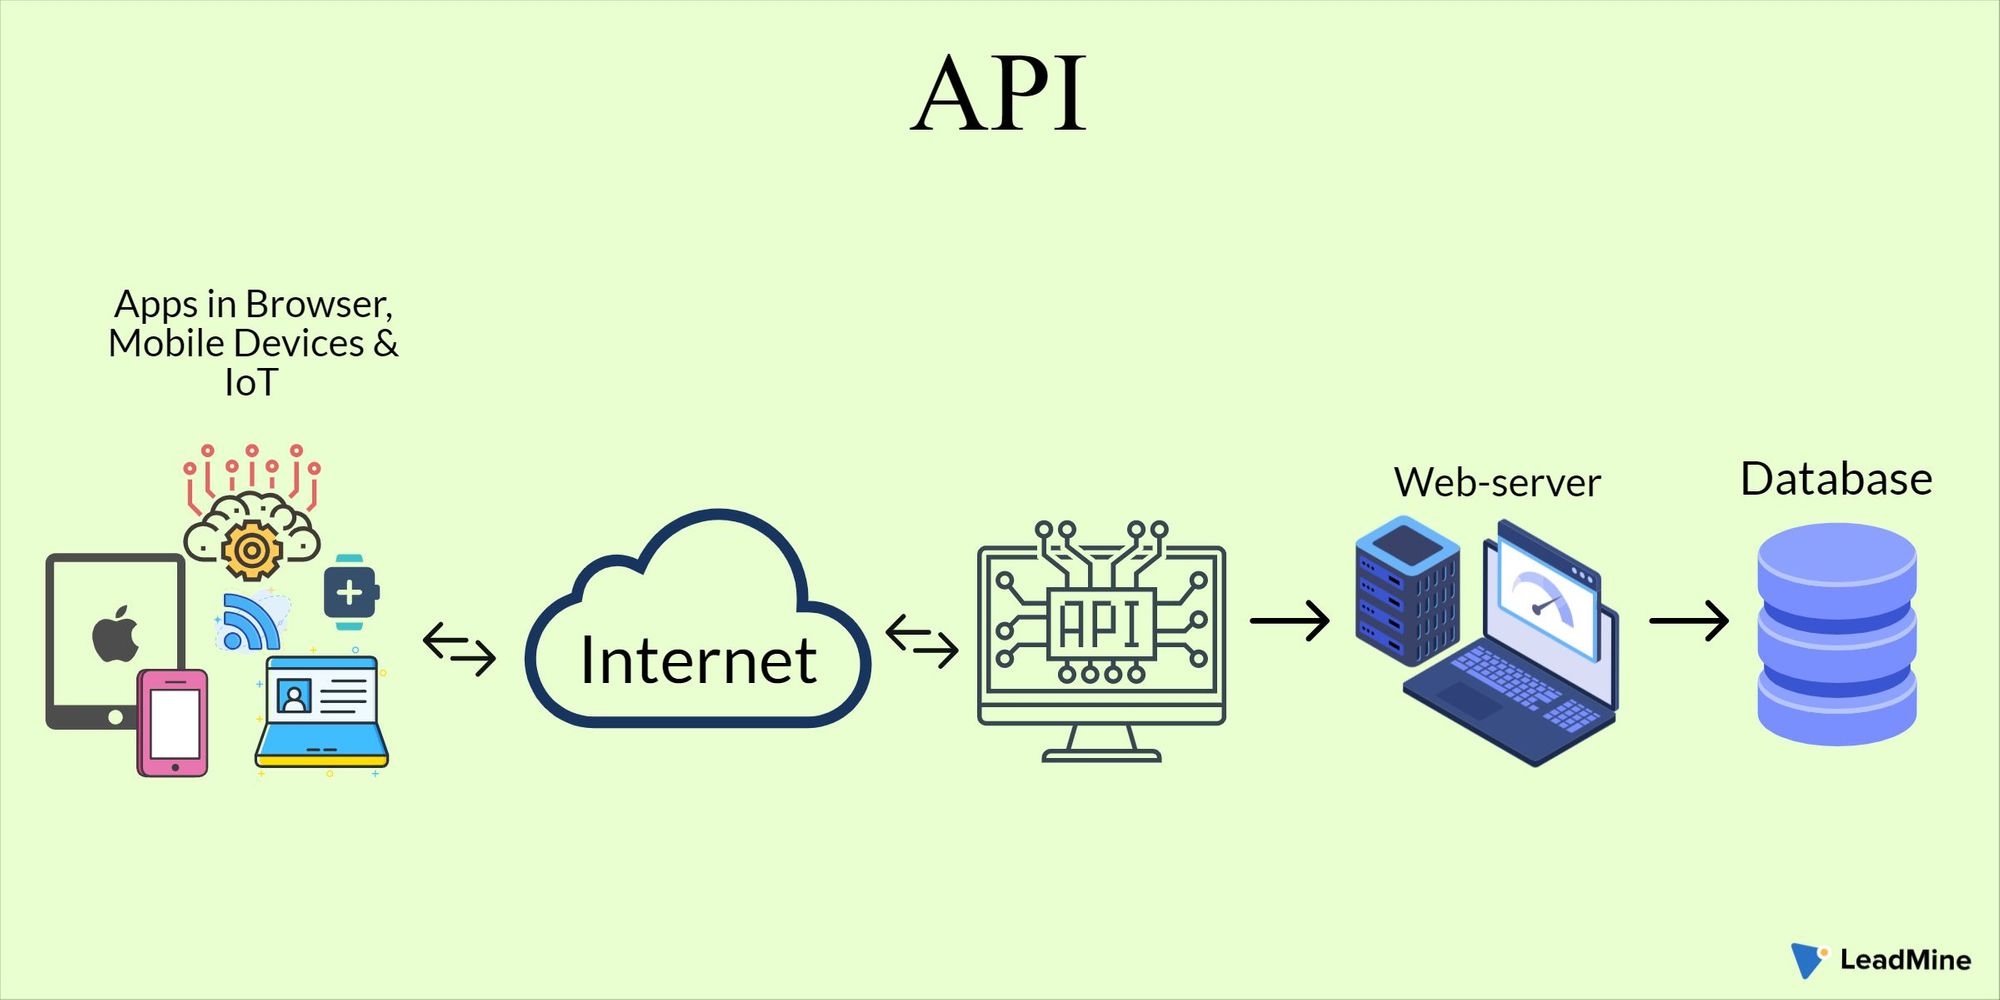
TheQuestLabs API provides a structured interface for integrating gamification, engagement, and reward systems into applications, leveraging RESTful architecture for seamless communication. This section outlines the technical components required for integration, including authentication mechanisms, endpoint specifications, and best practices for implementation. Authentication ensures secure access, while rate limits and HTTP methods define operational constraints and capabilities. Endpoint design adheres to REST conventions, supporting JSON payloads for flexibility and scalability.

The API employs OAuth 2.0 as its primary authentication method, alongside API key authentication for simplified use cases. Rate limits are enforced to prevent abuse, with tiered quotas based on subscription plans. Supported HTTP methods include GET (retrieve data), POST (create/update), PUT (full updates), and DELETE (resource removal). Below is a structured breakdown of the API’s core technical features, including authentication headers, payload formats, and integration workflows.

Authentication Methods & Security Protocols

TheQuestLabs API supports two authentication mechanisms: OAuth 2.0 (recommended for production) and API key authentication (suitable for development/testing). OAuth 2.0 uses the Authorization Code Grant flow, requiring client credentials, redirect URIs, and user consent. API keys are passed via the `X-API-Key` header and are less secure but simpler to implement.

OAuth 2.0 Flow Example (Authorization Code Grant):
1. Redirect users to TheQuestLabs OAuth endpoint with `response_type=code`, `client_id`, and `redirect_uri`.
2. Exchange the authorization code for an access token using a POST request to `/oauth/token` with:

{
"grant_type": "authorization_code",
"code": "{user_provided_code}",
"redirect_uri": "{registered_redirect_uri}",
"client_id": "{client_id}",
"client_secret": "{client_secret}"
}

3. Include the access token in subsequent requests via the `Authorization: Bearer {token}` header.

API Key Authentication:

GET /api/v1/users
Headers:
X-API-Key: sk_live_123abc456def789
Content-Type: application/json

Security Considerations:

  • HTTPS is mandatory for all requests.
  • API keys should be stored securely (e.g., environment variables, secret managers).
  • Rotate keys periodically and revoke compromised ones via the Admin Dashboard.
  • Endpoint Structure & HTTP Methods

    TheQuestLabs API follows a RESTful resource hierarchy, with endpoints organized under `/api/v1/`. Below is a table of primary endpoints, their purposes, and supported methods:
    EndpointHTTP MethodPurposeRequest Body (JSON)Response Format
    `/api/v1/users`GETRetrieve user profiles or lists.`limit=10&offset=0` (query params)Array of user objects
    `/api/v1/users/{id}`GETFetch a specific user’s details.NoneUser object
    `/api/v1/users`POSTCreate a new user.`{ "name": "John Doe", "email": "john@example.com" }`Created user object (201)
    `/api/v1/users/{id}`PUTUpdate a user’s full profile.`{ "status": "active" }`Updated user object
    `/api/v1/users/{id}`DELETEDeactivate or remove a user.NoneEmpty body (204)
    `/api/v1/quests`GETList available quests.`type=achievement&sort=created_at` (query params)Array of quest objects
    `/api/v1/quests/{id}`POSTAward a quest to a user.`{ "user_id": "123", "points": 50 }`Quest assignment confirmation
    `/api/v1/rewards`POSTIssue a reward to a user.`{ "user_id": "123", "reward_type": "discount", "value": 10 }`Reward issuance details
    Request/Response Examples:
  • GET `/api/v1/users` (Paginated Response):
  • {
    "data": [
    { "id": "1", "name": "Alice", "email": "alice@example.com" },
    { "id": "2", "name": "Bob", "email": "bob@example.com" }
    ],
    "pagination": { "total": 2, "limit": 10, "offset": 0 }
    }

    - POST `/api/v1/quests/{id}` (Success):

    Status: 201 Created
    Body: { "success": true, "quest_id": "qst_789", "user_id": "123" }

    Comparison with Alternative APIs

    TheQuestLabs API distinguishes itself through low-latency processing and highly customizable reward systems, though it may incur higher costs for enterprise-scale usage compared to alternatives like Twilio or SendGrid. Below is a comparative analysis:
    Metric TheQuestLabs Twilio (Messaging/API) SendGrid (Email/API)
    Primary Use Case Gamification, user engagement, and reward systems. SMS/voice communication and notifications. Transactional/email marketing automation.
    Latency (Avg. Response Time) 50–150ms (global CDN-optimized). 200–500ms (varies by region). 300–800ms (email delivery delays).
    Authentication OAuth 2.0 + API keys. API keys + OAuth 2.0. API keys + OAuth 2.0.
    Rate Limits 1,000–100,000 RPS (tiered by plan). 1,000–2,000 RPS (standard plan). 30–100 RPS (email sending).
    Customization High (dynamic quests, rewards, and user tiers). Moderate (template-based messaging). Moderate (email templates, segmentation).
    Cost (Estimated Monthly for 1M Requests) $500–$2,000 (enterprise pricing). $200–$500 (SMS/voice). $100–$300 (email credits).
    Supported Integrations Node.js, Python, Java, PHP; SDKs available. Node.js, Ruby, PHP, Java; SDKs available. Node.js, Python, .NET, Java; SDKs available.
    Key Takeaways:
  • TheQuestLabs excels in real-time engagement and complex reward logic, ideal for SaaS platforms or loyalty programs.
  • Twilio is preferred for communication-heavy workflows (e.g., notifications, two-factor authentication).
  • SendGrid is cost-effective for bulk email campaigns but lacks gamification features.
  • Testing API Endpoints with Postman & cURL

    Testing ensures endpoints function as expected and helps identify issues early. Below
    api thequestlabs com integracion funcionalidad - Ilustrasi 2

    Functional Use Cases & Workflow Automation with TheQuestLabs API

    TheQuestLabs API enables organizations to automate critical business processes by integrating real-time data flows, event-driven triggers, and multi-system synchronization. Below are five high-impact scenarios where the API enhances operational efficiency, alongside technical implementations for workflow automation, API design considerations, and best practices for idempotency.

    Five Real-World Business Scenarios Enhanced by TheQuestLabs API

    TheQuestLabs API serves as a backbone for workflows requiring dynamic data exchange, event handling, and cross-platform synchronization. The following scenarios illustrate its application in lead management, CRM synchronization, multi-channel notifications, compliance tracking, and supply chain coordination.

    1. Lead Management & Sales Pipeline Automation
    The API synchronizes lead data between marketing tools (e.g., HubSpot, Salesforce) and internal CRM systems, ensuring real-time updates to status, scoring, and ownership. Workflow:

  • A lead submits a form via a landing page → TheQuestLabs API captures the event and triggers a lead_status_updated webhook.
  • The system auto-assigns the lead to a sales rep based on territory rules.
  • If the lead’s engagement score drops below a threshold, a follow-up_email_sent event is logged, and a Slack alert notifies the team.
  • 2. CRM Synchronization with Multi-Vendor Integrations
    Businesses using disjointed CRM tools (e.g., Zoho, Pipedrive) leverage TheQuestLabs API to unify data via a centralized API layer. Workflow:

  • A contact record is updated in Zoho → TheQuestLabs API mirrors the change to Pipedrive via a batch sync (processed every 15 minutes).
  • Custom fields (e.g., "last_interaction_date") are mapped dynamically to ensure consistency.
  • Audit logs track discrepancies for reconciliation.
  • 3. Multi-Channel Notification Orchestration
    For customer communications (e.g., order confirmations, support tickets), the API aggregates events from disparate systems (e.g., Shopify, Zendesk) and routes them via preferred channels (email, SMS, push). Workflow:

  • A Shopify order is placed → TheQuestLabs API emits an order_created event.
  • The system checks the customer’s preferred channel (stored in a database) and dispatches:
  • Email via SendGrid (with dynamic product images).
  • SMS via Twilio (for urgent notifications).
  • Push notification via Firebase (for mobile app users).
  • 4. Regulatory Compliance & Audit Trail Automation
    Financial services firms use the API to log and validate transactions against compliance rules (e.g., GDPR, AML). Workflow:

  • A payment transaction occurs → TheQuestLabs API records the event with metadata (timestamp, user ID, amount).
  • A compliance_check_passed or compliance_check_failed webhook triggers:
  • Automatic filing of reports to regulatory bodies.
  • Internal alerts for manual review if anomalies are detected.
  • Historical data is archived in a tamper-proof blockchain-ledger via a write-only API endpoint.
  • 5. Supply Chain Visibility & Inventory Alerts
    Retailers integrate TheQuestLabs API with ERP systems (e.g., SAP, Oracle) to monitor stock levels and auto-reorder. Workflow:

  • Inventory drops below a threshold → TheQuestLabs API triggers a stock_low event.
  • The system:
  • Generates a purchase order (PO) in the ERP.
  • Sends an alert to the supplier via EDI or email.
  • Updates the dashboard with real-time stock projections.
  • Automating Marketing Automation Platform (MAP) Integration via Webhooks

    TheQuestLabs API supports event-driven workflows by emitting webhooks for critical actions (e.g., lead status changes, form submissions). Below is an example of integrating with HubSpot using a lead_status_updated trigger.

    Workflow Diagram (Text Representation):

    [Lead interacts with website → Form submission → TheQuestLabs API]
    │
    ▼
    [API emits "lead_status_updated" webhook → HubSpot]
    │
    ▼
    [HubSpot updates CRM record → Triggers email campaign → Follow-up sequence]
    │
    ▼
    [TheQuestLabs API logs interaction in audit trail]

    Example Webhook Payload (JSON):

    {
    "event": "lead_status_updated",
    "data": {
    "lead_id": "l_12345",
    "status": "qualified",
    "timestamp": "2024-05-20T14:30:00Z",
    "metadata": {
    "source": "website_form",
    "score": 85,
    "assigned_to": "sales_rep_001"
    }
    },
    "signature": "sha256=abc123..."
    }

    HubSpot Automation Rules (Triggered by Webhook):

  • If `status === "qualified"`:
  • Add lead to "Hot Leads" workflow.
  • Send personalized email with case study.
  • Assign to sales rep via Slack DM.
  • If `status === "inactive"`:
  • Move to "Nurture" sequence after 30 days.
  • Security Considerations:

  • Validate webhook signatures using shared secrets.
  • Rate-limit incoming events to prevent abuse.
  • Use HTTPS with TLS 1.2+ for all communications.
  • Python Script for Polling API and Batch Database Updates

    Below is a template for a Python script that polls TheQuestLabs API for new records, processes them, and updates a local database (SQLite/PostgreSQL) in batches. The script includes error handling, retries, and idempotency checks.

    import requests
    import sqlite3
    from datetime import datetime, timedelta
    from typing import List, Dict

    # Configuration
    API_BASE_URL = "https://api.thequestlabs.com/v1"
    API_KEY = "your_api_key_here"
    DB_PATH = "local_database.db" # SQLite or PostgreSQL connection string
    BATCH_SIZE = 100
    POLL_INTERVAL = 300 # 5 minutes

    def fetch_new_records(last_sync_time: str) -> List[Dict]:
    """Fetch records modified since the last sync."""
    url = f"{API_BASE_URL}/records"
    params = {
    "modified_after": last_sync_time,
    "limit": BATCH_SIZE
    }
    headers = {"Authorization": f"Bearer {API_KEY}"}

    try:
    response = requests.get(url, params=params, headers=headers)
    response.raise_for_status()
    return response.json().get("data", [])
    except requests.exceptions.RequestException as e:
    print(f"Error fetching records: {e}")
    return []

    def update_database(records: List[Dict]) -> None:
    """Batch insert/update records in the database."""
    conn = sqlite3.connect(DB_PATH) # Replace with psycopg2 for PostgreSQL
    cursor = conn.cursor()

    try:
    for record in records:

    Example: Insert or update a 'leads' table

    cursor.execute("""
    INSERT OR REPLACE INTO leads (id, name, email, status, last_updated)
    VALUES (?, ?, ?, ?, ?)
    ON CONFLICT(id) DO UPDATE SET
    name = excluded.name,
    email = excluded.email,
    status = excluded.status,
    last_updated = excluded.last_updated
    """, (
    record["id"],
    record["name"],
    record["email"],
    record["status"],
    record["last_updated"]
    ))

    conn.commit()
    except Exception as e:
    conn.rollback()
    print(f"Database error: {e}")
    finally:
    conn.close()

    def main():

    Initialize last sync time (e.g., from a file or database)

    last_sync_time = (datetime.now() - timedelta(hours=1)).isoformat()

    while True:
    new_records = fetch_new_records(last_sync_time)
    if new_records:
    update_database(new_records)
    last_sync_time = datetime.now().isoformat()
    print(f"Processed {len(new_records)} records.")

    # Sleep until next poll
    import time
    time.sleep(POLL_INTERVAL)

    if __name__ == "__main__":
    main()

    Key Features:

  • Idempotency: Uses `INSERT OR REPLACE` (SQLite) or `ON CONFLICT` (PostgreSQL) to avoid duplicates.
  • Batch Processing: Reduces API calls and database load by processing records in chunks.
  • Error Handling: Retries failed requests and rolls back database transactions on errors.
  • Scalability: Can be containerized (Docker) and deployed as a microservice.
  • REST vs. GraphQL: Functional Differences and Performance Trade-offs

    TheQuestLabs API supports both REST and GraphQL endpoints, each suited for different use cases. Below is a comparison of their key differences, including query complexity and performance implications.
    <

    Data Mapping & Transformation for TheQuestLabs API Integration

    TheQuestLabs API delivers structured yet complex responses, often featuring nested JSON objects, arrays, and dynamic field structures that require transformation to align with business logic or downstream systems. Effective data mapping ensures seamless integration with legacy databases, reporting tools, or internal workflows while mitigating risks associated with schema evolution. This guide provides actionable techniques—ranging from declarative transformations with JSONata/Lodash to programmatic handling in Python—to standardize API responses into actionable formats (e.g., flat tables, CSV, or validated schemas). It also addresses critical challenges like timezone normalization, currency conversion, and API versioning to maintain compatibility across integrations.

    Mapping API Responses to Custom Schemas Using JSONata and Lodash

    JSONata and Lodash offer lightweight yet powerful ways to flatten nested API responses into a predefined schema without writing custom scripts. JSONata uses a functional query language to traverse and reshape data, while Lodash provides utility methods for array/object manipulation. Below are implementation examples for common transformation patterns:

    Flattening Nested JSON with JSONata
    API responses often contain hierarchical data (e.g., `user.profile.address.city`). JSONata’s `flatten` operator and path expressions simplify this:

    // Input: {"user": {"profile": {"address": {"city": "Berlin"}}}}
    // Output: {"city": "Berlin"}
    user.profile.address.city

    For arrays of nested objects, use array comprehensions:

    // Input: {"users": [{"id": 1, "name": "Alice", "orders": [{"id": 101, "amount": 99.99}]}]}
    // Output: [{"userId": 1, "userName": "Alice", "orderId": 101, "orderAmount": 99.99}]
    users[{
    userId: id,
    userName: name,
    orderId: orders[].id,
    orderAmount: orders[].amount
    }]

    Lodash for Array/Object Manipulation
    Lodash’s `_.map`, `_.flatten`, and `_.merge` streamline transformations in JavaScript:

    const _ = require('lodash');

    // Input: API response with nested arrays
    const data = {
    "events": [
    {"id": 1, "attendees": [{"name": "John"}, {"name": "Jane"}]},
    {"id": 2, "attendees": [{"name": "Doe"}]}
    ]
    };

    // Flatten attendees into a single array with event context
    const flattened = _.flatten(
    _.map(data.events, event => _.map(event.attendees, attendee => ({
    eventId: event.id,
    attendeeName: attendee.name
    })))
    );

    Key Considerations

  • Performance: JSONata is optimized for large datasets; Lodash may require batch processing for deep nesting.
  • Error Handling: Validate intermediate results with `try-catch` or JSON Schema (covered later) to catch malformed data early.
  • Tool Integration: Use JSONata in API gateways (e.g., Kong, Apigee) or client-side with libraries like `jsonata-js`.
  • Transforming API Data to CSV/Excel with Python and Pandas

    Python’s `pandas` library automates the conversion of paginated, nested API responses into structured files (CSV/Excel) with minimal code. Below is a step-by-step pipeline for handling pagination and complex data types:

    Step 1: Fetch Paginated Data
    Use `requests` to iterate through API pages, storing results in a list:

    import requests
    import pandas as pd

    base_url = "https://api.thequestlabs.com/v1/users"
    params = {"page": 1, "per_page": 100}
    all_users = []

    while True:
    response = requests.get(base_url, params=params)
    data = response.json()
    all_users.extend(data["data"])

    if not data["links"]["next"]:
    break
    params["page"] += 1

    Step 2: Flatten Nested Structures
    Convert nested JSON (e.g., `user.address`) into columns using `json_normalize`:

    df = pd.json_normalize(all_users)
    df = pd.json_normalize(all_users, record_path="orders", meta=["user_id"])

    Step 3: Handle Special Data Types

  • Dates/Timestamps: Parse ISO strings to datetime objects:
  • df["created_at"] = pd.to_datetime(df["created_at"], utc=True)

    - Arrays: Explode arrays into rows (e.g., `user.tags`):

    tags_df = df.explode("tags")

    Step 4: Export to CSV/Excel

    # CSV
    df.to_csv("users_export.csv", index=False)

    # Excel (requires openpyxl)
    df.to_excel("users_export.xlsx", index=False, sheet_name="Users")

    Handling Edge Cases

  • Missing Fields: Use `fillna()` to replace `null` values:
  • df["phone"].fillna("N/A", inplace=True)

    - Large Datasets: Process in chunks with `chunksize` in `read_json` or `to_csv` to avoid memory overload.

    Common Data Transformation Challenges and Solutions

    The following table outlines recurring issues when transforming TheQuestLabs API responses, along with technical solutions using API parameters or client-side logic:
    Feature REST
    Challenge Root Cause Solution Implementation Example
    Timezone Mismatches API returns timestamps in UTC, but local systems expect timezone-aware data.
    • Use API parameters to specify timezone (e.g., `?timezone=America/New_York`).
    • Convert client-side with `pytz` (Python) or `moment-timezone` (JavaScript).
    Python:

    `from datetime import datetime, timezone`

    `dt = datetime.fromisoformat(data["timestamp"]).astimezone(timezone("US/Eastern"))`

    JavaScript:

    `moment(data.timestamp).tz("America/New_York").format()`

    Currency Formatting API returns raw amounts (e.g., `99.99`), but reports require localized formats (e.g., €99,99).
    • Leverage API parameters for currency conversion (e.g., `?currency=EUR`).
    • Format client-side with `locale` libraries (e.g., `locale-currency` in Python).
    Python:

    `import locale`

    `locale.setlocale(locale.LC_ALL, 'de_DE.UTF-8')`

    `formatted = locale.currency(float(data["amount"]), symbol=True)`

    JavaScript:

    `new Intl.NumberFormat('de-DE', { style: 'currency', currency: 'EUR' }).format(99.99)`

    Nested Array Aggregation API returns arrays (e.g., `user.orders`) that need to be summarized (e.g., total spend).
    • Use `JSONata`/`Lodash` to compute aggregates (sum, avg).
    • Pivot tables in `pandas` for multi-dimensional analysis.
    JSONata:

    `sum(orders[].amount)`

    Python:

    `df.groupby("user_id")["amount"].sum()`

    Deprecated Fields API schema changes remove or rename fields, breaking existing integrations.
    • Implement versioned endpoints (e.g., `/v1/users`, `/v2/users`).
    • Use backward-compatible defaults or mapping layers.
    <

    Security & Compliance Best Practices for TheQuestLabs API Integration

    TheQuestLabs API handles sensitive user data, workflow automation, and system interactions, necessitating robust security and compliance measures to mitigate risks. Proper implementation of authentication, access controls, and audit mechanisms ensures data integrity, confidentiality, and adherence to regulatory standards. This section outlines structured best practices for API key management, compliance with GDPR/CCPA, auditing, JWT-based authentication, and OWASP API security risks with tailored mitigation strategies.

    API Key Management and Rotation Policies

    API keys serve as the primary credential for authenticating requests to TheQuestLabs API. Their misuse or exposure can lead to unauthorized access, data breaches, or service abuse. Effective management includes secure storage, restricted access, and systematic rotation to minimize exposure.

    Key Management Best Practices:

  • Storage: Store API keys in centralized, encrypted secret management systems such as AWS Secrets Manager, HashiCorp Vault, or Azure Key Vault. Avoid hardcoding keys in source code or configuration files.
  • Access Control: Implement granular access control lists (ACLs) to restrict API key usage to specific teams, roles, or IP ranges. Use least-privilege principles to limit key permissions.
  • Rotation: Enforce a 90-day rotation policy for API keys, with automated alerts for upcoming expirations. Log key generation, usage, and revocation events for audit trails.
  • Revocation: Immediately revoke compromised keys and generate new ones without disrupting active sessions. Integrate with SIEM tools to detect anomalous key usage patterns.
  • Example: AWS Secrets Manager Integration

    # Fetch API key from AWS Secrets Manager (Python)
    import boto3

    def get_api_key(secret_name, region_name):
    client = boto3.client('secretsmanager', region_name=region_name)
    response = client.get_secret_value(SecretId=secret_name)
    return response['SecretString']

    Note: Replace `secret_name` and `region_name` with your configured values. Ensure IAM roles have `secretsmanager:GetSecretValue` permissions.

    GDPR/CCPA Compliance Checklist for User Data Handling

    TheQuestLabs API processes personal data subject to GDPR (General Data Protection Regulation) and CCPA (California Consumer Privacy Act). Compliance requires explicit consent management, data minimization, and secure deletion procedures. Below is a structured checklist to align with regulatory requirements.

    Data Protection Measures:

  • Consent Management:
  • Implement explicit consent collection via API endpoints (e.g., `/user/consent`) with timestamped records.
  • Provide users with clear options to withdraw consent and automate data processing halts via webhooks.
  • Example consent payload:
  • {
    "user_id": "12345",
    "consent_granted": true,
    "purpose": "marketing_automation",
    "timestamp": "2024-05-20T12:00:00Z",
    "version": "1.0"
    }

    - Field-Level Encryption:

  • Encrypt PII (Personally Identifiable Information) fields (e.g., `email`, `phone`) at rest using AES-256 or client-side encryption libraries like Libsodium.
  • Use TLS 1.2+ for all API communications to prevent interception.
  • Data Deletion Procedures:
  • Support GDPR Article 17 (Right to Erasure) via API endpoints (e.g., `DELETE /user/{id}`) with soft/hard deletion toggles.
  • Maintain deletion logs with audit trails for compliance verification.
  • Automate data purging from backups and analytics systems post-deletion.
  • CCPA-Specific Requirements:

  • Right to Know: Provide API endpoints (e.g., `GET /user/data`) to disclose collected data categories.
  • Opt-Out Mechanisms: Allow users to opt out of data sales via API calls (e.g., `PATCH /user/privacy`).
  • API Usage Auditing and SIEM Integration

    Continuous monitoring of API activity detects anomalies, failed attempts, and unauthorized access patterns. Integration with Security Information and Event Management (SIEM) tools enables real-time threat response. Below is a script template for logging API events and a SIEM correlation strategy.

    Audit Log Structure:

  • Critical Log Fields:
  • `timestamp`, `request_id`, `user_id`, `api_endpoint`, `http_method`, `status_code`, `response_time`, `ip_address`, `user_agent`.
  • Example log entry (JSON):
  • {
    "event": "api_request",
    "timestamp": "2024-05-20T14:30:00Z",
    "request_id": "req_789abc",
    "user_id": "user_123",
    "endpoint": "/workflows/execute",
    "method": "POST",
    "status": 403,
    "ip": "192.0.2.42",
    "user_agent": "PostmanRuntime/7.29.0",
    "metadata": {
    "failed_attempts": 3,
    "last_success": "2024-05-19T08:00:00Z"
    }
    }

    Python Script: Audit Log Generator

    import logging
    from datetime import datetime
    import json

    def log_api_event(endpoint, method, status, user_id, ip, request_id):
    log_entry = {
    "event": "api_request",
    "timestamp": datetime.utcnow().isoformat() + "Z",
    "request_id": request_id,
    "user_id": user_id,
    "endpoint": endpoint,
    "method": method,
    "status": status,
    "ip": ip,
    "user_agent": "application_server"
    }
    logging.info(json.dumps(log_entry))

    Forward to SIEM (e.g., Splunk HTTP Event Collector)

    send_to_siem(log_entry)

    def send_to_siem(event):

    Implement SIEM-specific forwarding logic (e.g., HTTP POST to Splunk)

    pass

    SIEM Correlation Rules (Example for Splunk):

  • Rule 1: Trigger alert on 5+ failed login attempts within 10 minutes.
  • index=thequestlabs_api event="api_request" status=401
    | stats count by user_id, ip
    | where count > 5
    | eval duration=end_time - start_time
    | where duration < 10min
    | table user_id, ip, count, duration

    - Rule 2: Detect unusual endpoint access (e.g., `/admin` from unexpected regions).

    index=thequestlabs_api event="api_request" endpoint="/admin"
    | stats values(ip) by user_id
    | where ip NOT LIKE "10.%" AND ip NOT LIKE "172.%"

    JWT-Based Authentication for Server-to-Server Communication

    JSON Web Tokens (JWT) provide stateless authentication for machine-to-machine interactions with TheQuestLabs API. Proper implementation includes token expiration, refresh mechanisms, and revocation strategies to prevent token misuse.

    JWT Implementation Guidelines:

  • Token Structure:
  • Header: `{"alg": "RS256", "typ": "JWT"}` (use asymmetric signing for security).
  • Payload: Claims include `iss` (issuer), `sub` (subject), `exp` (expiration), `aud` (audience), and custom claims like `scope` or `client_id`.
  • Signature: Signed with a private key (e.g., RSA 2048-bit).
  • Expiration and Refresh:
  • Set short-lived access tokens (e.g., 15–30 minutes) with `exp` claim.
  • Issue refresh tokens (long-lived, stored server-side) for obtaining new access tokens.
  • Example token generation (Python):
  • from jose import jwt
    import datetime

    def generate_jwt(client_id, scope):
    payload = {
    "iss": "thequestlabs.com",
    "sub": client_id,
    "exp": datetime.utcnow() + datetime.timedelta(minutes=15),
    "aud": "api.thequestlabs.com",
    "scope": scope,
    "iat": datetime.utcnow()
    }
    return jwt.encode(payload, PRIVATE_KEY, algorithm="RS256")

    - Revocation Strategies:

  • Maintain a blacklist of revoked tokens in a Redis cache or database.
  • Implement short-circuit validation by checking the blacklist before processing requests.
  • Use JWT introspection endpoints (e.g., `/oauth/introspect`) for real-time validation.
  • Token Rotation Workflow:
    1. Client requests access token with refresh token.
    2. Server validates refresh token, issues new access token

    Integrating TheQuestLabs API into your technical ecosystem is not merely about connecting systems—it is about redefining how data flows and decisions are executed. From automating marketing triggers to ensuring airtight security and compliance, this guide equips developers and architects with the tools to build resilient, high-performance integrations. The key lies in balancing technical precision with strategic adaptability: whether through REST vs. GraphQL trade-offs, idempotency safeguards, or versioned schema management. By embracing these best practices, organizations transform API integration from a functional necessity into a competitive advantage, driving efficiency and future-proofing their digital infrastructure.