What Does Cybersecurity Principles Do And Their Core Functions
Table of Contents
- Core Functions of Cybersecurity Principles in Digital Asset Protection
- Structured Breakdown of Cybersecurity Principles and Their Preventive Roles
- Comparative Analysis of Confidentiality, Integrity, and Availability
- Mitigation of Cyber Threats Through Cybersecurity Principles
- Implementation Methods in Systems and Networks
- Integration of Cybersecurity Principles into System Architectures
- Step-by-Step Implementation in Cloud-Based Infrastructures
- Securing IoT Devices Through Cybersecurity Principles
- Impact on Compliance and Regulatory Frameworks
- Alignment of Cybersecurity Principles with Regulatory Standards
- Case Study: Equifax’s Failure and Lessons in Regulatory Compliance
- Third-Party Vendor Assessments and Supply Chain Security
- Evolution and Adaptation in Modern Threat Landscapes
- AI-Driven Attacks and the Shift Toward Behavioral Analytics
- Ransomware-as-a-Service and the Rise of Automated Extortion
- Comparison of Traditional and Modern Cybersecurity Approaches
- Adapting Least Privilege and Defense in Depth for Hybrid Work
- Defense in Depth for Hybrid Networks
- Timeline of Key Milestones in Cybersecurity Principle Development
- Practical Applications in Incident Response and Recovery
- Procedural Steps for Applying Cybersecurity Principles in Incident Response
- Forensic Analysis Leveraging Cybersecurity Principles
- Best Practices for Disaster Recovery Planning Based on Cybersecurity Principles
- Cybersecurity Principles in Tabletop Exercises and Simulation Drills
- Visual and Descriptive Representations of Cybersecurity Principles
- Decision-Making Flowchart for Applying Cybersecurity Principles in a Breach Scenario
- Cybersecurity Principle Dashboard: Key Visual Elements
- Depiction of Cybersecurity Principles in Threat Modeling Diagrams
- Text-Based Illustration of a Secure System Architecture
Cybersecurity principles serve as the foundational pillars that safeguard digital ecosystems against escalating threats in an interconnected world. These principles—confidentiality, integrity, and availability—form the bedrock of trustworthy data protection, ensuring systems remain resilient against unauthorized intrusions, malicious exploits, and evolving attack vectors. Beyond theoretical frameworks, their practical implementation spans firewalls, encryption protocols, and compliance-driven architectures, directly shaping how organizations mitigate risks from phishing campaigns to AI-driven cyber warfare. By integrating these principles into system design, incident response strategies, and regulatory adherence, businesses not only fortify their defenses but also cultivate a culture of proactive security awareness.
Their relevance extends across industries, from cloud-based infrastructures to IoT networks, where adherence to standards like ISO 27001 and GDPR bridges operational security with legal compliance. Modern adaptations, such as zero-trust architectures and behavioral analytics, further demonstrate how these principles evolve to counter sophisticated threats like ransomware-as-a-service and insider breaches. Understanding their role in threat modeling, forensic analysis, and disaster recovery underscores why cybersecurity principles are indispensable in maintaining operational continuity and safeguarding critical assets in an era of relentless digital transformation.
Core Functions of Cybersecurity Principles in Digital Asset Protection
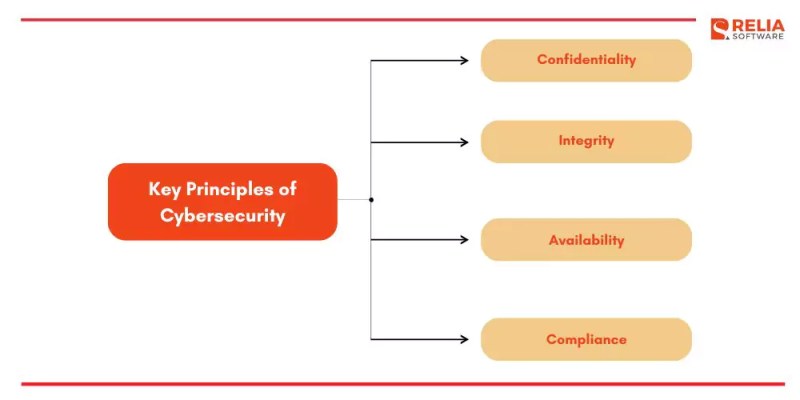
Cybersecurity principles serve as the foundational framework for safeguarding digital assets against evolving threats, ensuring resilience in an interconnected digital ecosystem. These principles—confidentiality, integrity, and availability—form the CIA Triad, a cornerstone of information security governance. Their implementation mitigates risks such as unauthorized data exposure, system corruption, and operational disruptions, aligning with regulatory compliance and organizational objectives. Below is a structured analysis of their roles, comparative breakdown, and real-world applications in threat mitigation.
Structured Breakdown of Cybersecurity Principles and Their Preventive Roles
The three core cybersecurity principles address distinct yet interdependent security objectives:
- Confidentiality ensures that sensitive information is accessible only to authorized entities, preventing unauthorized disclosure.
These principles collectively prevent unauthorized access, data breaches, and system disruptions by enforcing access controls, validation mechanisms, and redundancy protocols. For instance, confidentiality is enforced through encryption and role-based access control (RBAC), while integrity relies on checksums, digital signatures, and audit logs. Availability is maintained via failover systems, distributed storage, and denial-of-service (DoS) mitigation strategies.
The CIA Triad is not merely a theoretical model but a practical framework for designing, implementing, and maintaining security controls across industries, from healthcare to finance.
Comparative Analysis of Confidentiality, Integrity, and Availability
The following table contrasts the three principles, their objectives, and real-world examples illustrating their application:| Principle | Objective | Key Mechanisms | Real-World Example | Threat Mitigated |
|---|---|---|---|---|
| Confidentiality | Restrict data access to authorized users only. |
|
Healthcare: Patient records encrypted under HIPAA compliance, accessible only to medical staff via role-based permissions. | Unauthorized data leaks, insider theft, eavesdropping. |
| Integrity | Ensure data accuracy and prevent unauthorized modifications. |
|
Supply Chain: Blockchain-based tracking of pharmaceutical shipments to detect tampering with drug authenticity. | Data tampering, malware corruption, man-in-the-middle attacks. |
| Availability | Ensure systems and data are operational and accessible. |
|
E-Commerce: Amazon’s multi-region cloud infrastructure to maintain uptime during regional outages. | DoS attacks, hardware failures, natural disasters. |
Mitigation of Cyber Threats Through Cybersecurity Principles
Cybersecurity principles provide targeted defenses against common threats by addressing their root causes. Below is an analysis of how each principle counters specific risks:Malware and Ransomware Attacks
Malware exploits vulnerabilities to compromise integrity (e.g., encrypting files) and availability (e.g., locking systems). Mitigation strategies include:
Phishing and Social Engineering
Phishing targets confidentiality (e.g., credential theft) and integrity (e.g., fake invoices). Defenses involve:
Insider Threats
Insiders may violate confidentiality (data exfiltration) or availability (sabotage). Countermeasures include:
Insider threats account for 34% of breaches (Verizon DBIR 2023), underscoring the need for layered controls across all CIA principles.
Implementation Methods in Systems and Networks
Cybersecurity principles are not theoretical constructs but actionable frameworks that must be systematically integrated into system architectures to mitigate risks and ensure resilience. Their practical implementation—through firewalls, encryption, access controls, and network segmentation—transforms abstract defenses into tangible security postures. This section examines how these principles are embedded into modern infrastructures, with a focus on cloud-based environments and IoT ecosystems, where dynamic threats demand adaptive solutions.The effectiveness of cybersecurity measures hinges on their seamless integration into system design, operational workflows, and threat response protocols. Below, the discussion explores the methodological approaches for deploying core security controls, emphasizing procedural rigor and architectural alignment with zero-trust and least-privilege paradigms.
Integration of Cybersecurity Principles into System Architectures
Cybersecurity principles are embedded into system architectures through a defense-in-depth strategy, where multiple layers of controls—physical, technical, and administrative—work synergistically to neutralize vulnerabilities. Firewalls, encryption, and access controls serve as foundational pillars, each addressing distinct threat vectors while collectively enforcing a zero-trust model.Firewalls act as perimeter barriers by filtering traffic based on predefined rules (e.g., IP addresses, ports, or application protocols). Modern implementations include:
Encryption secures data in transit and at rest using symmetric (e.g., AES-256) or asymmetric (e.g., RSA) algorithms. Key management systems (KMS) ensure cryptographic keys are stored, rotated, and accessed securely. For example:
Access Controls restrict system interactions based on user identity, role, and contextual factors. Implementations include:
Defense-in-Depth Principle:
"Security should not rely on a single layer or control. Instead, multiple independent layers of defense should be deployed to ensure that if one layer is breached, others remain intact." — NIST SP 800-14, "Generally Accepted Principles and Practices for Securing Information Technology Systems"
Step-by-Step Implementation in Cloud-Based Infrastructures
Cloud environments introduce unique challenges, including shared responsibility models, dynamic scaling, and multi-tenancy risks. The following procedural steps outline a secure cloud deployment framework, adhering to principles like least privilege, immutable infrastructure, and continuous monitoring.1. Pre-Deployment Risk Assessment
2. Identity and Access Management (IAM) Configuration
3. Network Security Hardening
4. Data Protection and Encryption
5. Monitoring and Incident Response
Shared Responsibility Model (AWS Example):
"AWS secures the infrastructure (e.g., hypervisor, physical hardware), while customers secure their data, operating systems, and applications." — AWS Shared Responsibility Model
Securing IoT Devices Through Cybersecurity Principles
IoT devices—ranging from industrial sensors to smart home gadgets—pose significant security risks due to limited computational resources, lack of updates, and default credentials. The following steps outline a secure IoT deployment lifecycle, integrating principles like device authentication, firmware integrity, and network isolation.1. Device Hardening During Manufacturing
2. Network Segmentation and Isolation
3. Communication Security
4. Runtime Protection and Monitoring
IoT Security Best Practices (NIST IR 8259):
*"IoT devices should be designed with security as a primary consideration, not an afterthought
Impact on Compliance and Regulatory Frameworks
Cybersecurity principles serve as a foundational framework for organizations to align with global regulatory requirements, ensuring operational integrity and risk mitigation. Compliance with standards such as ISO 27001, NIST Cybersecurity Framework, and GDPR is not merely a legal obligation but a strategic imperative to safeguard digital assets, maintain stakeholder trust, and avoid financial or reputational penalties. These frameworks provide structured guidelines that cybersecurity principles directly support, bridging the gap between technical implementation and regulatory expectations. Below, the alignment of cybersecurity principles with key compliance standards is examined, alongside practical applications through case studies and third-party assessments.
Alignment of Cybersecurity Principles with Regulatory Standards
Cybersecurity principles such as confidentiality, integrity, availability (CIA triad), least privilege access, risk management, and continuous monitoring are explicitly embedded within major compliance frameworks. The following table compares core requirements of ISO 27001, NIST CSF, and GDPR with their corresponding cybersecurity principles, illustrating how adherence to these principles ensures regulatory alignment.
The table demonstrates that cybersecurity principles are not standalone technical measures but interdependent components of compliance strategies. Organizations leveraging these principles can systematically address regulatory demands while reducing audit burdens.
Regulatory Standard Key Requirement Corresponding Cybersecurity Principle Implementation Connection ISO 27001 Information Security Management System (ISMS) establishment Risk-based approach and governance Cybersecurity principles guide the development of an ISMS by prioritizing risks (e.g., asset classification, threat modeling) and integrating controls (e.g., access management, encryption). Data protection and breach response (Clause 16.1.6) Confidentiality, integrity, and availability (CIA) Principles like data encryption, access controls, and incident response plans directly address ISO 27001’s requirements for protecting information and responding to breaches. Supplier security assessments (Clause 15.2.3) Supply chain security and vendor risk management Principles such as third-party due diligence and contractual security clauses ensure vendors meet cybersecurity standards, mitigating supply chain risks. NIST Cybersecurity Framework (CSF) Identify risks through asset management (ID.AM) Asset inventory and classification Cybersecurity principles dictate systematic asset tracking (e.g., hardware/software catalogs) to align with NIST’s risk identification processes. Protect through access controls (PR.AC) Least privilege and multi-factor authentication (MFA) NIST’s protective measures rely on principles like role-based access control (RBAC) and MFA to limit unauthorized access. Detect anomalies via continuous monitoring (DE.CM) Real-time threat detection and logging Principles such as SIEM (Security Information and Event Management) and log analysis enable proactive detection as required by NIST. GDPR (General Data Protection Regulation) Data minimization and storage limitation (Article 5(1)(c)) Data retention policies and encryption Cybersecurity principles enforce data lifecycle management (e.g., automated deletion, encryption) to comply with GDPR’s data protection principles. Breach notification within 72 hours (Article 33) Incident response and transparency Principles like defined escalation protocols and stakeholder communication plans ensure timely breach reporting. Data subject rights (Article 15–22) Privacy by design and access controls Cybersecurity principles such as PII (Personally Identifiable Information) protection and consent management align with GDPR’s rights enforcement.
Case Study: Equifax’s Failure and Lessons in Regulatory Compliance
The 2017 Equifax data breach, exposing 147 million records, serves as a critical case study on the consequences of misaligned cybersecurity principles and regulatory non-compliance. The breach stemmed from:
Neglect of patch management (principle: system updates and vulnerability remediation). Inadequate access controls (principle: least privilege), allowing attackers to exploit unpatched Apache Struts software. Failure to encrypt sensitive data (principle: data protection), exacerbating the breach’s impact. Regulatory Fallout:
GDPR Fines: Equifax faced £500,000 fines (later reduced to £500,000 in 2020) under GDPR for inadequate breach notification and security measures. NIST CSF Shortfalls: Post-breach investigations revealed gaps in Identify (ID) and Protect (PR) functions, particularly in asset management and access controls. ISO 27001 Non-Compliance: Equifax’s lack of risk assessments and supplier security reviews violated ISO 27001’s Annex A controls. Corrective Actions Implemented:
Equifax subsequently adopted:
Automated patch management (aligned with NIST PR.PT). Zero-trust architecture (enforcing least privilege, per NIST PR.AC). Data encryption and tokenization (complying with GDPR’s data protection requirements). Third-party risk assessments (ISO 27001 Clause 15.2.3). Key Insight:
The breach highlighted that cybersecurity principles are not optional but mandatory for regulatory adherence. Organizations must integrate these principles into governance, risk management, and compliance (GRC) frameworks to avoid penalties and operational disruptions.
Third-Party Vendor Assessments and Supply Chain Security
Cybersecurity principles extend beyond internal systems to third-party vendors and supply chains, where risks often originate from weak links in the ecosystem. Regulatory frameworks increasingly mandate vendor security evaluations, as evidenced by:
ISO 27001 (Clause 15.2.3): Requires organizations to assess suppliers’ cybersecurity posture, including contractual security obligations and audit rights. NIST SP 800-161 (Supply Chain Risk Management): Advocates for vendor risk scoring and continuous monitoring of third-party security controls. GDPR (Article 28): Imposes joint controller responsibilities on vendors handling personal data, necessitating data protection agreements (DPAs). Implementation Methods for Vendor Security:
Cybersecurity principles guide vendor assessments through:
1. Pre-Engagement Due Diligence
Principle: Risk assessment and asset inventory. Action: Conduct security questionnaires (e.g., SOC 2, ISO 27001 certifications) and penetration testing of vendor systems. Example: A fintech company requires vendors to undergo NIST SP 800-53 assessments before processing transactions. 2. Contractual Security Clauses
Principle: Access control and accountability. Action: Enforce strict data handling terms, including encryption requirements, breach notification timelines, and right to audit. Example: A healthcare provider’s vendor contracts mandate HIPAA-compliant access logs and quarterly security reviews. 3. Continuous Monitoring and Incident Response
Principle: Real-time threat detection and transparency. Action: Implement SIEM integration for vendor networks and shared incident response plans. Example: A cloud service provider uses NIST IR (Incident Response) guidelines to coordinate with vendors during a ransomware attack. Case Study: SolarWinds Supply Chain Attack (2
Evolution and Adaptation in Modern Threat Landscapes
Cybersecurity principles have undergone a paradigm shift from static, rule-based defenses to dynamic, intelligence-driven frameworks as threat actors leverage advanced technologies like artificial intelligence (AI), machine learning (ML), and automation. The rise of AI-driven attacks—such as deepfake phishing, adversarial ML exploits, and autonomous malware—has necessitated a transition from reactive security measures to proactive, adaptive strategies. Similarly, ransomware-as-a-service (RaaS) models have democratized cybercrime, increasing both the frequency and sophistication of attacks. This evolution demands that core cybersecurity principles—traditionally rooted in perimeter defense and access control—now integrate behavioral analysis, deception tactics, and zero-trust architectures to mitigate evolving risks in hybrid and remote work environments.The adaptation of cybersecurity principles reflects broader shifts in threat intelligence, operational resilience, and regulatory expectations. While traditional models relied on static firewalls, antivirus signatures, and rigid authentication protocols, modern approaches emphasize context-aware security, continuous validation, and deception-based deterrence. Principles like least privilege and defense in depth have been reengineered to function effectively in decentralized, cloud-native, and remote-access scenarios, where the traditional network perimeter no longer exists.
AI-Driven Attacks and the Shift Toward Behavioral Analytics
AI and ML have become dual-edged swords in cybersecurity: while they empower defenders with predictive analytics and anomaly detection, they also enable attackers to automate and personalize attacks at scale. AI-driven threats exploit vulnerabilities in ML models through techniques such as:
Adversarial attacks: Manipulating input data to deceive ML classifiers (e.g., evading facial recognition in biometric authentication). Automated phishing: Generating hyper-realistic emails using generative AI (e.g., WormGPT, a tool marketed for creating convincing phishing campaigns). Deepfake impersonation: Voice or video cloning to bypass multi-factor authentication (MFA) or social engineering defenses. To counter these threats, behavioral analytics has emerged as a cornerstone of modern cybersecurity. Unlike signature-based detection, behavioral models analyze patterns of user activity, system interactions, and network traffic to identify deviations indicative of compromise. For example:
User and Entity Behavior Analytics (UEBA): Detects lateral movement by monitoring deviations from baseline behavior (e.g., an executive suddenly accessing unusual file types). AI-driven threat hunting: Uses unsupervised learning to uncover hidden attack chains in large datasets (e.g., Darktrace’s Antigena autonomously responding to zero-day exploits). Deception technology: Deploying honeypots and honeytokens to lure attackers into detectable traps, exposing their tactics (e.g., CrowdStrike’s Falcon Deception). Key Adaptation: Traditional antivirus relies on known malware signatures; behavioral analytics detects unknown threats by focusing on how systems are used, not just what is used.Ransomware-as-a-Service and the Rise of Automated Extortion
The Ransomware-as-a-Service (RaaS) model has transformed cybercrime into a subscription-based business, lowering the barrier for entry for non-technical actors. Key characteristics of RaaS include:
Affiliate networks: Cybercriminals rent malware kits (e.g., LockBit, Conti) with built-in customer support and revenue-sharing models. Double extortion: Attackers exfiltrate data before encryption, threatening to leak it if ransom demands are unmet (e.g., REvil’s attacks on Kaseya). Targeted supply-chain attacks: Compromising third-party vendors to infiltrate high-value organizations (e.g., SolarWinds breach leading to DarkSide ransomware deployments). Modern cybersecurity principles address RaaS through:
Immutable backups: Ensuring critical data cannot be altered or encrypted (e.g., AWS Backup with versioning and air-gapped storage). Endpoint detection and response (EDR): Real-time monitoring of suspicious processes (e.g., CrowdStrike Falcon blocking ransomware execution). Decoy systems: Deploying canary tokens or fake credentials to detect reconnaissance activities (e.g., CanaryTokens.org). Industry Impact: The 2023 Cost of a Data Breach Report (IBM) found that ransomware attacks increased average breach costs by $1.85 million, with 45% of organizations paying ransoms in 2022.Comparison of Traditional and Modern Cybersecurity Approaches
The following table contrasts legacy cybersecurity principles with their modern adaptations, highlighting the shift from static defenses to dynamic resilience:
Traditional Principle Modern Adaptation Key Enabling Technology Example Use Case Perimeter Security Zero Trust Architecture (ZTA) Identity-aware micro-segmentation Google BeyondCorp: No implicit trust; verify every request. Static Firewalls Software-Defined Perimeter (SDP) Dynamic access policies Cloudflare Access: Restricts IP-based access. Password Authentication Passwordless + Behavioral Biometrics FIDO2, adaptive MFA Microsoft Authenticator with risk-based challenges. Signature-Based Antivirus AI-Powered EDR/XDR Behavioral detection, ML anomaly scoring SentinelOne Singularity detects zero-day malware. Least Privilege (Static Roles) Just-In-Time (JIT) Access Privileged Access Management (PAM) CyberArk Vault grants temporary admin rights. Defense in Depth (Layered) Deception + Adaptive Defense Honeypots, automated threat simulation Illusive Networks deploys decoy environments. Critical Insight: Modern approaches prioritize context over static rules—e.g., granting access based on user behavior, device health, and risk score rather than IP or pre-configured roles.Adapting Least Privilege and Defense in Depth for Hybrid Work
The proliferation of remote work and cloud adoption has eroded the efficacy of traditional least privilege and defense in depth models, which assumed a centralized network perimeter. Adaptations include:#### Least Privilege in Decentralized Environments
Dynamic Role-Based Access Control (RBAC): Assigns permissions based on real-time context (e.g., Okta’s Adaptive MFA adjusts access based on location and device posture). Privileged Access Management (PAM): Limits admin rights to just-in-time (JIT) sessions (e.g., BeyondTrust Privilege Management). Attribute-Based Access Control (ABAC): Grants access based on attributes like job function, time of day, or data classification (e.g., Microsoft Azure ABAC policies). Real-World Example: SolarWinds breach (2020) exploited excessive privileges in the supply chain; modern PAM solutions would have restricted the attacker’s lateral movement.Defense in Depth for Hybrid Networks
Micro-Segmentation: Divides networks into isolated zones to contain breaches (e.g., VMware NSX). Zero Trust Network Access (ZTNA): Replaces VPNs with identity-centric access (e.g., Zscaler Private Access). Deception Grid: Deploys fake assets to detect reconnaissance (e.g., Attivo Networks honeypots). Continuous Compliance Monitoring: Ensures endpoints meet security baselines (e.g., Tanium for real-time patch validation). Hybrid Work Challenge: 74% of organizations report increased cloud-related risks due to remote access (Ponemon Institute, 2023); defense in depth now requires cloud-native segmentation and identity-first security.Timeline of Key Milestones in Cybersecurity Principle Development
The following timeline traces the evolution of cybersecurity principles, from perimeter-based defense to distributed, identity-centric security:
Year Milestone Principle Shift Impact 1980s Firewalls (Early Packet Filtering) Perimeter security First line of defense against external threats (e.g., Check Point Firewall-1). Practical Applications in Incident Response and Recovery
Cybersecurity principles serve as the foundational framework for structured incident response and recovery, ensuring that organizations can mitigate threats, minimize damage, and restore operations efficiently. These principles—such as least privilege, defense in depth, and zero trust—are not merely theoretical but are actively applied in real-world scenarios to contain breaches, eradicate threats, and recover systems while preserving forensic evidence. The effectiveness of incident response hinges on the systematic integration of these principles into procedural workflows, forensic analysis, and disaster recovery planning.The application of cybersecurity principles in incident response follows a phased approach: containment, eradication, and recovery. Each phase relies on predefined protocols that align with core principles to ensure accountability, traceability, and resilience. Forensic analysis further leverages these principles to reconstruct attack vectors, identify vulnerabilities, and implement corrective measures. Additionally, tabletop exercises and simulation drills incorporate these principles to test organizational preparedness against evolving threats, refining response strategies before actual incidents occur.
Procedural Steps for Applying Cybersecurity Principles in Incident Response
The incident response lifecycle is divided into structured phases where cybersecurity principles are embedded to guide actions. The containment phase prioritizes isolating affected systems to prevent lateral movement, adhering to the principle of segmentation and least privilege. The eradication phase focuses on removing malware, patching vulnerabilities, and restoring configurations, aligning with defense in depth and immutability principles. Finally, the recovery phase ensures systems are restored securely, with validation checks to confirm compliance with integrity and authenticity standards.The following steps outline the procedural integration of cybersecurity principles in each phase:
- Containment
- Implement network segmentation to isolate compromised segments, limiting attacker access to critical assets.
- Apply temporary access controls (e.g., disabling accounts, revoking permissions) based on the principle of least privilege.
- Deploy automated detection tools (e.g., SIEM, EDR) to enforce real-time containment aligned with defense in depth.
- Document all actions in an audit trail to ensure non-repudiation and compliance with regulatory requirements.
- Eradication
- Conduct a forensic analysis to identify root causes, leveraging hashing and digital signatures to verify malware authenticity.
- Patch vulnerabilities using secure baselines and immutable configurations, ensuring systems adhere to hardening principles.
- Reimage or restore systems from verified backups, prioritizing data integrity over speed to prevent reinfection.
- Update access policies and logging mechanisms to reflect lessons learned, reinforcing zero trust principles.
- Recovery
- Validate restored systems through penetration testing and vulnerability scans, ensuring compliance with security validation principles.
- Monitor for anomalous behavior post-recovery using behavioral analytics, aligning with continuous monitoring requirements.
- Communicate recovery status transparently to stakeholders, adhering to transparency and accountability principles.
- Conduct a post-incident review to refine response strategies, incorporating adaptive security principles for future threats.
Forensic Analysis Leveraging Cybersecurity Principles
Forensic analysis is critical for tracing attack origins, attributing responsibility, and restoring systems without compromising evidence integrity. Cybersecurity principles such as chain of custody, data preservation, and cryptographic verification underpin this process. Forensic investigators follow a structured methodology to ensure admissibility in legal proceedings while extracting actionable intelligence.Key steps in forensic analysis include:
Forensic tools such as FTK Imager, Autopsy, and Volatility automate parts of this process while ensuring compliance with digital forensics best practices. The use of blockchain-based evidence logging is emerging as a method to enhance tamper-proof documentation, further aligning with immutability principles.
- Evidence Collection
- Acquire forensic images of affected systems using write-blocking tools, preserving data integrity as per hash verification principles.
- Document timestamps and metadata to establish a chronological chain of events, ensuring non-repudiation.
- Isolate volatile memory (RAM) and log files to capture real-time attacker activity, adhering to transient data preservation principles.
- Attack Reconstruction
- Analyze network traffic logs and system artifacts to map the kill chain, applying defense in depth to identify all compromise points.
- Use behavioral forensics to detect living-off-the-land binaries (LOLBins) and fileless malware, aligning with anomaly detection principles.
- Cross-reference IOCs (Indicators of Compromise) with threat intelligence feeds to attribute attacks, leveraging threat intelligence integration principles.
- System Restoration
- Restore systems from air-gapped backups to prevent contamination, ensuring data authenticity through cryptographic checks.
- Apply forensic wiping techniques to sanitize compromised storage, adhering to secure deletion standards.
- Validate restoration using checksum comparisons and configuration baselines, confirming system integrity.
Best Practices for Disaster Recovery Planning Based on Cybersecurity Principles
Disaster recovery planning (DRP) must incorporate cybersecurity principles to ensure resilience against both cyber and physical threats. The following best practices are derived from core principles and real-world incident responses, such as the SolarWinds breach and Colonial Pipeline ransomware attack:
Principle-Based Disaster Recovery Best Practices:Organizations such as NIST and ISO/IEC 27031 provide frameworks for DRP, emphasizing risk-based prioritization and resource allocation aligned with cybersecurity principles. For example, the NIST SP 800-34 guide highlights the importance of pre-incident planning, detection, and post-incident analysis as critical components of a principle-driven DR strategy.
- Redundancy and Diversity
Deploy geographically distributed backups to mitigate single points of failure, adhering to the diversity of defense principle.- Immutable Backups
Store backups in write-once-read-many (WORM) storage to prevent tampering, ensuring data integrity and non-repudiation.- Automated Failover
Implement orchestrated failover mechanisms to restore services within defined recovery time objectives (RTOs), aligning with resilience principles.- Access Control for Recovery
Enforce role-based access control (RBAC) for DRP teams, limiting privileges to least privilege and separation of duties.- Regular Validation
Conduct quarterly DR drills to test recovery procedures, ensuring continuous improvement and adaptive security.- Incident-Specific Playbooks
Develop principle-driven playbooks for ransomware, DDoS, and insider threats, incorporating defense in depth and zero trust strategies.- Third-Party Vendor Resilience
Assess supply chain risks in DRP, ensuring vendors comply with security-by-design and transparency principles.
Cybersecurity Principles in Tabletop Exercises and Simulation Drills
Tabletop exercises (TTX) and simulation drills are proactive methods to test an organization’s ability to apply cybersecurity principles under simulated attack conditions. These exercises are designed to identify gaps, refine response strategies, and ensure alignment with regulatory requirements. The Homeland Security Exercise and Evaluation Program (HSEEP) and NIST’s Cybersecurity Framework (CSF) provide structured methodologies for conducting such dr
Visual and Descriptive Representations of Cybersecurity Principles
Cybersecurity principles serve as foundational guidelines for designing, implementing, and maintaining secure systems. Their effectiveness is significantly enhanced when visualized through structured representations—such as flowcharts, dashboards, threat modeling diagrams, and architectural schematics. These visual tools translate abstract concepts into actionable frameworks, facilitating decision-making during incidents, compliance audits, and system design phases. Below are descriptive breakdowns of how these principles are depicted in practical and analytical contexts.
Decision-Making Flowchart for Applying Cybersecurity Principles in a Breach Scenario
A decision-making flowchart for cybersecurity breach response integrates core principles—confidentiality, integrity, availability (CIA), least privilege, defense in depth, and incident response protocols—into a structured workflow. The flowchart begins with breach detection (e.g., anomaly alerts, SIEM triggers) and progresses through triage, containment, eradication, recovery, and post-incident review. Key decision nodes include:- Impact Assessment: Classifying the breach by severity (e.g., data exfiltration vs. system degradation) using DREAD (Damage, Reproducibility, Exploitability, Affected Users, Discoverability) metrics.
Principle Application Points: Confidentiality: Triggering data encryption (e.g., AES-256) for exposed assets and revoking compromised credentials. Integrity: Validating system logs via hash verification (SHA-256) to detect tampering. Availability: Isolating affected segments while maintaining critical services (e.g., failover to redundant servers). Escalation Paths: Directing responses based on regulatory obligations (e.g., GDPR’s 72-hour notification rule) or business continuity priorities. Documentation: Logging actions per audit trails for compliance (e.g., PCI DSS, NIST SP 800-61). The flowchart’s visual hierarchy uses color-coded paths (e.g., red for immediate containment, blue for forensic analysis) and conditional branches to reflect real-time adjustments, such as shifting from preventive controls (e.g., patching) to corrective controls (e.g., restoring from backups).
Cybersecurity Principle Dashboard: Key Visual Elements
A cybersecurity principle dashboard consolidates real-time data into a unified interface, prioritizing threat visibility, compliance adherence, and risk mitigation. Core visual components include:- Threat Intelligence Feeds:
Geospatial Heatmaps: Displaying attack vectors by origin (e.g., darknet chatter, Tor exit nodes) with risk scoring (e.g., MITRE ATT&CK tactics like Initial Access or Persistence). Timeline Visualizations: Chronological plots of incidents (e.g., phishing campaigns, ransomware outbreaks) with principle alignment (e.g., "Least Privilege Violation Detected" flags). Indicator of Compromise (IoC) Dashboards: Aggregating hashes, IP ranges, and domains from feeds like AlienVault OTX or FireEye Intelligence, categorized by STRIDE threats (e.g., Spoofing for credential stuffing). - Compliance Status Indicators:
Control Gap Analysis: Bar charts comparing implemented controls (e.g., NIST CSF Identify-Protect-Detect-Respond-Recover) against regulatory baselines (e.g., ISO 27001 Annex A). Automated Audit Trails: Checklists with real-time compliance markers (e.g., "Multi-Factor Authentication Enforced" for Authentication principle). Regulatory Deadlines: Countdown timers for mandatory disclosures (e.g., HIPAA’s 60-day breach reporting). - Risk Heatmaps:
Matrix Grids: Plotting asset criticality (y-axis) vs. vulnerability severity (x-axis) with color gradients (e.g., green for patched systems, red for unmitigated CVEs). Principle-Specific Alerts: Pop-ups for defense-in-depth violations (e.g., "No Web Application Firewall (WAF) for API endpoints"). The dashboard’s interactive filters allow drill-downs into principle-specific metrics, such as:
Encryption Coverage: Percentage of data encrypted at rest/transit (aligned with Confidentiality). Access Control Efficacy: Failed login attempts vs. successful authentications (aligned with Least Privilege). Redundancy Status: Uptime guarantees for critical systems (aligned with Availability). Depiction of Cybersecurity Principles in Threat Modeling Diagrams
Threat modeling frameworks like STRIDE and DREAD embed cybersecurity principles into attack surface analysis, translating abstract risks into mitigation strategies. Below are their visual and descriptive representations:- STRIDE Framework:
Spoofing: Depicted as an external actor (e.g., an attacker) impersonating a legitimate user (e.g., via session hijacking or phishing). Mitigation aligns with Authentication (e.g., biometric verification, certificate-based auth). Tampering: Illustrated as data corruption (e.g., SQL injection altering database records). Controls include Integrity checks (e.g., digital signatures, checksums). Repudiation: Shown as anonymous actions (e.g., a DDoS attacker denying involvement). Countermeasures involve Non-repudiation (e.g., audit logs, blockchain for transaction trails). Information Disclosure: Visualized as data leaks (e.g., exposed PII in logs). Principles applied: Confidentiality (e.g., field-level encryption, data masking). Denial of Service (DoS): Represented as resource exhaustion (e.g., CPU overload via flood attacks). Mitigations include Availability (e.g., rate limiting, load balancers). Elevation of Privilege: Depicted as unauthorized access escalation (e.g., exploiting a kernel vulnerability). Defenses align with Least Privilege (e.g., mandatory access control (MAC)). Diagram Structure:
Asset-Centric: Central node represents the system/component (e.g., a web application). Threat Arrows: Directed edges from external/internal actors to STRIDE threats, labeled with attack vectors (e.g., "Cross-Site Scripting (XSS)" for Tampering). Mitigation Annotations: Boxes adjacent to threats listing principle-based controls (e.g., "Use TLS 1.3 for Information Disclosure"). - DREAD Framework:
Risk Scoring Matrix: A table with axes for Damage Potential, Reproducibility, Exploitability, Affected Users, and Discoverability, each scored 1–10. Principle Integration: Damage: Linked to Confidentiality/Integrity (e.g., "Data breach impacts 10,000 records" → Encryption). Exploitability: Tied to Defense in Depth (e.g., "Multiple layers required to exploit" → Firewalls + IPS). Visual Weighting: Threats with high DREAD scores (e.g., >40) are bolded/red-highlighted, triggering immediate mitigation (e.g., patching a zero-day). Example Workflow:
1. Identify Threat: "Insider leaks customer data via misconfigured S3 bucket."
2. Map to STRIDE: Information Disclosure + Repudiation.
3. Apply DREAD: Score Damage as 9 (PII exposed), Discoverability as 3 (bucket publicly indexed).
4. Mitigate: Enforce Confidentiality (bucket encryption) and Non-repudiation (access logs + SIEM alerts).
Text-Based Illustration of a Secure System Architecture
A secure system architecture integrates cybersecurity principles into layered design, ensuring defense in depth and resilience. Below is a textual blueprint of a cloud-hosted e-commerce platform, labeling principle applications:┌───────────────────────────────────────────────────────┐
│ Client Layer │
│ ┌─────────────┐ ┌─────────────┐ ┌───────────┐ │
│ │Cybersecurity principles do far more than defend against cyber threats—they redefine how organizations perceive, implement, and sustain security in dynamic digital environments. From the structured application of confidentiality, integrity, and availability to the adaptive strategies required for hybrid workforces and AI-driven attacks, these principles provide a cohesive framework for risk mitigation and resilience. Their integration into compliance frameworks, incident response protocols, and architectural designs ensures that security is not an afterthought but a proactive, evolving discipline. As threats continue to evolve, the principles remain the cornerstone of a secure digital future, guiding both technical implementations and strategic decision-making to protect what matters most: data, systems, and trust.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.