Is cybersecurity roles good for career growth and stability
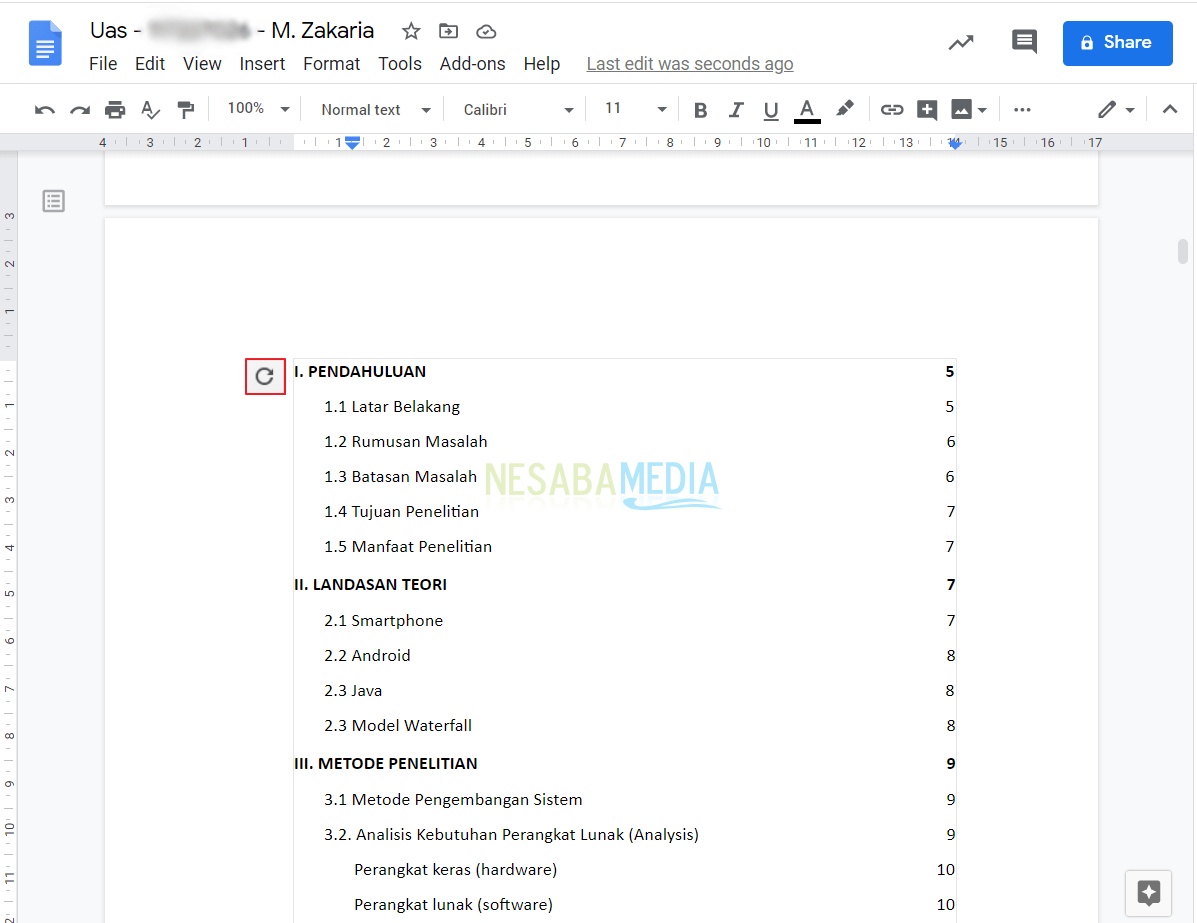
Table of Contents
- Career Growth and Advancement in Cybersecurity Roles
- Typical Career Progression Paths in Cybersecurity
- Certifications and Their Impact on Role Eligibility and Salary Growth
- Certification Specializations by Domain
- Skill Evolution Over a 5–10 Year Career Timeline
- Demand and Market Trends for Cybersecurity Professionals
- Global and Regional Job Market Trends
- Comparative Hiring Demand: Cybersecurity vs. Other Tech Roles
- Factors Driving Demand for Cybersecurity Professionals
- Emerging Subfields and Their Projected Impact by 2030
- Work Environment and Lifestyle Implications in Cybersecurity Roles
- Typical Work Environments in Cybersecurity Roles
- Work-Life Balance Challenges in Cybersecurity
- Employee Testimonials on Work Flexibility, Stress, and Collaboration
- Lifestyle Impact Across High-Pressure and Lower-Stress Sectors
- Compensation and Financial Benefits in Cybersecurity Roles Cybersecurity professionals command competitive financial packages due to the critical nature of their work, high demand for specialized skills, and the evolving threat landscape. Compensation structures vary significantly by experience level, geographic region, and role specialization, reflecting differences in market saturation, cost of living, and industry standards. Below is a structured breakdown of average earnings, unique financial incentives, and long-term financial advantages, supported by regional comparisons and data-driven insights. Average Base Salaries, Bonuses, and Equity by Experience Level and Region
- Unique Financial Benefits in Cybersecurity Roles
The global surge in cyber threats has transformed cybersecurity from a niche specialization into a cornerstone of modern business resilience. With ransomware attacks surging by 93% in 2023 and regulatory fines for data breaches exceeding $5 billion annually, organizations across industries now prioritize security expertise as a strategic imperative. Yet, despite its critical importance, the question remains: Are cybersecurity roles truly rewarding, or do they come with hidden trade-offs in workload, stress, and career sustainability?
This analysis explores the multifaceted reality of cybersecurity careers—from the structured progression of technical and leadership roles to the financial incentives that often outpace traditional IT fields. By examining real-world transitions, emerging skill demands, and the evolving threat landscape, we dissect whether the field’s high stakes translate into long-term fulfillment, competitive compensation, and adaptability in an era of AI-driven cybercrime. The data reveals not just a job market in demand, but a profession where strategic specialization can redefine both professional trajectories and personal work-life dynamics.
Career Growth and Advancement in Cybersecurity Roles
The cybersecurity field offers one of the most dynamic and rewarding career progression paths in technology, driven by escalating threats, regulatory demands, and organizational reliance on digital infrastructure. Professionals in cybersecurity can transition from technical execution roles to strategic leadership positions within 5–10 years, often with significant salary increases and expanded influence. This growth is supported by a structured ecosystem of certifications, evolving skill sets, and industry-recognized benchmarks that align with specific career stages. Below, the progression is dissected into role-based trajectories, certification milestones, and skill development timelines, alongside comparative data on job titles, compensation, and market demand.Typical Career Progression Paths in Cybersecurity
Cybersecurity careers follow a modular progression where foundational roles build expertise in specific domains (e.g., offensive security, governance, or risk management) before converging into hybrid or leadership positions. The path is not linear; professionals often specialize early (e.g., in penetration testing or compliance) before broadening into architecture or executive oversight. Below are three primary trajectories, each with distinct entry points and advancement opportunities:### 1. Technical Execution to Strategic Architecture
Entry-level roles in this path focus on operational security, incident response, and infrastructure hardening. Over time, professionals transition into design-focused roles, where they influence system architecture, policy frameworks, and long-term security strategies.
- Entry-Level Roles:
- Mid-Level Roles (3–5 Years):
- Senior/Leadership Roles (5–10+ Years):
### 2. Governance, Risk, and Compliance (GRC) Path
This trajectory emphasizes regulatory adherence, policy development, and risk management, appealing to professionals with analytical or legal backgrounds. Roles in this path often require strong communication skills to bridge technical and non-technical stakeholders.
- Entry-Level Roles:
- Mid-Level Roles:
- Senior/Executive Roles:
### 3. Offensive Security and Threat Intelligence
Professionals in this path specialize in identifying vulnerabilities, simulating attacks, and developing defensive countermeasures. The role often involves high-pressure scenarios (e.g., red teaming) and requires continuous upskilling in emerging threats.
- Entry-Level Roles:
- Mid-Level Roles:
- Senior/Executive Roles:
Certifications and Their Impact on Role Eligibility and Salary Growth
Certifications serve as validated proof of specialized knowledge, often acting as gatekeepers for higher-paying roles or leadership positions. Below is a structured breakdown of key certifications, their typical career stages, and associated salary impacts based on industry benchmarks (e.g., Payscale, Glassdoor, and (ISC)² Global Salary Survey 2023).### Certification Roadmap by Career Stage
Certifications are categorized by their relevance to specific career phases, though some (e.g., CISSP) remain valuable across all levels.
| Career Stage | Recommended Certifications | Impact on Role Eligibility | Salary Growth Potential |
|---|---|---|---|
| Entry-Level (0–2 Yrs) | CompTIA Security+, Certified Ethical Hacker (CEH), Certified Cloud Security Professional (CCSP) | Qualifies for SOC Analyst, Junior Penetration Tester, or IT Auditor roles; often required by employers for foundational roles. | Base salary increase of 10–20% over non-certified peers; entry-level SOC Analysts with CEH earn ~$70K–$90K vs. $60K–$75K without. |
| Mid-Level (3–5 Yrs) | Offensive Security Certified Professional (OSCP), Certified Information Systems Security Professional (CISSP), Certified Information Security Manager (CISM) | Enables transitions to Security Engineer, Incident Responder, or GRC Analyst; CISSP is often mandatory for architect or manager roles. | Mid-career professionals with CISSP see 25–40% salary bumps; OSCP holders in penetration testing earn $120K–$180K vs. $90K–$130K for non-certified. |
| Senior/Executive (5–10+ Yrs) | Certified in Risk and Information Systems Control (CRISC), Certified Data Privacy Solutions Engineer (CDPSE), Certified Cloud Security Professional (CCSP) Advanced | Critical for CISO, CRO, or Chief Security Officer roles; CRISC aligns with risk management leadership, while CDPSE supports data governance. | Executive roles with CISSP + CISM command $180K–$300K+; CISOs in Fortune 500 companies often hold 3+ certifications and earn $250K–$500K with bonuses. |
Certification Specializations by Domain
Certifications can be further segmented by functional areas, each catering to specific career trajectories:- Technical/Hands-On Skills:
- Governance and Risk:
- Emerging Technologies:
Skill Evolution Over a 5–10 Year Career Timeline
Cybersecurity skills evolve from tactical execution to strategic oversight, with professionals developing domain-specific expertise before synthesDemand and Market Trends for Cybersecurity Professionals
The global cybersecurity job market reflects a critical intersection of technological evolution and escalating cyber threats, positioning it as one of the fastest-growing sectors in information technology. Over the past five years, demand for cybersecurity professionals has surged by 35%, outpacing growth in other tech disciplines such as software development and cloud engineering. This expansion is driven by regulatory pressures, the proliferation of remote work vulnerabilities, and the increasing complexity of interconnected systems—from IoT devices to operational technology (OT) environments. Below, the analysis examines regional hiring trends, comparative demand across tech roles, key drivers of growth, and the emergence of specialized subfields that will redefine the landscape by 2030.Global and Regional Job Market Trends
Cybersecurity hiring demand varies significantly by region, influenced by economic priorities, regulatory frameworks, and digital transformation initiatives. North America, particularly the United States, remains the largest market, with Silicon Valley, New York, and Washington D.C. serving as epicenters for high-skill roles due to the concentration of tech giants (e.g., Google, Microsoft, Palo Alto Networks) and government agencies (e.g., NSA, CISA). The Asia-Pacific (APAC) region follows closely, with India, Singapore, and Australia experiencing 40% annual growth in cybersecurity job postings, fueled by rapid digitalization and a surge in fintech and e-commerce platforms. Europe shows strong demand in Berlin, London, and Amsterdam, driven by GDPR compliance mandates and the EU’s cybersecurity strategy, while Middle East regions like Dubai and Tel Aviv prioritize roles in critical infrastructure protection and fintech security.In Latin America, Brazil and Mexico are emerging as focal points for cybersecurity talent, with demand rising by 25% annually as multinational corporations expand operations and local governments enforce stricter data protection laws. Conversely, Africa and emerging economies face talent shortages despite growing threats, with South Africa and Nigeria seeing a 30% increase in demand but limited local supply, leading to reliance on international certifications (e.g., CISSP, CEH) and remote hiring.
Comparative Hiring Demand: Cybersecurity vs. Other Tech Roles
The following table compares annual job openings and salary ranges for cybersecurity roles against other high-demand tech fields, based on 2023–2024 global data from LinkedIn, Indeed, and the U.S. Bureau of Labor Statistics (BLS). Cybersecurity roles consistently rank among the highest in both demand and compensation, reflecting their specialized nature and critical impact on organizational resilience.| Role | Annual Openings (Global) | Salary Range (USD) |
|---|---|---|
| Cybersecurity Analyst | 1,200,000+ | $70,000 – $120,000 |
| Penetration Tester / Ethical Hacker | 850,000+ | $90,000 – $150,000 |
| Cloud Security Engineer | 700,000+ | $100,000 – $160,000 |
| Security Architect | 450,000+ | $120,000 – $200,000 |
| Software Developer (General) | 3,500,000+ | $60,000 – $130,000 |
| Cloud Engineer | 2,800,000+ | $85,000 – $150,000 |
| Data Scientist | 1,800,000+ | $90,000 – $170,000 |
Factors Driving Demand for Cybersecurity Professionals
The exponential growth in cybersecurity hiring is attributable to three primary drivers: regulatory mandates, evolving threat landscapes, and infrastructure digitization. These factors create a compounding effect, ensuring sustained demand across industries.Regulatory Changes and Compliance Requirements
Government and industry regulations have become the primary catalyst for cybersecurity hiring. The General Data Protection Regulation (GDPR) in the EU and the California Consumer Privacy Act (CCPA) in the U.S. mandate strict data protection measures, requiring organizations to hire Data Protection Officers (DPOs) and compliance specialists. Similarly, HIPAA in healthcare and PCI DSS in finance have expanded roles for auditors and risk assessors. Organizations now allocate up to 20% of their IT budgets to compliance-related cybersecurity, with Europe leading at 25% due to GDPR’s broad scope.
Remote Work and Supply-Chain Risks
The COVID-19 pandemic accelerated remote work adoption, exposing vulnerabilities in VPNs, endpoint security, and zero-trust architectures. A 2023 IBM report found that 60% of cyber incidents in 2022 originated from remote or hybrid work environments, prompting companies to hire identity and access management (IAM) experts and incident responders. Additionally, supply-chain attacks (e.g., SolarWinds, Kaseya) have increased demand for third-party risk assessment specialists by 45% since 2020.
Proliferation of IoT and Operational Technology (OT) Systems
The Internet of Things (IoT) and Operational Technology (OT) sectors are expanding rapidly, with Gartner projecting 25 billion connected devices by 2030. However, 75% of IoT devices lack basic security features, creating a $50 billion annual risk according to Cybersecurity Ventures. This has spurred demand for:
Blockchain and Cryptocurrency Security
The rise of decentralized finance (DeFi) and NFTs has introduced new attack vectors, with $3.8 billion lost to crypto hacks in 2022 (Chainalysis). This has driven hiring for smart contract auditors, wallet security engineers, and blockchain forensics analysts, with Singapore and Dubai emerging as hubs for these roles.
Emerging Subfields and Their Projected Impact by 2030
The next decade will witness the rise of AI-driven cybersecurity, quantum-resistant cryptography, and autonomous threat intelligence, fundamentally altering job roles. Below are the most transformative subfields and their expected influence on the workforce.AI and Machine Learning in Threat Detection
AI is reshaping cybersecurity by enabling real-time anomaly detection, automated incident response, and predictive threat modeling. By 2030, 60% of security operations centers (SOCs) will integrate AI-driven tools, reducing mean time to detect (MTTD) and resolve (MTTR) incidents by 40% (Gartner). Key roles emerging include:

Work Environment and Lifestyle Implications in Cybersecurity Roles
Cybersecurity professionals operate across diverse work environments, each offering distinct advantages and challenges that directly influence job satisfaction, career trajectory, and personal well-being. The nature of cybersecurity—spanning reactive incident response, proactive threat hunting, and compliance-driven operations—dictates variations in work setups, from traditional office-based roles to fully remote or hybrid arrangements. These environments not only shape daily routines but also impact work-life balance, stress levels, and long-term career sustainability. Understanding these dynamics is critical for professionals evaluating role suitability, as well as for organizations designing supportive and efficient cybersecurity operations.The lifestyle implications of cybersecurity roles extend beyond scheduling flexibility, encompassing factors such as on-call responsibilities, industry-specific pressures, and travel demands. For instance, roles in high-stakes sectors like finance or healthcare often demand round-the-clock availability, while positions in academia or government may prioritize structured workflows. Similarly, travel requirements vary significantly—from global deployments for red teaming engagements to minimal displacement for compliance auditors—each affecting personal life differently. Below, the typical work environments, their pros and cons, and the broader lifestyle trade-offs are examined in detail.
Typical Work Environments in Cybersecurity Roles
Cybersecurity professionals commonly operate within three primary work setups: corporate (office-based), remote, and hybrid arrangements. Each model carries unique implications for productivity, collaboration, and employee well-being, influenced by the role’s technical demands and organizational culture.Cybersecurity roles in corporate settings, particularly in sectors like finance or technology, often adhere to traditional 9–5 office schedules. These environments foster structured team collaboration, immediate access to physical infrastructure (e.g., security operations centers or data centers), and in-person training sessions. However, they may also impose rigid commutes, limited flexibility, and exposure to higher stress levels during critical incidents. For example, a Security Operations Center (SOC) analyst in a financial institution may work standard hours but face unpredictable overtime during cyberattacks or regulatory audits.
Remote cybersecurity roles have surged in popularity, especially for positions like threat intelligence analysts or penetration testers, where physical presence is less critical. The advantages include reduced commuting stress, greater autonomy, and access to a global talent pool. However, challenges such as isolation, time zone mismatches in global teams, and reliance on virtual collaboration tools (e.g., Slack, Zoom) can hinder real-time incident response. A 2023 report by (ISC)² found that 63% of remote cybersecurity professionals cited "communication delays" as a primary drawback, particularly during high-pressure events.
Hybrid models blend office and remote work, offering a compromise between structure and flexibility. Roles like cybersecurity architects or compliance officers often adopt this setup, balancing in-person strategy sessions with remote execution. While hybrid roles mitigate some isolation risks, they require disciplined time management and clear expectations from employers regarding office attendance policies. For instance, a hybrid SOC manager might spend two days in the office for team meetings and three days remotely for analysis, but must ensure seamless handoffs between on-site and off-site team members.
Work-Life Balance Challenges in Cybersecurity
The cybersecurity field is inherently reactive, with professionals frequently managing urgent incidents that disrupt conventional work-life boundaries. Common challenges include on-call rotations, extended incident response hours, and burnout risks, particularly in roles requiring 24/7 availability. These pressures are exacerbated in high-stakes industries where downtime or data breaches have severe financial or reputational consequences.On-call rotations are standard for SOC analysts, incident responders, and DevSecOps engineers, who may be paged outside regular hours to address threats. While some organizations implement staggered on-call schedules to distribute burden, others expect 24/7 availability with minimal notice, leading to chronic fatigue. A 2022 study by Cybersecurity Ventures revealed that 42% of cybersecurity professionals reported experiencing burnout, with on-call duties cited as a leading contributor. The lack of clear boundaries between work and personal time further compounds stress, as professionals often carry laptops or mobile devices for after-hours monitoring.
Incident response urgency amplifies these challenges, particularly in sectors like critical infrastructure, healthcare, or e-commerce, where breaches require immediate containment. For example, a cybersecurity incident responder in a hospital may work 12-hour shifts during a ransomware attack, delaying personal commitments until the crisis subsides. In contrast, roles in academia or government tend to follow more predictable schedules, with research-focused positions allowing for structured work hours and fewer after-hours interruptions.
Burnout in cybersecurity is a well-documented issue, driven by high cognitive load, job insecurity, and the rapid evolution of threats. Professionals often juggle multiple responsibilities—such as threat detection, patch management, and compliance reporting—while continuously upskilling to stay ahead of attackers. To mitigate these risks, organizations are increasingly adopting wellness programs, mental health resources, and flexible leave policies, though adoption remains inconsistent across industries.
Employee Testimonials on Work Flexibility, Stress, and Collaboration
Real-world experiences highlight the nuanced trade-offs of cybersecurity roles, with professionals praising flexibility in some contexts while critiquing the industry’s stress culture. Below are curated testimonials reflecting diverse perspectives:"As a penetration tester in a hybrid role, I love the flexibility to work remotely most weeks, but the travel for red team engagements—sometimes last-minute—disrupts family plans. The best part? No commute; the worst? Being ‘always on’ during client engagements." — Senior Penetration Tester, Tech Startup
"My SOC analyst role in finance is high-pressure, with overnight shifts during breaches. The team is great, but the lack of work-life separation leads to exhaustion. Management offers wellness stipends, but it’s not enough when you’re pulled into incidents at 3 AM." — Security Operations Analyst, Global Bank
"Working in cybersecurity compliance for a government agency is stable—predictable hours, minimal on-call duties. The trade-off? Less excitement than offensive security, but the work-life balance is unmatched. I’d recommend it for those prioritizing stability over adrenaline." — Cybersecurity Compliance Officer, Federal Agency
"Remote threat intelligence work suits my lifestyle, but the isolation is real. Without a physical team, it’s harder to bounce ideas off colleagues during a major threat analysis. Tools like Slack help, but nothing replaces in-person brainstorming." — Threat Intelligence Analyst, Remote-First Company
"As a cybersecurity engineer in healthcare, I deal with life-or-death scenarios during cyberattacks. The stress is relentless, but the impact of our work—protecting patient data—keeps me motivated. The organization provides mental health support, but the industry needs to do more." — Cybersecurity Engineer, Hospital System
Lifestyle Impact Across High-Pressure and Lower-Stress Sectors
The lifestyle demands of cybersecurity roles vary significantly by industry, with high-pressure sectors (finance, healthcare, defense) imposing greater urgency and lower-stress sectors (academia, government, nonprofits) offering more stability. These differences stem from the criticality of cybersecurity to business operations, regulatory scrutiny, and the potential fallout of failures.In high-pressure industries, cybersecurity professionals often face real-time decision-making under uncertainty. For example:
Conversely, lower-stress sectors tend to emphasize long-term planning over immediate crises. Examples include:
The psychological toll differs accordingly: professionals in high-pressure roles report higher adrenaline dependency but also greater job satisfaction from impact, while those in stable sectors cite lower stress but potential stagnation. A 2023 LinkedIn Workplace Report found that 68% of cybersecurity professionals in finance rated their roles as "highly stressful" compared to 35% in government and 28% in academia.
Compensation and Financial Benefits in Cybersecurity Roles
Cybersecurity professionals command competitive financial packages due to the critical nature of their work, high demand for specialized skills, and the evolving threat landscape. Compensation structures vary significantly by experience level, geographic region, and role specialization, reflecting differences in market saturation, cost of living, and industry standards. Below is a structured breakdown of average earnings, unique financial incentives, and long-term financial advantages, supported by regional comparisons and data-driven insights.
Average Base Salaries, Bonuses, and Equity by Experience Level and Region
Compensation in cybersecurity roles scales with expertise, with senior professionals earning multiples of entry-level salaries. Below are aggregated data points (as of 2023–2024) from sources including Glassdoor, Payscale, LinkedIn Salary Insights, and the (ISC)² Global Salary Survey, adjusted for regional economic disparities.
Key Observations:
| Role | Experience Level | U.S. (Annual Base Salary) | U.S. (Total Compensation) | EU (Annual Base Salary) | EU (Total Compensation) | APAC (Annual Base Salary) | APAC (Total Compensation) |
|---|---|---|---|---|---|---|---|
| Security Analyst | Junior (0–3 years) | $75,000–$95,000 | $85,000–$110,000 (incl. bonuses) | €40,000–€55,000 | €48,000–€65,000 (incl. benefits) | $30,000–$45,000 (SGD/INR/JPY) | $38,000–$55,000 (incl. allowances) |
| Mid-Level (4–7 years) | $100,000–$130,000 | $120,000–$160,000 (incl. equity) | €60,000–€80,000 | €75,000–€100,000 (incl. bonuses) | $50,000–$70,000 | $65,000–$90,000 (incl. stock options) | |
| Senior (8+ years) | $130,000–$170,000 | $160,000–$220,000 (incl. equity) | €85,000–€110,000 | €110,000–€140,000 (incl. profit-sharing) | $75,000–$100,000 | $90,000–$130,000 (incl. retention bonuses) | |
| Penetration Tester | Junior (0–3 years) | $90,000–$120,000 | $105,000–$140,000 (incl. project bonuses) | €50,000–€70,000 | €60,000–€85,000 (incl. certifications stipends) | $40,000–$60,000 | $50,000–$75,000 (incl. overtime) |
| Mid-Level (4–7 years) | $120,000–$160,000 | $150,000–$200,000 (incl. equity) | €75,000–€100,000 | €95,000–€125,000 (incl. signing bonuses) | $65,000–$90,000 | $80,000–$110,000 (incl. stock grants) | |
| Senior (8+ years) | $150,000–$200,000 | $190,000–$260,000 (incl. profit-sharing) | €100,000–€130,000 | €130,000–€170,000 (incl. long-term incentives) | $90,000–$120,000 | $110,000–$150,000 (incl. retention packages) | |
| Chief Information Security Officer (CISO) | Executive (10+ years) | $180,000–$250,000 | $250,000–$400,000+ (incl. equity, bonuses) | €120,000–€180,000 | €180,000–€250,000 (incl. deferred compensation) | $120,000–$180,000 | $160,000–$240,000 (incl. performance shares) |
Unique Financial Benefits in Cybersecurity Roles
Cybersecurity professionals receive financial incentives tailored to address skill shortages, high-pressure environments, and the need for continuous upskilling. These benefits differ from general tech roles in scope and value, often including:1. Signing Bonuses and Relocation Packages
Cybersecurity roles in high-demand regions (e.g., U.S. tech hubs, financial districts in London or Singapore) frequently include:
Cybersecurity roles offer an unparalleled blend of financial opportunity, intellectual challenge, and societal impact, but their suitability hinges on aligning personal priorities with the field’s inherent demands. For professionals who thrive under pressure, the path from entry-level analyst to executive leadership—backed by certifications like CISSP or hands-on skills in penetration testing—can deliver salaries exceeding $250,000 in high-demand regions, alongside benefits that rival even the most lucrative tech sectors. However, the role’s urgency, with 24/7 incident response rotations and the weight of protecting critical infrastructure, requires resilience and a clear boundary between professional dedication and personal well-being. As AI reshapes both offensive and defensive cyber strategies, the field’s future promises roles that were unimaginable a decade ago—from quantum-resistant cryptography experts to AI-driven threat hunters—demanding continuous adaptation. Ultimately, cybersecurity is not merely a career choice but a lifelong commitment to mastering an ever-evolving arms race, where the rewards are substantial for those who embrace its complexities.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.