Find Cybersecurity What Is It Core Principles Explained

Published

find cybersecurity what is it
Table of Contents

Cybersecurity stands as the critical safeguard of the digital era, shielding systems, data, and infrastructure from evolving threats that exploit vulnerabilities in technology and human behavior. As cyberattacks grow in frequency and sophistication—from ransomware targeting hospitals to state-sponsored espionage campaigns—understanding its foundational principles becomes essential for individuals, businesses, and governments alike. This exploration dissects cybersecurity’s core pillars, examines the technologies and frameworks that underpin modern defenses, and highlights best practices to mitigate risks across diverse sectors. By addressing both technical implementations and strategic policies, the discussion equips stakeholders with actionable insights to navigate an increasingly interconnected and perilous digital landscape.

The discipline extends beyond reactive measures, emphasizing proactive strategies such as zero-trust architectures, encryption protocols, and compliance frameworks like GDPR and NIST guidelines. Real-world case studies, from the Equifax breach to AI-driven cyber threats, illustrate the tangible consequences of oversight while underscoring the adaptability required to counter emerging risks. Whether assessing industry-specific vulnerabilities in healthcare or finance or evaluating the role of emerging technologies like quantum computing, this analysis provides a structured roadmap for fortifying digital resilience in an era where cyber threats are not merely technical challenges but existential concerns for global stability.

find cybersecurity what is it

Core Definition and Scope of Cybersecurity

Cybersecurity represents the collective practices, technologies, and processes designed to safeguard digital systems, networks, and data from unauthorized access, cyberattacks, or disruption. Its primary objective is to ensure the resilience of infrastructure against evolving digital threats while maintaining trust in digital interactions. The scope extends beyond mere technical defenses, encompassing policies, user education, and risk management to create a holistic security framework.

Cybersecurity operates at multiple layers—physical, technical, and administrative—to mitigate risks arising from malicious actors, human error, or system vulnerabilities. For instance, a healthcare provider must protect patient records from breaches, while a financial institution must secure transactions against fraud. The field evolves rapidly in response to new threats, such as AI-driven attacks or supply chain vulnerabilities, underscoring its dynamic and critical role in modern society.

Three Key Pillars of Cybersecurity

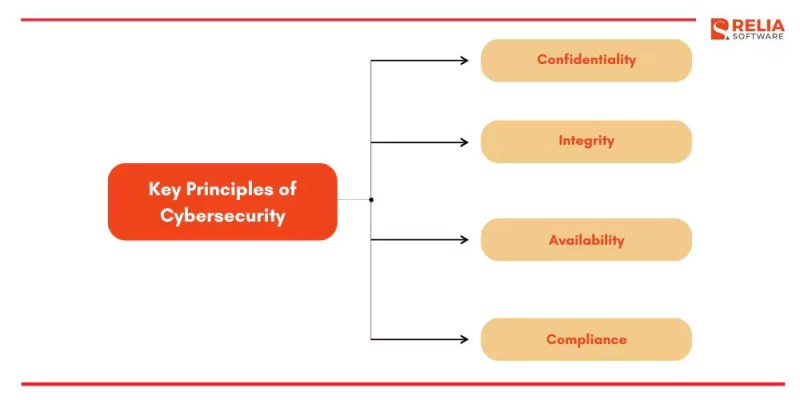
Cybersecurity is built on three foundational principles that align with the CIA Triad: Confidentiality, Integrity, and Availability. Each pillar addresses distinct aspects of data protection, ensuring systems remain secure and functional.
Confidentiality ensures that sensitive information is accessible only to authorized users.
Integrity guarantees that data remains accurate, unaltered, and trustworthy.
Availability ensures systems and data are accessible to legitimate users when needed.
A structured breakdown of these pillars, along with real-world examples, illustrates their practical application:

- Confidentiality: Protects data from unauthorized disclosure. Example: Encryption (e.g., TLS for secure web browsing) prevents third parties from reading transmitted data, such as credit card details during online transactions.

  • Integrity: Ensures data is not tampered with or altered. Example: Hash functions (e.g., SHA-256) detect changes in files, such as software updates or financial transactions, verifying their authenticity.
  • Availability: Maintains uninterrupted access to systems and data. Example: Redundant servers in cloud infrastructure (e.g., AWS multi-AZ deployments) prevent downtime during distributed denial-of-service (DDoS) attacks.
  • Comparison of Traditional Security and Cybersecurity Measures

    While traditional security focuses on physical protection, cybersecurity addresses digital vulnerabilities. Below is a comparative table highlighting key differences:
    Aspect Traditional Security Cybersecurity
    Primary Threat Physical intrusion (e.g., burglary, theft) Digital attacks (e.g., hacking, malware)
    Key Measures
    • Locks and alarms
    • Guards and surveillance cameras
    • Access control (keycards, biometrics)
    • Firewalls and intrusion detection systems (IDS)
    • Encryption (e.g., AES-256 for data at rest)
    • Multi-factor authentication (MFA)
    Response Time Immediate physical intervention (e.g., calling security) Real-time monitoring and automated responses (e.g., SIEM tools)
    Scalability Limited to physical premises Global reach (e.g., cloud-based security for remote teams)
    Example Scenario A bank vault protected by armed guards and biometric scanners. A corporate network secured with endpoint detection (EDR) and zero-trust architecture.
    The table demonstrates that while traditional security relies on tangible barriers, cybersecurity employs layered digital defenses to counteract sophisticated cyber threats.

    Cyber Threat Landscape

    The cyber threat landscape encompasses a diverse array of malicious activities targeting digital assets. Below are categorized threats, defined concisely with illustrative examples:

    - Malware: Malicious software designed to infiltrate or damage systems.

  • Examples: Ransomware (e.g., WannaCry encrypting hospital files), Trojan horses (e.g., Emotet stealing credentials), Spyware (e.g., FinFisher monitoring user activity).
  • Phishing: Deceptive attempts to trick individuals into revealing sensitive information.
  • Examples: Spear phishing (targeted emails impersonating executives), Smishing (SMS-based scams like fake banking alerts), Vishing (voice calls mimicking IT support).
  • Ransomware: A type of malware that encrypts data and demands payment for decryption.
  • Real-world impact: The Colonial Pipeline attack (2021) disrupted U.S. fuel supplies, costing $4.4 million in ransom.
  • Insider Threats: Risks posed by employees, contractors, or partners with legitimate access.
  • Examples: Malicious insiders (e.g., Edward Snowden leaking classified NSA documents), Negligent insiders (e.g., accidental data leaks via unsecured USB drives).
  • Advanced Persistent Threats (APTs): Long-term, targeted cyberattacks by state-sponsored actors.
  • Example: Stuxnet (2010), a worm sabotaging Iran’s nuclear centrifuges by exploiting industrial control systems.
  • Zero-Day Exploits: Attacks leveraging unknown vulnerabilities before vendors release patches.
  • Example: EternalBlue (exploited in WannaCry) targeted unpatched Windows systems.
  • Understanding these threats is critical for implementing proactive defenses, such as patch management, employee training, and threat intelligence sharing.

    Sector-Specific Applications of Cybersecurity

    Cybersecurity risks and protective measures vary significantly across industries due to differing regulatory requirements and asset sensitivities. Below are sector-specific examples:

    - Healthcare:

  • Risks:
    • Patient data breaches (e.g., HIPAA violations exposing medical records).
    • Ransomware targeting hospital IT systems (e.g., 2020 Ryuk attack on Universal Health Services).
    • IoT vulnerabilities in medical devices (e.g., unsecured insulin pumps).
  • Protections:
    • Role-based access control (RBAC) for EHR systems.
    • End-to-end encryption for patient communications.
    • Regular audits compliant with HIPAA and GDPR.
  • Finance:
  • Risks:
    • Payment card fraud (e.g., EMV chip skimming in ATMs).
    • Business email compromise (BEC) scams (e.g., $2.3 billion lost globally in 2022).
    • Supply chain attacks on fintech partners (e.g., SolarWinds breach affecting banks).
  • Protections:
    • Tokenization for credit card transactions.
    • Behavioral analytics to detect fraudulent transactions.
    • ISO 27001 certification for risk management frameworks.
  • Government:
  • Risks:
    • State-sponsored cyber espionage (e.g., 2015 Office of Personnel Management breach).
    • Critical infrastructure attacks (e.g., 2021 cyberattack on U.S. water treatment plants).
    • Data leaks from public sector databases (e.g., UK NHS ransomware attacks).
  • Protections:
    • Federal Information Security Modernization Act (FISMA) compliance.
    • Air-gapped systems for classified networks.
    • Cybersecurity Information Sharing Act (CISA) for threat intelligence.
    Each sector’s cybersecurity strategy must align with its unique operational and regulatory demands to mitigate tailored threats effectively.

    find cybersecurity what is it - Ilustrasi 2

    Key Components and Technologies in Cybersecurity

    Cybersecurity relies on a structured framework of technical layers and tools designed to protect systems, networks, and data from evolving threats. These components operate in tandem to mitigate vulnerabilities, detect anomalies, and enforce access controls. Below, the foundational technical layers—network security, endpoint security, application security, and data security—are examined alongside their roles in a defense-in-depth strategy. Additionally, implementation procedures for core technologies (firewalls, antivirus, IDS, VPNs) are outlined, followed by a comparative analysis of encryption methods and the principles of zero-trust architecture.

    Technical Layers of Cybersecurity

    Cybersecurity is organized into four interdependent layers, each addressing distinct attack surfaces and risk vectors. The network security layer safeguards data transmission across wired and wireless networks, while endpoint security focuses on devices like desktops, laptops, and mobile endpoints. Application security ensures software integrity and resilience against exploits, and data security protects stored or in-transit information through encryption and access controls. These layers collectively form a defense-in-depth model, where failure in one component triggers compensating controls in others.

    Network Security
    Network security employs technologies to monitor, filter, and secure traffic between devices. Key measures include:

  • Firewalls: Stateful packet inspection (SPI) and next-generation firewalls (NGFW) enforce access rules based on IP addresses, ports, and application protocols.
  • VPNs: Encapsulate and encrypt traffic using protocols like IPsec or OpenVPN, ensuring confidentiality over untrusted networks.
  • Network Segmentation: Isolates critical assets (e.g., servers, IoT devices) to limit lateral movement by attackers.
  • Intrusion Prevention Systems (IPS): Actively blocks malicious traffic by analyzing patterns against threat signatures or behavioral anomalies.
  • Endpoint Security
    Endpoints are primary targets for malware and unauthorized access. Protections include:

  • Antivirus/Antimalware: Scans files and processes for known threats (e.g., ransomware, trojans) using signature-based or heuristic detection.
  • Endpoint Detection and Response (EDR): Provides real-time monitoring, forensic analysis, and automated response to advanced threats.
  • Device Hardening: Configures systems to minimize attack surfaces (e.g., disabling unnecessary services, enforcing least-privilege access).
  • Mobile Device Management (MDM): Enforces security policies on BYOD (Bring Your Own Device) environments, including encryption and remote wipe capabilities.
  • Application Security
    Applications often contain vulnerabilities exploited via injection attacks, misconfigurations, or API abuses. Mitigations include:

  • Static/Dynamic Application Security Testing (SAST/DAST): Identifies flaws in code (e.g., SQL injection, cross-site scripting) during development or runtime.
  • Runtime Application Self-Protection (RASP): Integrates with applications to detect and block exploits in real time.
  • Secure Coding Practices: Adheres to frameworks like OWASP Top 10 to prevent common vulnerabilities (e.g., insecure dependencies, broken authentication).
  • Web Application Firewalls (WAF): Filters HTTP/HTTPS traffic to block attacks targeting web apps (e.g., DDoS, CSRF).
  • Data Security
    Data security ensures confidentiality, integrity, and availability (CIA triad) through:

  • Encryption: Transforms data into unreadable formats (e.g., AES for symmetric, RSA for asymmetric encryption).
  • Data Loss Prevention (DLP): Monitors and prevents unauthorized data exfiltration (e.g., emailing sensitive files).
  • Access Controls: Implements role-based access (RBAC) or attribute-based access control (ABAC) to restrict data exposure.
  • Backup and Recovery: Maintains redundant copies of data to recover from ransomware or hardware failures.
  • Implementation Procedure for Basic Cybersecurity Technologies

    Deploying foundational cybersecurity tools requires systematic planning to ensure effectiveness without disrupting operations. Below is a step-by-step procedure for four critical technologies:

    Firewalls
    1. Assess Network Topology: Map all devices, subnets, and traffic flows to define firewall placement (e.g., perimeter, internal segments).
    2. Define Security Policies: Create rules based on:

  • Default Deny: Block all traffic unless explicitly allowed.
  • Least Privilege: Restrict access to only necessary ports/protocols (e.g., allow HTTP/HTTPS to web servers, RDP to admin workstations).
  • Stateful Inspection: Track connection states to prevent spoofed packets.
  • 3. Deploy and Test: Install the firewall (hardware/software) and validate rules using:
  • Penetration Testing: Simulate attacks to identify misconfigurations.
  • Log Analysis: Verify rule effectiveness by monitoring blocked traffic.
  • 4. Maintain and Update: Regularly review logs, update rules for new threats, and patch firmware.

    Antivirus Software
    1. Select an Agent: Choose between signature-based (e.g., McAfee) or behavior-based (e.g., CrowdStrike) solutions based on threat landscape.
    2. Deploy Agents: Install on all endpoints, ensuring compatibility with OS and applications.
    3. Configure Scans:

  • Schedule regular scans (e.g., daily for critical systems, weekly for others).
  • Enable real-time protection for file downloads/execution.
  • 4. Update Definitions: Automate signature/engine updates to counter zero-day threats.
    5. Monitor and Respond: Set up alerts for detected malware and quarantine suspicious files for analysis.

    Intrusion Detection Systems (IDS)
    1. Choose Deployment Mode:

  • Network-Based IDS (NIDS): Monitors traffic at chokepoints (e.g., Snort, Suricata).
  • Host-Based IDS (HIDS): Analyzes system logs and processes (e.g., OSSEC, AIDE).
  • 2. Define Detection Rules: Use preconfigured rulesets (e.g., Emerging Threats for Snort) or customize for organization-specific threats.
    3. Integrate with SIEM: Forward alerts to a Security Information and Event Management (SIEM) system for correlation and incident response.
    4. Tune for False Positives: Adjust sensitivity to reduce benign traffic misclassification.
    5. Validate with Simulated Attacks: Test IDS effectiveness using tools like Metasploit or custom payloads.

    Virtual Private Networks (VPNs)
    1. Select VPN Protocol:

  • IPsec: Suitable for site-to-site connections (e.g., branch offices).
  • OpenVPN/WireGuard: Preferred for remote access due to flexibility and performance.
  • SSL/TLS (e.g., AnyConnect): Ideal for web-based access with built-in encryption.
  • 2. Configure Server and Client:
  • Server Setup: Install VPN software, generate certificates (for TLS/IPsec), and configure routing tables.
  • Client Configuration: Distribute credentials (e.g., PSK for IPsec, certificates for TLS) securely.
  • 3. Enforce Policies:
  • Split Tunneling: Route only necessary traffic through the VPN to improve performance.
  • Multi-Factor Authentication (MFA): Require MFA for remote access to mitigate credential theft.
  • 4. Monitor Usage: Track connection logs for anomalies (e.g., unusual geolocations, repeated failures).

    Essential Cybersecurity Tools and Their Functions

    Cybersecurity tools automate threat detection, vulnerability assessment, and incident response. Below is a table of 10 critical tools categorized by function, along with examples and use cases:
    Tool Category Primary Function Example Tools Use Case
    Network Analysis Packet capture, protocol analysis, and traffic monitoring. Wireshark, TShark, NetworkMiner Investigating intrusions, debugging network issues, or analyzing malware C2 (command-and-control) traffic.
    Vulnerability Scanning Identifies security flaws in systems, networks, or applications. Nessus, OpenVAS, Qualys Compliance audits (e.g., PCI DSS), pre-deployment security assessments, or patch management prioritization.
    Web Application Testing Detects vulnerabilities in web apps (e.g., OWASP Top 10). Burp Suite, OWASP ZAP,

    Cybersecurity Best Practices for Individuals and Organizations

    Cybersecurity threats evolve in sophistication and frequency, necessitating proactive measures from both individuals and organizations to mitigate risks. While technical defenses form the backbone of cybersecurity, human behavior and structured frameworks play equally critical roles in preventing breaches. This section outlines actionable strategies for personal cybersecurity, organizational frameworks like the NIST Cybersecurity Framework, and comparative policies for businesses of varying scales. Additionally, it explores the principle of least privilege (PoLP) and examines real-world case studies to derive actionable lessons for resilience.

    Actionable Checklist for Individuals to Enhance Personal Cybersecurity

    Individuals remain the primary targets for cybercriminals due to vulnerabilities in human behavior and weak authentication practices. Implementing a layered defense strategy significantly reduces exposure to threats such as identity theft, malware, and financial fraud. Below is a structured checklist of best practices, categorized by priority and ease of implementation.
    • Password Hygiene
      • Use passphrases (e.g., "BlueSky$2024!") instead of short passwords, combining uppercase, lowercase, numbers, and symbols.
      • Enable password managers (e.g., Bitwarden, 1Password) to generate, store, and auto-fill unique credentials for each account.
      • Conduct regular audits (quarterly) to identify and update weak or reused passwords using tools like Have I Been Pwned.
      • Avoid storing passwords in plaintext files or browser autofill (unless encrypted by the manager).
    • Multi-Factor Authentication (MFA)
      • Enable MFA for all accounts supporting it, prioritizing email, banking, social media, and cloud services (Google, Microsoft, Apple).
      • Use authenticator apps (e.g., Google Authenticator, Authy) over SMS-based MFA, as SMS is vulnerable to SIM swapping.
      • For high-risk accounts, implement hardware tokens (e.g., YubiKey) or biometric verification (fingerprint/face ID).
      • Disable MFA backup codes after secure storage (e.g., encrypted password manager) to prevent unauthorized access if lost.
    • Phishing and Social Engineering Recognition
      • Verify sender email addresses and URLs before clicking links; hover to check for misspellings (e.g., "paypa1.com" vs. "paypal.com").
      • Ignore urgent requests for sensitive information (e.g., "Your account will be locked!"). Legitimate organizations use secure portals.
      • Use email filters (e.g., Gmail’s phishing tab) and report suspicious messages to service providers.
      • Educate household members on vishing (voice phishing) and smishing (SMS phishing) tactics, such as fake tech support calls.
    • Device and Network Security
      • Keep operating systems, browsers, and applications updated with the latest patches to close vulnerabilities.
      • Use VPNs (e.g., ProtonVPN, NordVPN) on public Wi-Fi to encrypt traffic and prevent man-in-the-middle attacks.
      • Enable full-disk encryption (BitLocker for Windows, FileVault for macOS) to protect data if devices are lost or stolen.
      • Disable unnecessary services (e.g., remote desktop, Bluetooth) when not in use to reduce attack surfaces.
    • Backup and Recovery
      • Implement the 3-2-1 backup rule: 3 copies of data, 2 on different media, 1 offsite (e.g., cloud + external drive).
      • Use versioned backups (e.g., Time Machine, Veeam) to recover from ransomware by restoring pre-encryption files.
      • Test restoration processes annually to ensure backups are functional and accessible.
    • Financial and Online Privacy
      • Monitor credit reports (free annually via AnnualCreditReport.com) and set up fraud alerts with credit bureaus.
      • Use privacy-focused tools (e.g., DuckDuckGo for searches, Signal for messaging) to limit data collection.
      • Avoid oversharing on social media; adjust privacy settings to restrict personal details (birthdays, addresses).
    Critical Insight: The weakest link in cybersecurity is often human error. A single compromised password or clicked phishing link can lead to cascading breaches. Proactive habits—such as MFA and regular audits—reduce reliance on reactive damage control.

    NIST Cybersecurity Framework: Phases and Organizational Application

    The National Institute of Standards and Technology (NIST) Cybersecurity Framework (CSF) provides a voluntary, risk-based approach to managing cybersecurity risks. Structured around five core functions—Identify, Protect, Detect, Respond, and Recover—it aligns with business objectives and regulatory requirements. Organizations adapt the framework by tailoring each phase to their risk profile, resources, and industry standards.
    • Identify
      • Objective: Develop organizational understanding of cybersecurity risk to assets, systems, and capabilities.
      • Key Actions:
        • Conduct asset inventories (hardware, software, data, and third-party dependencies).
        • Map critical business functions and their dependencies (e.g., supply chain, customer data).
        • Identify governance policies (e.g., data classification, access controls) and legal/regulatory obligations (e.g., GDPR, HIPAA).
        • Develop a risk assessment methodology (qualitative/quantitative) to prioritize threats (e.g., ransomware, insider threats).
      • Example: A healthcare provider would identify patient records as high-value assets and HIPAA as a compliance driver.
    • Protect
      • Objective: Implement safeguards to limit or contain cybersecurity incidents.
      • Key Actions:
        • Enforce access controls (e.g., role-based access, PoLP) and identity management (e.g., single sign-on, MFA).
        • Deploy network segmentation to isolate critical systems (e.g., separating IoT devices from corporate networks).
        • Apply data protection measures (encryption, tokenization) for sensitive data in transit and at rest.
        • Train employees on security awareness (e.g., phishing simulations, incident reporting procedures).
        • Maintain asset inventory and patch management to address vulnerabilities proactively.
      • Example: A financial institution would segment trading systems from HR databases and encrypt customer transaction data.
    • Detect
      • Objective: Define activities to identify cybersecurity events in a timely manner.
      • Key Actions:
        • Install intrusion detection/prevention systems (IDS/IPS) and endpoint detection and response (EDR) tools.
        • Monitor logs and alerts from SIEM (Security Information and Event Management) platforms (e.g., Splunk, IBM QRadar).
        • Conduct continuous vulnerability scanning (e.g., Nessus, OpenVAS) and penetration testing (quarterly/annual).
        • Establish anomaly detection for unusual behavior (e.g., sudden data exfiltration, login attempts from new locations).
      • Example: A retail chain detects a brute-force attack on its POS systems via SIEM alerts and isolates affected terminals.
    • Cybersecurity is undergoing rapid transformation due to technological advancements, evolving threat landscapes, and regulatory shifts. Artificial intelligence (AI) and machine learning (ML) are reshaping both defensive strategies and offensive tactics, while emerging technologies such as quantum computing and the Internet of Things (IoT) introduce new vulnerabilities. Simultaneously, supply chain attacks and sophisticated cybercrime models—including ransomware-as-a-service (RaaS)—highlight the escalating financial and operational risks faced by organizations. Regulatory frameworks like GDPR and HIPAA impose stringent compliance requirements, further complicating cybersecurity strategies. This section examines these trends, their implications, and the future challenges they present to global cybersecurity resilience.

      Impact of AI and Machine Learning on Cybersecurity

      AI and ML are dual-edged tools in cybersecurity, enhancing both defensive capabilities and adversarial techniques. On the defensive front, AI-driven anomaly detection systems analyze network traffic patterns, user behavior, and system logs to identify deviations indicative of cyber threats. For example, deep learning models deployed by companies like Darktrace and CrowdStrike autonomously detect zero-day exploits by recognizing subtle deviations from baseline activity. Similarly, natural language processing (NLP) is used to analyze phishing emails, flagging suspicious communications before they reach end-users.

      However, AI also empowers offensive cyber operations. AI-powered attacks leverage automation to scale phishing campaigns, generate convincing deepfake voices or videos, and optimize malware delivery. For instance, GPT-based phishing tools can craft hyper-personalized emails that bypass traditional keyword-based filters. Additionally, adversarial ML manipulates AI models by introducing subtle input perturbations, causing misclassifications—such as evading facial recognition systems or fooling fraud detection algorithms. A notable case is the 2020 AI-driven attack on a U.S. financial institution, where attackers used ML to bypass multi-factor authentication (MFA) by analyzing user behavior patterns and generating realistic biometric spoofs.

      AI in cybersecurity is a high-stakes arms race: defenders use it to predict and prevent attacks, while attackers exploit it to automate and evade detection.
      The cybersecurity landscape has evolved significantly over the past five years, with each trend introducing new risks or defensive paradigms. Below is a chronological breakdown of key developments:
      • 2020: Rise of Remote Work Vulnerabilities The COVID-19 pandemic accelerated digital transformation, exposing weaknesses in remote access protocols (e.g., VPN misconfigurations) and shadow IT adoption. Attackers exploited unpatched vulnerabilities in Zoom, Microsoft Teams, and RDP, leading to a 667% increase in cyberattacks targeting remote workers (Coveware, 2020). This period also saw the emergence of ransomware-as-a-service (RaaS), with groups like REvil and DarkSide demanding millions in ransom payments.
      • 2021: Supply Chain Attacks and SolarWinds Fallout The SolarWinds breach, discovered in December 2020 but executed in 2021, demonstrated the catastrophic potential of supply chain attacks. State-sponsored actors (attributed to Russia’s SVR) compromised the Orion software update mechanism, infiltrating nine U.S. federal agencies and 100 private companies. This incident triggered a global focus on third-party risk management, with organizations adopting Software Bill of Materials (SBOM) requirements to track dependencies.
      • 2022: Quantum Computing Threats and Post-Quantum Cryptography Advances in quantum computing posed existential risks to public-key cryptography (e.g., RSA, ECC), which underpins secure communications. The U.S. National Institute of Standards and Technology (NIST) initiated a post-quantum cryptography standardization project, with CRYSTALS-Kyber and CRYSTALS-Dilithium emerging as leading candidates. Meanwhile, quantum decryption attacks became a theoretical but imminent threat, prompting enterprises to begin migrating to quantum-resistant algorithms.
      • 2023: AI-Driven Cyberattacks and Generative AI Exploitation The proliferation of generative AI tools (e.g., MidJourney, DALL·E) enabled attackers to create hyper-realistic phishing lures, including AI-generated voice clones for voice phishing (vishing). The 2023 "WannaCry 2.0" ransomware strain leveraged AI to automate lateral movement within networks, adapting to defensive countermeasures in real time. Concurrently, AI red-teaming emerged as a defensive technique, where organizations use AI to simulate adversarial tactics and harden their defenses.
      • 2024: IoT and OT Convergence Risks The blurring of lines between IoT (Internet of Things) and OT (Operational Technology) introduced critical infrastructure vulnerabilities. Attacks on OT systems (e.g., Colonial Pipeline 2021, Ukrainian power grid 2015) evolved to target industrial control systems (ICS) via compromised IoT devices. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) issued emergency directives mandating OT asset inventory and segmentation to mitigate wormable vulnerabilities in legacy systems.
      • 2025: Cyber Insurance Market Disruption and Regulatory Scrutiny The cyber insurance market faced a hardening cycle, with underwriters imposing stricter cyber hygiene requirements (e.g., mandatory MFA, regular penetration testing) before issuing policies. High-profile claims, such as the 2023 BlackCat ransomware attack on a major insurer, led to insurance exclusions for state-sponsored attacks. Concurrently, global cybersecurity regulations expanded, with the EU’s NIS2 Directive and U.S. SEC cybersecurity disclosure rules imposing mandatory breach reporting and risk management frameworks.

      Growing Threat of Supply Chain Attacks

      Supply chain attacks exploit the trusted relationships between organizations and their third-party vendors, leveraging compromised software, cloud services, or hardware to infiltrate target networks. Unlike traditional cyberattacks, which directly target an organization’s perimeter, supply chain attacks co-opt legitimate update mechanisms or dependencies to bypass security controls.

      The SolarWinds breach exemplifies this threat model, where attackers compromised the Orion IT management software to distribute malware to thousands of downstream customers. Similarly, the 2020 Codecov breach involved a malicious dependency in the software supply chain, allowing attackers to exfiltrate secrets from CI/CD pipelines of high-profile companies like Microsoft, Netflix, and Slack.

      Key vectors for supply chain attacks include:

      • Software Updates and Patches Attackers inject malware into legitimate software updates, as seen in the 2017 CCleaner breach, where a trojanized update distributed by Piriform (later acquired by Avast) infected 2.27 million users.
      • Third-Party Cloud Services Compromised cloud storage providers or API integrations can serve as entry points. For example, the 2021 Accellion breach exploited a zero-day vulnerability in Accellion’s File Transfer Appliance, leading to data theft from hundreds of organizations, including Singapore’s Ministry of Defense.
      • Hardware Supply Chain Tampering Malicious firmware or hardware implants (e.g., Supermicro motherboard chips) can introduce persistent backdoors. The 2018 "Cloud Hopper" espionage campaign allegedly involved tampered hardware in server components supplied to U.S. government contractors.
      • Open-Source Dependencies Malicious packages in repositories like npm, PyPI, and RubyGems can introduce vulnerabilities. The 2021 "Dependency Confusion" attack demonstrated how attackers could hijack legitimate package names to deliver malware when developers unknowingly pulled compromised versions.
      Mitigation strategies focus on transparency, verification, and segmentation:
      Supply chain attacks are the ultimate "trust exploitation" tactic—organizations must assume that even their most trusted partners could be compromised.

      Cybersecurity Regulations and Global Compliance Requirements

      Cybersecurity regulations enforce minimum security standards, mandate breach disclosure, and impose financial penalties for non-compliance. Below is a comparative analysis of key frameworks:
      Cybersecurity is not a static shield but a dynamic ecosystem where awareness, technology, and policy converge to defend against an ever-expanding threat landscape. The principles of confidentiality, integrity, and availability remain the bedrock, yet their application demands continuous evolution—from implementing multi-factor authentication for individuals to deploying AI-driven threat detection for enterprises. As supply chain attacks and ransomware-as-a-service models reshape the tactics of cybercriminals, organizations must adopt a zero-trust mindset and leverage frameworks like NIST to transform security from a reactive posture into a strategic advantage. The future of cybersecurity hinges on collaboration, innovation, and an unwavering commitment to safeguarding digital trust, ensuring that progress in technology does not outpace the defenses that protect it.

      Regulation

    Leave a Comment

    Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.