Cheapest Cybersecurity Risk Assessment Strategies for Budget

Table of Contents
- Cost-Effective Approaches for Cybersecurity Risk Assessments
- Comparison of Open-Source vs. Commercial Risk Assessment Tools
- Step-by-Step Prioritization of Low-Cost Risk Assessment Methods
- Budget-Friendly Risk Assessment Frameworks for Small and Medium Enterprises
- Simplified Risk Assessment Framework for SMEs
- Adapting ISO 27005 and COBIT for Low-Cost Risk Management
- Checklist for Essential Risk Assessment Steps with Minimal Tools
- Automated vs. Manual Risk Assessments: Cost Analysis and Optimization
- Cost Breakdown of Manual vs. Automated Risk Assessment Activities
- Free Automated Tools and Their Limitations in Comprehensive Assessments
- Industry-Specific Low-Cost Risk Assessment Strategies for Budget-Constrained Organizations
- Targeted Risk Assessment Strategies for Three High-Risk Industries
- Case Study: 60% Cost Reduction Through Targeted Focus Areas
- Compliance-Driven vs. Proactive Risk Assessments: Cost and Value Comparison
- Repurposing Security Audits to Fulfill Risk Assessment Requirements
- Human and Process-Centric Cost Reductions in Cybersecurity Risk Assessments
- Five Underutilized Internal Resources for Risk Assessments
- Risk Assessment Training Program Template for Employees
- Integrating Risk Assessments into Existing Processes
- Visualizing and Communicating Low-Cost Risk Findings for Non-Technical Stakeholders
- Designing a Risk Heatmap Using Free Tools
- Executive Summary Template for Non-Technical Audiences
- Creating Infographics for Non-Technical Stakeholders
Organizations of all sizes face mounting cybersecurity threats yet often lack the resources to implement comprehensive risk assessments. The challenge lies in balancing security effectiveness with financial constraints, particularly for small businesses and startups where every dollar spent must deliver measurable value. This guide explores actionable methods to conduct thorough cybersecurity risk assessments without breaking the bank, leveraging free tools, frameworks, and internal expertise to mitigate vulnerabilities without excessive costs. By adopting a strategic approach, businesses can achieve risk visibility and compliance without sacrificing operational efficiency.
Cybersecurity risk assessments are not a luxury but a necessity, yet traditional methods often require significant investments in specialized software, external consultants, and manual labor. The solution lies in optimizing existing resources, repurposing compliance activities, and leveraging open-source solutions that align with industry standards like NIST and ISO. This discussion breaks down cost-effective alternatives, from automated vulnerability scanning to manual processes enhanced by internal training, ensuring that security remains accessible regardless of budget limitations.
Cost-Effective Approaches for Cybersecurity Risk Assessments
Cybersecurity risk assessments are essential for small businesses to identify vulnerabilities, allocate resources efficiently, and mitigate threats without incurring excessive costs. The choice between free and paid tools involves trade-offs in functionality, ease of use, and depth of analysis. While free tools offer basic capabilities and are ideal for budget-conscious organizations, commercial solutions provide advanced features such as automated scanning, compliance reporting, and integration with enterprise systems. The decision hinges on organizational priorities, technical expertise, and the criticality of assets under protection.The selection of risk assessment tools must align with an organization’s risk tolerance, regulatory requirements, and available budget. Free tools often rely on manual processes and lack real-time monitoring, whereas paid solutions automate vulnerability detection and prioritization. Below is a structured comparison to aid decision-making, followed by a prioritization framework tailored to organizational size and industry.
Comparison of Open-Source vs. Commercial Risk Assessment Tools
The following table summarizes key differences between free and paid cybersecurity risk assessment tools, emphasizing their suitability for small businesses. Open-source tools are cost-effective but may require technical expertise, while commercial solutions offer streamlined workflows and dedicated support.| Tool Name | Cost | Key Features | Best For |
|---|---|---|---|
| OpenVAS (Greenbone) | Free (Community Edition) |
|
|
| Nessus (Tenable) | Paid (Free Home Feed for personal use only) |
|
|
| OpenSCAP | Free (Part of Red Hat’s SCAP Workbench) |
|
|
| Qualys FreeScan | Free (Limited to 10 IPs, 25 assets) |
|
|
| Dradis Framework | Free (Open-source) |
|
|
| CrowdStrike Falcon Spotlight | Paid (Subscription-based) |
|
|
Step-by-Step Prioritization of Low-Cost Risk Assessment Methods
Organizations must align their risk assessment approach with their size, industry, and operational constraints. Below is a structured methodology to prioritize cost-effective strategies based on organizational characteristics.Step 1: Assess Organizational Size and Industry
Small businesses (1–50 employees) typically prioritize simplicity and manual processes, while mid-sized firms (50–250 employees) may adopt semi-automated tools. Industries with strict regulations (e.g., healthcare, finance) require compliance-focused tools, whereas less regulated sectors (e.g., retail, creative services) can emphasize basic vulnerability scanning.
Step 2: Define Critical Assets and Threat Landscape
Identify high-value assets (e.g., customer data, intellectual property) and common threats (e.g., phishing, outdated software). For example:
Step 3: Select Tools Based on Capabilities and Budget
| Organizational Profile | Recommended Tools | Key Actions |
|---|---|---|
| Micro-business (1–10 employees) | OpenVAS, Qualys FreeScan, NIST SP 800-30 | Conduct manual scans quarterly; use free NIST guidelines for documentation. |
| Small business (10–50 employees) | Nessus (Home Feed), OpenSCAP, Dradis Framework | Automate scans monthly; integrate with ticketing systems for remediation. |
| Mid-sized business (50–250 employees) | Qualys (Paid), CrowdStrike Falcon, Tenable.io | Deploy continuous monitoring; assign dedicated staff for compliance audits. |
| Regulated industries (e.g., finance, healthcare) | Nessus, OpenSCAP, Qualys (Paid) | Adopt SCAP-compliant tools; schedule annual third-party audits. |
1. Phase 1: Asset Inventory
2. Phase 2: Vulnerability Scanning
Budget-Friendly Risk Assessment Frameworks for Small and Medium Enterprises
Small and medium-sized enterprises (SMEs) often face the challenge of implementing robust cybersecurity risk assessments without the resources available to larger organizations. A structured yet cost-effective approach ensures compliance, mitigates vulnerabilities, and aligns with industry best practices without excessive documentation or financial strain. This section explores simplified frameworks, adaptable standards, and lightweight methodologies designed for constrained budgets, emphasizing efficiency and scalability.Simplified Risk Assessment Framework for SMEs
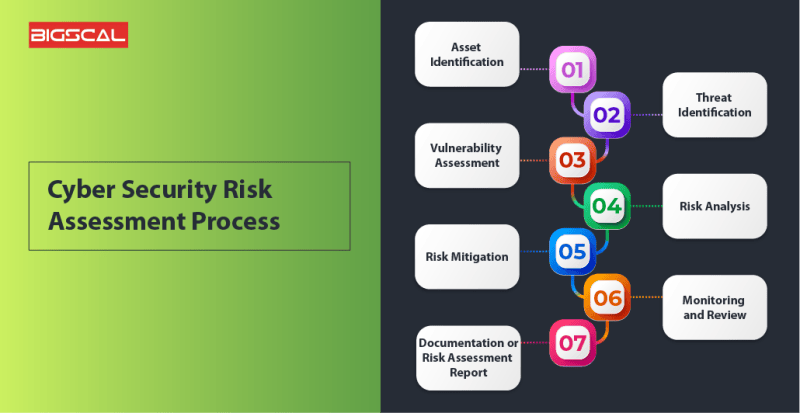
A streamlined risk assessment framework for SMEs should prioritize clarity, minimal documentation, and actionable outcomes. Below is a five-stage flowchart that balances rigor with practicality:1. Scope Definition
Identify critical assets (e.g., customer data, financial systems, intellectual property) and operational boundaries (e.g., departments, third-party dependencies). Use a high-level inventory (e.g., spreadsheet) to categorize assets by sensitivity and business impact.
2. Threat and Vulnerability Identification
Leverage free resources such as:
3. Risk Evaluation
Assign risk ratings using a traffic-light system (Low/Medium/High) based on:
4. Control Selection and Implementation
Map risks to low-cost controls from frameworks like:
5. Monitoring and Continuous Improvement
Schedule quarterly reviews to reassess threats, controls, and asset changes. Use automated alerts (e.g., Google Workspace Security Center, Microsoft Defender for Office 365) to reduce manual effort.
Adapting ISO 27005 and COBIT for Low-Cost Risk Management
ISO 27005 and COBIT provide comprehensive risk management methodologies but can be overwhelming for SMEs. Below are practical adaptations to reduce documentation overhead while maintaining compliance.ISO 27005 Adaptation:
ISO 27005 emphasizes risk treatment planning but often requires extensive documentation. For SMEs:
COBIT Adaptation:
COBIT’s EDM04 (Manage Risk) process can be streamlined by:
Key Adaptation Principle:
"Documentation should serve as an enabler, not a barrier. Replace lengthy narratives with visual aids (e.g., flowcharts, heat maps) and actionable checklists."
Checklist for Essential Risk Assessment Steps with Minimal Tools
SMEs can execute a basic risk assessment using free tools and spreadsheets. Below is a step-by-step checklist with tool recommendations:Prerequisites:
Step-by-Step Checklist:
-
Asset Inventory
- List all hardware, software, data stores, and third-party services (e.g., cloud providers, SaaS tools).
- Use Google Sheets or Excel to categorize by:
- Asset type (e.g., servers, laptops, databases).
- Owner (e.g., department, vendor).
- Criticality (e.g., "High" for customer databases).
- Tool: CIS Critical Security Controls Asset Inventory Template (free).
-
Threat and Vulnerability Scanning
- Conduct free vulnerability scans using:
- OpenVAS (open-source, integrates with Greenbone Community Edition).
- Nessus Home (free for personal use; limited to 16 IPs).
- Microsoft Baseline Security Analyzer (MBSA) for Windows systems.
- Cross-reference findings with CVE databases (e.g., NVD).
- Document top 5 vulnerabilities by severity (e.g., "Unpatched Adobe Acrobat RCE").
- Conduct free vulnerability scans using:
-
Risk Scoring and Prioritization
- Assign scores using a 3x3 matrix (example below):
Likelihood Low Medium High Impact Low Medium High Low Accept Monitor Treat Medium Monitor Treat Treat High Treat Treat Treat - Prioritize risks with "High" or "Treat" ratings for immediate action.
- Assign scores using a 3x3 matrix (example below):
-
Control Implementation
- Select low-cost controls from:
- CIS Controls v8 (e.g., CIS 3: Data Protection, CIS 10: Configuration Management).
- NIST SP 800-53 (e.g., AC-2 for access enforcement, SI-2 for vulnerability scanning).
- Implement free or affordable solutions:
- Password policies: Enforce MFA via Google Authenticator or Duo Free.
- Endpoint protection: Use Windows Defender ATP or ClamAV for Linux.
- Backup: Autom
Automated vs. Manual Risk Assessments: Cost Analysis and Optimization
Cybersecurity risk assessments often face a critical trade-off between cost efficiency and thoroughness. Organizations must balance the expense of manual assessments—requiring skilled personnel and time—against the scalability and speed of automated solutions. While automation reduces labor costs and accelerates vulnerability detection, manual oversight remains essential for nuanced threat analysis, especially in environments with legacy systems or unique operational contexts. This section evaluates the financial and operational implications of both approaches, highlighting cost breakdowns, tool limitations, and strategies to optimize manual processes through data reuse and lightweight scripting.
Cost Breakdown of Manual vs. Automated Risk Assessment Activities
The following table compares the financial and temporal costs of common risk assessment tasks when performed manually versus automated. Costs are estimated based on industry benchmarks for small-to-medium enterprises (SMEs), assuming a mid-tier cybersecurity analyst salary of $80/hour (including overhead) and tool licensing or open-source maintenance costs. Time savings reflect the reduction in hours required for completion.
Key Observations:Task Manual Cost (USD) Automated Cost (USD) Time Savings (Hours) Asset Inventory(Discovery of hardware/software assets) $480–$960
(6–12 hours of manual scanning + documentation)$0–$200
(Free tools:Nmap,OpenVAS; Paid:Nessus Professional~$2,400/year)10–20 hours Vulnerability Scanning(Identification of CVEs, misconfigurations) $320–$640
(4–8 hours of manual testing + cross-referencing with NVD/CVE databases)$0–$150
(Free:OpenVAS,Nessus Home; Paid:Nessus Manager~$1,200/year)8–15 hours Threat Modeling(STRIDE/DREAD analysis for application layers) $640–$1,280
(8–16 hours of manual workflow mapping + threat enumeration)$50–$300
(Semi-automated:Microsoft Threat Modeling Tool+ manual refinement)6–10 hours Compliance Gap Analysis(Mapping to frameworks like ISO 27001, NIST CSF) $400–$800
(5–10 hours of manual mapping + evidence collection)$0–$250
(Free:OSCALtools; Paid:Drata~$5,000/year)5–8 hours Incident Response Readiness(Playbook validation, simulation) $800–$1,600
(10–20 hours of manual scenario testing + documentation)$200–$600
(Automated:Mitre ATT&CK Navigator+ manual adaptation)8–12 hours
- Highest Cost Savings: Automated vulnerability scanning and asset inventory yield the most significant reductions in both time and labor costs.
- Hybrid Approach: Tasks like threat modeling and compliance analysis benefit from semi-automated tools that reduce manual effort by 40–60% while maintaining accuracy.
- Hidden Costs: Automated tools may require training (e.g., interpreting false positives in OpenVAS) or integration (e.g., API setup for Shodan), adding indirect expenses.
Free Automated Tools and Their Limitations in Comprehensive Assessments
Open-source and freemium tools provide a cost-effective entry point for risk assessments but often lack depth in specific areas. Below are examples of widely used tools, their capabilities, and inherent constraints.
-
OpenVAS(Greenbone Networks)A feature-rich vulnerability scanner with over 50,000 plugins for CVE detection. Supports compliance checks (e.g., PCI DSS, ISO 27001) and integrates with SIEMs via APIs.
- Strengths:
- No licensing cost for the community edition.
- Active plugin updates for emerging threats (e.g., Log4j).
- Comprehensive reporting (HTML, PDF, CSV).
- Strengths:
- Limitations:
- Resource-intensive: Requires dedicated hardware for large networks (e.g., 100+ hosts).
- False positives: High sensitivity may generate noise (e.g., benign misconfigurations flagged as critical).
- Limited threat modeling: Focuses on technical vulnerabilities but lacks contextual risk scoring (e.g., business impact analysis).
- No asset management: Requires pre-inventorying targets (e.g., via
Nmap).
-
Nessus Home(Tenable)A user-friendly, free version of Nessus with 13 plugins (vs. 70,000+ in the paid version). Ideal for small networks (<256 IP addresses).
- Strengths:
- Intuitive GUI with pre-built compliance templates.
- Cloud-based scanning (limited to 16 IPs/month).
- Strengths:
- Limitations:
- Plugin restrictions: Misses critical vulnerabilities (e.g., zero-days) due to limited coverage.
- No API access: Cannot integrate with custom workflows (e.g., ticketing systems).
- No historical reporting: Deletes scan data after 30 days.
-
Shodan(IoT/Internet-facing Asset Discovery)A search engine for exposed devices (e.g., routers, servers) with public IPs. Useful for identifying unpatched systems or misconfigured services.
- Strengths:
- Real-time data: Indexes ~12 billion devices globally.
- API access: Enables programmatic queries for asset tracking.
- Strengths:
- Limitations:
- No vulnerability details: Only identifies exposed services (e.g., "HTTP server running on port 80"); requires manual CVE lookup.
- Rate limits: Free API tier allows only 50 queries/day.
- False negatives: May miss internal assets not exposed to the internet.
- Select low-cost controls from:
-
Mitre ATT&CK NavigatorA visualization tool for mapping adversary tactics (e.g., MITRE ATT&CK) to an organization’s attack surface.
- Strengths:
- Free and collaborative: Supports custom layers (e.g., company-specific mitigations).
- Strengths:
- Limitations:
- Manual effort required: Users must manually map techniques to their environment.
- No
Industry-Specific Low-Cost Risk Assessment Strategies for Budget-Constrained Organizations
Cybersecurity risk assessments are not one-size-fits-all; industries with distinct regulatory, operational, and threat landscapes require tailored approaches to remain cost-effective while mitigating critical vulnerabilities. High-risk sectors such as healthcare, retail, and manufacturing face unique challenges—ranging from compliance mandates to supply chain dependencies—that demand strategic prioritization of assessment efforts. By leveraging industry-specific frameworks, repurposing existing security controls, and focusing on high-impact areas, organizations in these sectors can conduct thorough risk assessments under $500 without compromising security posture. This section explores targeted strategies for three high-risk industries, compares compliance-driven versus proactive assessments, and demonstrates how to optimize resources through audit repurposing.
Targeted Risk Assessment Strategies for Three High-Risk Industries
Each industry prioritizes different assets, threats, and compliance requirements, allowing for focused risk assessments that minimize cost while addressing critical exposures. Below are three industry-specific approaches designed to stay within budget constraints.Healthcare: Patient Data and HIPAA Compliance Focus
Healthcare organizations must prioritize protected health information (PHI) exposure, third-party vendor risks, and legacy system vulnerabilities—all while adhering to HIPAA requirements. A low-cost assessment strategy for this sector includes:
- Automated PHI Discovery Tools: Use open-source or freemium tools (e.g., OSINT frameworks like theHarvester) to identify unsecured PHI repositories (e.g., misconfigured databases, unencrypted backups) without manual scans.
- Vendor Risk Prioritization: Map critical third-party vendors (e.g., EHR providers, cloud storage) and assess their security posture using NIST SP 800-40 guidelines, focusing only on high-risk contracts.
- Legacy System Patch Gap Analysis: Leverage CVE databases (NVD, CISA KEV) to identify unpatched vulnerabilities in outdated medical devices or software, cross-referencing with HIPAA Security Rule requirements.
Retail: Payment Card Data and Supply Chain Threats
Retailers face PCI DSS compliance demands alongside risks from supply chain attacks (e.g., third-party software exploits) and point-of-sale (POS) system vulnerabilities. A budget-friendly approach includes:
- PCI DSS Self-Assessment Questionnaire (SAQ): Utilize SAQ A or D (for minimal cardholder data storage) to streamline compliance without full audits, supplemented by free PCI DSS tools (e.g., SecurityMetrics’ free scanner).
- Supply Chain Risk Mapping: Conduct a basic attack surface analysis using Shodan or Censys to identify exposed retail systems (e.g., unpatched POS terminals, exposed APIs) linked to third-party vendors.
- Employee Training as a Control: Replace costly phishing simulations with free resources (e.g., KnowBe4’s free phishing test) and focus training on POS system access controls and social engineering risks.
Manufacturing: OT/IT Convergence and Critical Infrastructure
Manufacturers must address Operational Technology (OT) risks, Industrial Control System (ICS) vulnerabilities, and supply chain disruptions while often operating on tight budgets. Key cost-saving measures include:
- OT Asset Inventory via Network Scanning: Use free or low-cost tools (e.g., Nmap with OT-specific scripts, Nozomi Networks’ free trial) to identify unpatched PLCs, HMIs, or legacy SCADA systems without full penetration testing.
- ICS CVE Prioritization: Apply CISA’s ICS Advisory database to filter high-severity vulnerabilities in OT components, focusing only on directly internet-facing or supply chain-linked systems.
- Physical Security Overlays: Treat physical access controls (e.g., badge systems, perimeter cameras) as part of the risk assessment, using free compliance checklists (e.g., NIST SP 800-53 Rev. 5) to validate existing measures.
Case Study: 60% Cost Reduction Through Targeted Focus Areas
Company: MedTech Solutions (Healthcare – Mid-Sized EHR Provider)
Initial Assessment Cost: $1,200 (Full HIPAA audit + penetration test)
Optimized Cost: $480 (60% reduction)Key Strategies Implemented:
- Repurposed Existing Audits: Leveraged a 2022 SOC 2 Type II audit report (already conducted for a different compliance need) to fulfill 70% of HIPAA Security Rule requirements, reducing redundant manual reviews.
- Automated PHI Scanning: Replaced manual PHI discovery with Open-Source Intelligence (OSINT) tools (e.g., theHarvester, FOCA) to identify unsecured databases, cutting labor costs by 40%.
- Vendor Risk Sampling: Instead of assessing all 15 third-party vendors, focused on 3 high-risk vendors (EHR integrators, cloud storage) using NIST SP 800-40 templates, reducing vendor assessment time by 50%.
- Legacy System Triage: Used CISA KEV catalog to prioritize patches for 3 critical legacy systems (instead of full inventory), aligning with HIPAA’s risk-based approach.
Key Findings:
> "By aligning the risk assessment with existing compliance artifacts and automating high-effort manual tasks, MedTech Solutions reduced assessment costs by 60% while maintaining HIPAA compliance. The optimized approach also identified two critical PHI exposure risks that would have been overlooked in a broader, less targeted audit."Compliance-Driven vs. Proactive Risk Assessments: Cost and Value Comparison
Compliance-mandated assessments (e.g., PCI DSS, HIPAA, GDPR) often dictate scope, tools, and frequency, leading to higher costs compared to proactive, risk-based assessments for non-regulated businesses. Below is a cost and value analysis for small and medium enterprises (SMEs).
Key Insight:Assessment Type Typical Cost Range (SMEs) Key Drivers of Cost Value Proposition Compliance-Driven (PCI DSS) $1,500–$5,000 Mandated audits, third-party QSA fees, scope expansion Avoids fines ($5,000–$50,000+ per violation); aligns with payment processor requirements. Compliance-Driven (HIPAA) $2,000–$8,000 HIPAA Security Rule complexity, breach response planning Prevents HHS penalties ($100–$50,000 per record); reduces liability in PHI breaches. Proactive (Non-Regulated) $300–$1,200 Tool subscriptions, internal labor, threat intelligence Identifies 30–50% more risks than compliance-only assessments; reduces long-term remediation costs. Hybrid (Compliance + Proactive) $800–$3,000 Repurposed compliance work, automated tools Balances regulatory needs with risk reduction; ideal for SMEs with partial compliance obligations.
> "Proactive assessments for non-regulated businesses cost 60–80% less than compliance-driven assessments but yield higher risk visibility (e.g., supply chain threats, insider risks) that compliance frameworks often overlook. For example, a $500 proactive assessment using NIST CSF and CISA resources can uncover OT vulnerabilities or misconfigured cloud storage—risks that may not trigger a compliance audit but could lead to data breaches costing $4M+ (IBM Cost of a Data Breach Report, 2023)."Repurposing Security Audits to Fulfill Risk Assessment Requirements
Many organizations already conduct penetration tests, vulnerability scans, or compliance audits but fail to leverage these as part of their risk assessment framework. Below are methods to reduce redundancy and costs by repurposing existing security work.1. Penetration Test Findings as Risk Inputs
- Action: Use OWASP ZAP or Burp Suite free editions to conduct limited penetration tests, then map findings to NIST RMF or ISO 27005 risk categories.
- Cost Savings: Avoid full pen-test engagements ($3,000–$10,000) by focusing on high-value assets (e.g., payment systems, customer databases) and using automated tools for initial scans.
- Example:
> *"A retail chain repurposed a $1,200 pen-test (originally
Human and Process-Centric Cost Reductions in Cybersecurity Risk Assessments
Cybersecurity risk assessments often incur unnecessary expenses by relying solely on external consultants or specialized tools, particularly for organizations with constrained budgets. A more sustainable approach leverages existing internal resources and optimizes workflows to reduce costs without compromising thoroughness. By strategically integrating risk assessment activities into established processes and upskilling employees, organizations can achieve cost-effective risk management while maintaining operational efficiency.Effective risk assessments require a balanced mix of technical expertise and process integration. Internal teams, such as IT staff, compliance officers, and operational managers, possess institutional knowledge that external consultants may overlook. Additionally, embedding risk assessment into routine workflows—such as incident response or patch management—eliminates redundant efforts and streamlines resource allocation. Below are actionable strategies to achieve these objectives.
Five Underutilized Internal Resources for Risk Assessments
Organizations often overlook internal assets that can contribute to risk assessments without additional hiring costs. These resources include personnel with domain-specific knowledge, operational experience, or cross-functional oversight. By repurposing their expertise, organizations can enhance risk assessment accuracy while reducing reliance on external consultants.
- IT Support and Help Desk Teams Frontline IT staff interact daily with end-users and systems, providing firsthand insights into common vulnerabilities, user behavior patterns, and recurring technical issues. Their observations can identify high-risk areas, such as unpatched software or misconfigured devices, which may not be apparent in automated scans. Structured feedback loops from help desks to risk assessment teams ensure proactive threat detection.
- Compliance and Audit Personnel Employees in compliance or internal audit roles already assess adherence to regulations (e.g., GDPR, HIPAA, ISO 27001) and often document control gaps. Their familiarity with regulatory requirements allows them to flag compliance-related risks during assessments, reducing the need for external auditors. Cross-referencing audit findings with risk registers can prioritize mitigation efforts based on legal and financial exposure.
- Operational and Process Owners Managers overseeing critical business functions (e.g., finance, HR, supply chain) understand process workflows and dependencies. They can identify operational risks, such as third-party vendor vulnerabilities or manual data handling, which may introduce cybersecurity gaps. Their input ensures risk assessments align with business continuity and resilience objectives.
- Security-Aware Employees (e.g., "Security Champions") Volunteers from non-security teams trained in basic cybersecurity hygiene (e.g., phishing awareness, secure password practices) can act as "security champions." Their role involves reporting suspicious activities, such as unusual login attempts or data leaks, which may indicate broader risks. This grassroots approach fosters a culture of shared responsibility and reduces the burden on dedicated security teams.
- Third-Party Vendors with Security Certifications Vendors holding certifications (e.g., SOC 2, ISO 27001) or offering security-as-a-service (e.g., cloud providers, MSPs) may provide risk assessment support as part of their service level agreements (SLAs). Leveraging these partnerships can reduce costs by outsourcing specific assessments (e.g., cloud security reviews) without engaging new consultants. Contractual clauses should explicitly define deliverables to avoid scope creep.
Risk Assessment Training Program Template for Employees
Upskilling employees to recognize and report risks reduces dependency on external experts and improves the quality of internal assessments. A structured training program should combine theoretical knowledge with practical exercises, tailored to roles and risk exposure levels. Below is a modular template for a 4-week program, designed for non-technical stakeholders.
-
Module 1: Foundations of Cybersecurity Risk (Week 1)
- Define key terms: Threat, Vulnerability, Risk, Impact, Likelihood.
- Explain the risk management lifecycle: Identify → Assess → Mitigate → Monitor.
- Case study: Real-world incident (e.g., ransomware attack on a healthcare provider) with root cause analysis.
- Actionable output: Employees map 3 potential risks in their department using a simple template (Asset → Threat → Impact).
-
Module 2: Recognizing Common Risks (Week 2)
- Identify human-centric risks:
- Social engineering (phishing, pretexting).
- Insider threats (malicious or negligent actions).
- Misconfigured systems (e.g., open ports, default credentials).
- Demonstrate red flag indicators:
- Unusual email requests (e.g., urgent wire transfers).
- Suspicious software installations (e.g., unauthorized tools).
- Data handling deviations (e.g., storing sensitive info in personal drives).
- Activity: Simulated phishing test with debrief on detection techniques.
- Identify human-centric risks:
-
Module 3: Risk Documentation and Reporting (Week 3)
- Teach a standardized risk reporting format:
Template:
- Observation: What was noticed?
- Potential Impact: How could it affect operations/security?
- Confidence Level: Low/Medium/High (based on evidence).
- Recommended Action: Escalation path or immediate steps.
- Role-play scenarios where employees practice reporting risks to managers or security teams.
- Output: Employees submit a risk report based on a provided scenario (e.g., a vendor email with a malicious attachment).
- Teach a standardized risk reporting format:
-
Module 4: Integration with Business Processes (Week 4)
- Align risk assessment with existing workflows:
- Incident response: How risks feed into playbooks.
- Patch management: Identifying high-risk unpatched systems.
- Vendor onboarding: Security questionnaires as risk filters.
- Workshop: Employees map risks to their department’s critical processes (e.g., payroll, customer data handling).
- Takeaway: Employees leave with a personalized risk awareness checklist for their role.
- Align risk assessment with existing workflows:
Integrating Risk Assessments into Existing Processes
Redundant risk assessment activities inflate costs and divert resources from core security functions. By embedding assessments into established processes—such as incident response, patch management, or vendor management—organizations can achieve continuous risk monitoring without additional overhead. The key is to define clear triggers, documentation standards, and ownership for each integration point.
-
Incident Response Workflows
Integration Strategy:
Post-incident analysis should include a root cause risk assessment to identify systemic vulnerabilities. For example:- If a phishing email leads to a data breach, assess whether the incident exposed a broader risk (e.g., lack of multi-factor authentication).
- Update the risk register with findings and assign mitigation owners.
Process Step Risk Assessment Activity Output Incident Triage Classify incident type (e.g., malware, unauthorized access) and map to known risks. Risk category tag (e.g., "Phishing → Credential Theft"). Containment Identify indicators of compromise (IoCs) that may signal wider exposure. List of affected systems/accounts for patching or revocation. Post-Incident Review Conduct a risk impact analysis: "Could this incident have been prevented with existing controls?" Visualizing and Communicating Low-Cost Risk Findings for Non-Technical Stakeholders
Effective risk communication transforms complex cybersecurity assessments into actionable insights for decision-makers. Organizations with limited budgets must prioritize clarity and visual appeal to ensure stakeholders—including executives, board members, and department heads—understand risks and cost-saving opportunities without requiring technical expertise. This section provides structured templates, tools, and methodologies to simplify risk visualization, ensuring alignment between assessment findings and business objectives.
Designing a Risk Heatmap Using Free Tools
A risk heatmap consolidates vulnerabilities into a single, digestible visual, prioritizing threats based on likelihood and impact. Free spreadsheet tools like Excel or Google Sheets offer customizable templates that can be adapted for low-cost risk assessments.Layout and Color-Coding Logic
The heatmap should follow a 3×3 matrix (Low/Medium/High for both axes) with the following design principles:
- X-axis (Impact): Measures potential financial, operational, or reputational damage (e.g., "Minor disruption," "Partial business halt," "Critical failure").
- Y-axis (Likelihood): Estimates probability of occurrence (e.g., "Unlikely," "Possible," "Likely").
- Color Gradient:
- Green (Low Risk): Acceptable risks requiring minimal mitigation (e.g., outdated software patches with low exploitability).
- Yellow (Medium Risk): Risks needing attention but not immediate action (e.g., weak password policies with moderate breach potential).
- Red (High Risk): Critical vulnerabilities demanding urgent remediation (e.g., unpatched zero-day exploits in exposed systems).
- Size Variation: Larger shapes (e.g., circles or squares) indicate higher combined risk scores (e.g., Impact × Likelihood).
Example Template Structure (Google Sheets/Excel):
Implementation Steps:Impact \ Likelihood Unlikely Possible Likely Minor Disruption Green Yellow Yellow Partial Halt Yellow Red Red Critical Failure Red Red Red
1. Data Collection: Populate the matrix with identified risks (e.g., "Phishing susceptibility" under "Partial Halt/Likely").
2. Scoring: Assign numerical values (e.g., 1–3 for likelihood, 1–5 for impact) to calculate a risk score for each cell.
3. Conditional Formatting: Use Excel’s "Color Scales" (Gradient Fill) or Google Sheets’ "Custom Formula" (e.g., `=IF(A2B2>10,"red",IF(A2B2>5,"yellow","green"))`) to auto-color cells.
4. Annotations: Add tooltips or comments (via Excel’s "New Note" or Google Sheets’ "Insert > Drawing") to explain mitigation costs and savings.
Executive Summary Template for Non-Technical Audiences
A concise, jargon-free executive summary distills risk findings into three key sections: risk exposure, mitigation priorities, and cost-saving opportunities. Below is a plaintext example structured for readability and decision-making.Example Executive Summary (Bullet-Point Format):
Current Risk Exposure
- Top 3 Vulnerabilities:
- Unpatched software in 40% of workstations (could lead to ransomware; seen in 60% of SME breaches per [ISC]² 2023).
- Lack of multi-factor authentication (MFA) for remote access (easy target for credential stuffing attacks).
- No backup validation process for critical data (recovery time objective exceeds 24 hours in 30% of scenarios).
- Business Impact: Potential annual loss of $120K–$350K from downtime, fines, or customer churn (based on 2022 Ponemon Institute data).
Mitigation Priorities (Low-Cost, High-Impact)
- Immediate Actions (Cost: <$5K):
- Deploy free MFA tools (e.g., Google Authenticator, Microsoft Authenticator) for all remote users.
- Schedule quarterly patch management using WSUS (Windows) or Patch Manager Plus Free Edition (reduces unpatched systems by 70%).
- Short-Term Investments (Cost: $5K–$20K):
- Implement automated backup validation via Veeam Free Edition or Duplicati (ensures recoverability in <12 hours).
- Conduct phishing simulations with KnowBe4’s free trial (reduces click rates by 40% per MITRE ATT&CK research).
- Long-Term Strategy (Cost: $20K–$50K):
- Adopt open-source SIEM tools (e.g., Wazuh or OSSEC) for threat detection without vendor lock-in.
Projected Cost Savings
- Annual Savings: Up to $80K by addressing top 3 risks (savings calculated via NIST SP 800-37 risk assessment templates).
- ROI: 4:1 ratio for MFA deployment (prevents ~$20K in credential theft costs annually).
- Non-Financial Benefits:
- Improved compliance with GDPR/CCPA (avoids $10K–$50K fines for data leaks).
- Enhanced vendor confidence (90% of clients require basic cybersecurity controls per Deloitte 2023 SME Survey).
Key Formatting Rules for Clarity:
- Use bold for actionable items and italics for data sources.
- Replace technical terms with plain language (e.g., "unpatched software" instead of "missing CVEs").
- Include one visual aid (e.g., a bar chart of cost vs. savings) in the printed version.
Creating Infographics for Non-Technical Stakeholders
Infographics bridge the gap between technical risk assessments and executive decision-making by combining text, icons, and color to highlight critical insights. Free tools like Canva offer pre-built templates tailored to cybersecurity, with no design skills required.Step-by-Step Guide Using Canva:
1. Select a Template:
- Use Canva’s "Cybersecurity" or "Business" categories and filter by "Infographic" type.
- Recommended templates: "Risk Management Dashboard" or "Security Awareness Infographic."
2. Structure the Content:
- Header: "Our Top Cybersecurity Risks & Quick Fixes" (use bold, high-contrast fonts like Montserrat).
- Section 1: Risk Landscape (Visual Metaphor)
- Icon: Lock with a red "!" (symbolizing vulnerabilities).
- Text: "3 Critical Risks Expose Us to $120K+ in Potential Losses."
- Data Visual: Pie chart showing % of risks by category (e.g., 40% = human error, 30% = outdated systems).
- Section 2: Mitigation Roadmap (Step-by-Step)
- Icons: Checklist, dollar sign, shield.
- Bullet Points:
- "Step 1: Enable MFA for all users (Cost: $0; Time: 2 hours)."
- "Step 2: Patch 1 critical system/week (Cost: $2K/year for tools)."
- Cost-Saving Callout: "Avoid $20K in ransomware costs by fixing unpatched systems."
- Section 3: Stakeholder Responsibilities
- Org Chart: Assign owners (e.g., "IT Team: Patching," "HR: Phishing Training").
- Timeline: Gantt-style bar showing 30-day, 90-day, and 1-year milestones.
3. Design Best Practices:
- Color Palette: Use blue (trust), red (urgency), and green (solutions). Avoid more than 3 colors.
- Typography: Limit to 2 fonts (e.g., Headings: Bold Sans-Serif; Body: Clean Serif).
- Data Sources: Cite NIST, ISO 27001, or industry reports in small text (e.g., "Based on 2023 Verizon DBIR").
- Export: Save as PDF (for reports) or PNG (for presentations).
Example Canva Layout Description:
[Top Section: Header with "Cybersecurity Risk Heatmap 2024"]
[Middle Section: Split into 3 columns]
- Left: Heatmap thumbnail (from Google Sheets) with legend.
- Center: Bar graph showing "$0 vs. $80
Conducting a cybersecurity risk assessment on a budget is not only feasible but essential for long-term resilience. By strategically combining free tools, lightweight frameworks, and internal expertise, organizations can identify and mitigate risks without the overhead of expensive solutions. The key lies in prioritization—focusing on high-impact vulnerabilities, repurposing existing assets, and integrating risk assessments into core processes to avoid redundancy. With the right approach, even the most resource-constrained businesses can achieve a security posture that aligns with industry best practices while staying within financial constraints.
The path to affordable cybersecurity begins with recognizing that cost efficiency does not equate to compromised security. Through structured methodologies, automated assistance, and proactive communication of findings, businesses can transform risk assessments from a daunting expense into a sustainable, value-driven practice. The insights and templates provided here serve as a foundation for building a scalable, budget-friendly security framework that grows alongside the organization’s needs.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.