Best compliance tool selection guide for modern enterprises

Table of Contents
- Core Features of Leading Compliance Tools: Functionalities and Workflow Integration
- Automation Capabilities in Compliance Tools
- Real-Time Monitoring and Integration with Existing Systems
- Policy Management Modules: Structure and Enforcement
- Risk Assessment Frameworks: Methodologies and AI Enhancements
- Audit Trails: Immutable Records and Forensic Analysis
- Industry-Specific Compliance Solutions: Tailored Tools for Regulatory Excellence
- RegTech Platforms for Financial Institutions: Automating Regulatory Reporting and AML Compliance
- Healthcare Compliance Tools: EHR Integration and PHI Protection Under HIPAA and OCR Rules
- Data Privacy Compliance Tools: GDPR, CCPA, and Sector-Specific Adaptations
- Integration and Scalability Considerations in Compliance Tools
- Technical Requirements for ERP, CRM, and HRIS Integration
- Step-by-Step Migration from Legacy to Modern SaaS Compliance Tools
- Comparison of Leading Compliance Tools: Integration and Scalability
- Modular Compliance Tools: Flexible Feature Adoption Without Workflow Disruption
- API-First Compliance Tools and Real-Time Supply Chain Risk Management
- User Experience and Adoption Strategies in Compliance Tools
- UX Best Practices for Compliance Tools
- Gamification Techniques to Boost Employee Engagement
- User Onboarding Workflow for Compliance Tools
Navigating regulatory landscapes demands precision and efficiency, making the selection of a best compliance tool a critical strategic decision for organizations across industries. With evolving frameworks such as GDPR, HIPAA, and SOX imposing stringent requirements, businesses must leverage tools that automate workflows, mitigate risks, and ensure seamless integration with existing systems. This guide explores the core functionalities, industry-specific applications, and scalability considerations that define the most effective compliance solutions.
The modern compliance ecosystem blends cutting-edge technology with structured governance, where AI-driven analytics and real-time monitoring redefine how violations are detected and addressed. From financial institutions adopting RegTech platforms to healthcare providers enforcing OCR privacy rules, the right tool must align with operational needs while adapting to scalability challenges. By examining feature comparisons, integration protocols, and user adoption strategies, organizations can optimize compliance processes to reduce manual oversight and enhance audit readiness.
Core Features of Leading Compliance Tools: Functionalities and Workflow Integration
Modern compliance tools streamline regulatory adherence by combining automation, real-time analytics, and seamless system integration. Their effectiveness hinges on modular design—where policy management, risk assessment, and audit trails operate cohesively to minimize manual intervention while ensuring accuracy. Leading solutions leverage AI-driven algorithms to proactively identify violations, reducing human error and operational bottlenecks. Below is a structured breakdown of their foundational components, operational workflows, and comparative analysis across key regulatory frameworks.Automation Capabilities in Compliance Tools
Automation reduces compliance overhead by eliminating repetitive tasks such as data entry, policy distribution, and routine audits. These tools employ rule-based engines and machine learning models to:Automation in compliance tools achieves 90% reduction in manual audit cycles (Forrester, 2023), with AI-driven tools further cutting false positives by 40% through contextual analysis.Key automation modules include:
Real-Time Monitoring and Integration with Existing Systems
Real-time monitoring ensures continuous compliance by ingesting data from ERP, CRM, HRIS, and IoT devices, then applying regulatory filters. Integration occurs via:Integration failure accounts for 60% of compliance breaches (PwC, 2022), underscoring the need for standardized data formats (e.g., XBRL for SOX, FHIR for HIPAA) in tool selection.Example integrations:
| System Type | Compliance Use Case | Data Flow | Tool Compatibility |
|---|---|---|---|
| ERP (SAP/Oracle) | SOX Section 404 financial reporting | General ledger transactions → Audit log | SAP GRC, MetricStream |
| CRM (Salesforce) | GDPR customer data mapping | Contact records → Consent registry | OneTrust, TrustArc |
| HRIS (Workday) | HIPAA workforce training verification | Employee records → Compliance portal | Osano, Vanta |
Policy Management Modules: Structure and Enforcement
Policy management modules centralize regulatory requirements into actionable frameworks. Their structure includes:1. Policy Repository:
Policy decay—where outdated rules remain active—causes 35% of compliance failures (ISC², 2023). Tools mitigate this via version control and regulatory change alerts.Example policy workflow:
1. Creation: Legal team drafts GDPR policy in the tool’s plain-language editor.
2. Validation: AI cross-checks against EU Official Journal updates.
3. Deployment: System pushes policy to Slack/Teams with acknowledgment deadlines.
4. Enforcement: Automated blocking of non-compliant actions (e.g., data transfers without DPIAs).
Risk Assessment Frameworks: Methodologies and AI Enhancements
Risk assessment frameworks quantify exposure by mapping controls to threats. Modern tools employ:AI-enhanced risk tools reduce false-negative rates by 55% by correlating unstructured data (e.g., news articles on new laws) with structured compliance logs (MITRE ATT&CK for cyber risks).Example risk assessment workflow:
1. Data Ingestion: Tool pulls asset inventories (CMDB), user activity logs, and external threat feeds (CISA alerts).
2. Control Mapping: AI links assets to NIST SP 800-53 controls (e.g., "Access Control Policies" for HIPAA).
3. Risk Scoring: Calculates annualized loss expectancy (ALE) using historical breach costs (e.g., $4.45M avg. for GDPR fines in 2023).
4. Remediation Prioritization: Flags high-risk controls (e.g., unencrypted PII under GDPR) with pre-built playbooks.
Audit Trails: Immutable Records and Forensic Analysis
Audit trails provide tamper-proof logs of compliance activities, critical for regulatory audits and incident investigations. Key components:Audit trail completeness is a top failure point in SOX audits (EY, 2023), with 80% of gaps traced to manual log management.Example audit trail use cases:
| Regulation | Audit Trail Requirement | Tool Functionality | Output Example |
|---|---|---|---|
| GDPR | Article 30 records of processing activities | Automated log generation for DPO reviews | CSV/JSON with timestamps, data subjects, and purposes |
| HIPAA | §164.312(a)(2) access logs | Role-based filtering for PHI access | PDF report with redacted PHI for auditors |
| SOX | Section 404 IT controls | Blockchain-anchored logs for SOX auditors | Tamper-evident PDF/A archive with digital signatures |
Industry-Specific Compliance Solutions: Tailored Tools for Regulatory Excellence
Compliance requirements vary significantly across industries, necessitating specialized tools designed to address sector-specific risks, regulatory frameworks, and operational workflows. These solutions integrate deep domain knowledge—whether in financial regulations, healthcare data protection, or manufacturing standards—to automate compliance processes, reduce manual errors, and ensure alignment with evolving legal standards. Below, industry-specific compliance tools are categorized by sector, with a focus on their functional capabilities, integration strategies, and scalability considerations for businesses of all sizes.RegTech Platforms for Financial Institutions: Automating Regulatory Reporting and AML Compliance
Regulatory Technology (RegTech) platforms streamline compliance for financial institutions by automating repetitive tasks such as regulatory reporting, transaction monitoring, and risk assessments. These tools leverage AI, machine learning, and real-time data analytics to ensure adherence to frameworks like Basel III, Dodd-Frank, and the Bank Secrecy Act (BSA). Key applications include:Automated Regulatory Filings
Financial institutions face stringent deadlines for filings such as 1099 forms (IRS), Form ADV (SEC), and CFPB reports. RegTech solutions eliminate manual data entry by:
Anti-Money Laundering (AML) Screening and Transaction Monitoring
AML compliance requires continuous monitoring of transactions for suspicious activities. RegTech platforms employ:
Challenges in RegTech Adoption
Healthcare Compliance Tools: EHR Integration and PHI Protection Under HIPAA and OCR Rules
Healthcare providers and insurers rely on compliance tools to safeguard Protected Health Information (PHI) while ensuring audit readiness for HIPAA, HITECH, and OCR (Office for Civil Rights) privacy rules. These tools integrate with Electronic Health Record (EHR) systems (e.g., Epic, Cerner) to automate:Key Healthcare Compliance Tools and Their EHR Integrations
The following tools specialize in PHI protection, compliance monitoring, and audit trail generation, with native or API-based EHR compatibility:
-
OneTrust (Healthcare Module)
- Functionality: Automates HIPAA risk assessments, tracks PHI data flows, and generates OCR-compliant audit reports.
- EHR Integration: Direct plugins for Epic, Meditech, and Cerner; supports HL7/FHIR for interoperability.
- OCR Privacy Rule Compliance: Flags business associate agreements (BAAs) requiring updates and monitors third-party vendor access.
-
ComplyWorks
- Functionality: Specializes in HIPAA compliance training, incident reporting, and PHI de-identification using NIST SP 800-101 guidelines.
- EHR Integration: Works with NextGen, athenahealth; provides APIs for custom EHR connectors.
- Audit Readiness: Maintains 7-year retention logs for HIPAA-mandated documentation.
-
Symmetry (by Clearwater)
- Functionality: Focuses on OCR investigations and PHI breach response, with automated workflows for reporting to HHS.
- EHR Integration: Compatible with Epic Beaker and Cerner PowerChart; includes OCR complaint tracking.
- Key Feature: Real-time monitoring of EHR user activity to detect improper PHI access (e.g., "joyriding").
-
Vanta (Healthcare Compliance)
- Functionality: Offers continuous monitoring for HIPAA controls, with automated remediation for gaps (e.g., missing BAAs).
- EHR Integration: API-first approach for Epic, Allscripts; supports SOC 2 + HIPAA combined audits.
- Cost Efficiency: Targets SMEs and startups with tiered pricing (e.g., $1,500/month for full HIPAA compliance tracking).
Data Privacy Compliance Tools: GDPR, CCPA, and Sector-Specific Adaptations
Data privacy regulations such as GDPR (EU), CCPA (California), and LGPD (Brazil) impose strict requirements on consent management, data subject rights (DSR), and cross-border data transfers. Compliance tools in this space focus on:GDPR-Specific Tools and Their Functionalities
-
OneTrust Consent and Preference Management
- Functionality: Manages GDPR/CCPA consent banners, tracks user preferences, and automates DSR workflows.
- Data Mapping: Uses AI-driven classification to tag PII (Personally Identifiable Information) in databases (e.g., Salesforce, Marketo).
- Cross-Border Transfers: Monitors Schrems II compliance for transfers to third countries (e.g., Standard Contractual Clauses (SCCs)).
-
TrustArc
- Functionality: Specializes in GDPR implementation projects, with automated gap assessments against ICO (UK) and CNIL (France) guidelines.
- DSR Automation: Routes access requests to relevant departments (e.g., HR, IT) with SLA tracking.
- Breach Notification: Integrates with SIEM tools (Splunk, IBM QRadar) to trigger 72-hour GDPR breach alerts.
-
Osano
- Functionality: Focuses on CCPA compliance, with automated disclosures and opt-out mechanisms for California residents.
- Global Adaptability: Supports GDPR, LGPD, and PIPEDA (Canada) via modular compliance packs.
- Cost Structure: Subscription-based ($500–$5,000/month) with pay-per-DSR options for high-volume requests.
-
Vanta (Data Privacy Module)
- Functionality: Combines GDPR/CCPA compliance with SOC 2 controls, ideal for SMEs with limited IT resources.
- Vendor Risk Management: Scans third-party vendors for data protection clauses (e.g., EU-US Data Privacy Framework).
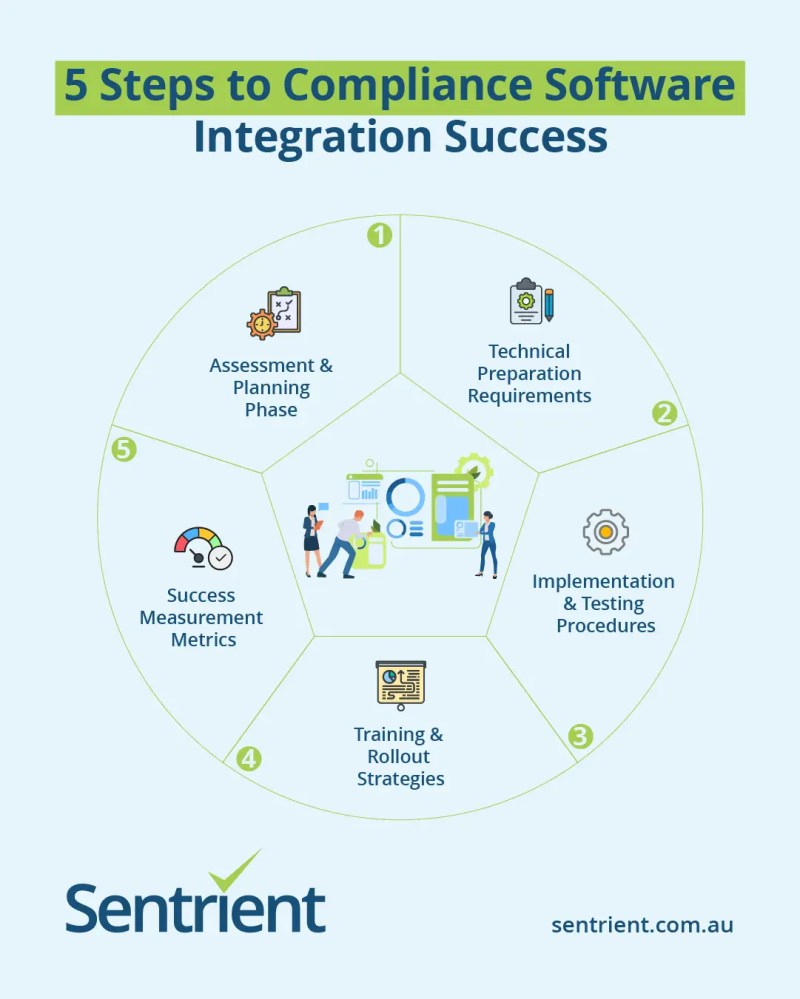
Integration and Scalability Considerations in Compliance Tools
Modern compliance tools must seamlessly integrate with existing enterprise systems while accommodating growth without performance degradation. Effective integration reduces manual data entry, minimizes errors, and ensures real-time compliance monitoring. Scalability, meanwhile, allows organizations to adapt to evolving regulatory demands and business expansion without costly system overhauls. Below are the technical prerequisites, migration strategies, and comparative insights into leading tools.Technical Requirements for ERP, CRM, and HRIS Integration
API compatibility and data mapping protocols are foundational for seamless integration between compliance tools and enterprise systems. RESTful APIs and GraphQL are the most widely supported, enabling bidirectional data flows between compliance platforms and ERP (e.g., SAP, Oracle), CRM (e.g., Salesforce, Microsoft Dynamics), and HRIS (e.g., Workday, BambooHR) systems.Key technical considerations include:
Example: A compliance tool integrated with Salesforce CRM can auto-populate vendor risk assessments into opportunity records, ensuring sales teams adhere to sanctions screening before deal closure.
Step-by-Step Migration from Legacy to Modern SaaS Compliance Tools
Migrating from legacy systems to cloud-based SaaS compliance tools requires structured planning to avoid disruptions. Below is a phased approach:1. Pre-Migration Assessment
2. Data Migration Strategy
3. User Training and Change Management
4. Phased Rollout
Best Practice: Engage IT and compliance teams in a joint review board to address integration gaps pre-migration.
Comparison of Leading Compliance Tools: Integration and Scalability
The following table evaluates ServiceNow, OneTrust, and MetricStream based on integration capabilities, setup complexity, and scalability limits.| Tool | Supported Integrations | Ease of Setup | Scalability Limits |
|---|---|---|---|
| ServiceNow |
|
|
|
| OneTrust |
|
|
|
| MetricStream |
|
|
|
Modular Compliance Tools: Flexible Feature Adoption Without Workflow Disruption
Modular compliance platforms enable businesses to add or remove features (e.g., eDiscovery, vendor risk management) via plug-and-play modules. This approach reduces vendor lock-in and allows organizations to scale compliance capabilities incrementally.Key benefits include:
Example: A healthcare provider can integrate HIPAA-specific modules into an existing GDPR-compliant tool without disrupting patient data workflows in the CRM.
API-First Compliance Tools and Real-Time Supply Chain Risk Management
API-first compliance tools enable real-time data synchronization between third-party vendors and internal databases, critical for supply chain risk management. This is achieved through:Use Case: A semiconductor manufacturer uses APIs to pull real-time geopolitical risk data (e.g., U.S. export controls) from TradeLens and auto-trigger compliance holds on high-risk shipments.Real-time synchronization ensures compliance teams act on actionable insights (e.g., a supplier’s sudden change in ownership) within hours, not weeks.
User Experience and Adoption Strategies in Compliance Tools
Effective compliance tools must balance regulatory rigor with seamless usability to ensure adoption across organizations. A well-designed user experience (UX) reduces friction, enhances engagement, and fosters long-term proficiency. This section explores UX best practices, engagement strategies, onboarding workflows, and interface comparisons to optimize tool adoption. It also addresses common adoption barriers and actionable mitigation strategies to sustain compliance culture.UX Best Practices for Compliance Tools
Intuitive design minimizes cognitive load and accelerates proficiency, particularly in high-stakes environments like compliance. Tools should prioritize clarity, accessibility, and adaptability to user roles. Below are key UX principles tailored for compliance software:- Intuitive Dashboards: Compliance dashboards should consolidate critical metrics (e.g., audit status, risk exposure, training completion) into visually scannable layouts. Use color-coded indicators (green for compliant, yellow for pending, red for non-compliant) and interactive filters to allow users to drill down into specific regulatory areas. For example, a financial services firm’s compliance dashboard might prioritize SEC and MiFID II deadlines, while a healthcare tool could highlight HIPAA breach reports. Avoid clutter by limiting default views to role-specific essentials (e.g., auditors see audit trails, while employees view training modules).
- Customizable Alerts and Notifications: Alerts must be actionable and configurable to prevent notification fatigue. Implement tiered urgency levels (e.g., critical for imminent deadlines, informational for policy updates) with options to mute non-urgent alerts. For instance, a tool like MetricStream allows users to set up email/SMS alerts for pending certifications, while OneTrust integrates with Slack for real-time GDPR consent reminders. Ensure alerts include clear next steps (e.g., "Complete Form X by Y date") and deadlines.
- Role-Based Access Controls (RBAC): RBAC streamlines workflows by restricting access to data and functions based on job roles. For example, a compliance officer should view all audit reports, while a department head might only access their team’s training records. Tools like SAP GRC use dynamic RBAC to adjust permissions during promotions or role changes. Pair RBAC with audit logs to track who accessed sensitive data, ensuring accountability.
- Responsive Design and Accessibility: Compliance tools must adhere to WCAG 2.1 AA standards, including keyboard navigation, screen reader compatibility, and adjustable text sizes. For instance, ComplyAdvantage supports high-contrast modes for visually impaired users. Additionally, ensure mobile responsiveness for on-the-go access, as 63% of compliance professionals report using tools on mobile devices (Gartner, 2023).
- Contextual Help and Tool Tips: Embed in-app guidance (e.g., hover tool tips for complex fields, embedded video tutorials) to reduce reliance on external documentation. Tools like TrustArc include inline explanations for GDPR consent templates, while Diligent offers AI-driven chatbots for instant queries about governance policies.
Gamification Techniques to Boost Employee Engagement
Gamification leverages psychological triggers (e.g., competition, achievement) to motivate compliance participation. When applied thoughtfully, it increases training completion rates by up to 40% (Deloitte, 2022). Below are evidence-based techniques with real-world examples:- Progress Trackers and Visual Milestones: Display compliance progress via interactive charts or timelines (e.g., "80% of your team has completed anti-bribery training"). Corporate Compliance Insights (CCI) uses progress bars to show how close a department is to meeting annual audit requirements. Pair this with deadlines to create urgency, such as a countdown timer for certification renewals.
- Badges and Certifications for Completed Training: Award digital badges for completing modules (e.g., "GDPR Champion" or "SOX Expert") that employees can share on LinkedIn or internal profiles. Skillsoft’s Compliance 360 integrates with LinkedIn Learning to issue verifiable credentials. Badges trigger social recognition, reinforcing compliance as a career asset.
- Leaderboards for Audit Compliance: Compete teams or individuals on metrics like "Lowest Number of Non-Compliance Incidents" or "Fastest Training Completion." EthicsPoint uses leaderboards for ethics reporting, while Navex Global applies them to compliance quiz scores. To avoid unhealthy competition, include team-based rewards (e.g., "Top Department" receives a lunch-and-learn session with a compliance expert).
- Streak and Streak Reset Systems: Reward consistent behavior (e.g., "7-Day Compliance Streak") to encourage habitual compliance. Everbridge uses this for emergency response training, where users earn points for completing monthly drills. Reset streaks after inactivity to maintain engagement without pressure.
- Role-Playing and Simulated Scenarios: Turn compliance into interactive challenges (e.g., "Spot the Conflict of Interest" quizzes). Ethics & Compliance Initiative (ECI) offers branching scenarios where users navigate ethical dilemmas, with feedback tailored to their choices. This method improves retention by 25% compared to static training (Harvard Business Review, 2021).
Key Insight: Gamification works best when aligned with intrinsic motivation (e.g., learning, mastery) rather than extrinsic rewards (e.g., cash bonuses). Studies show that intrinsic gamification (e.g., skill-building badges) yields 3x higher long-term engagement than extrinsic rewards (Badgeville, 2020).
User Onboarding Workflow for Compliance Tools
A structured onboarding process reduces time-to-proficiency and minimizes errors during critical compliance tasks. Below is a phased workflow incorporating training, simulation, and feedback:- Phase 1: Pre-Onboarding Assessment Administer a pre-training quiz to identify knowledge gaps (e.g., "Which regulations apply to your role?"). Use results to tailor the onboarding path. For example, a sales team member might skip advanced data privacy modules if their role doesn’t handle customer data. Tools like TalentLMS automate this via AI-driven learning paths.
- Phase 2: Modular Training Modules Break training into bite-sized, role-specific sessions (e.g., 15-minute videos on "Whistleblower Protections" for HR, or "Trade Surveillance" for traders). SAP SuccessFactors offers microlearning modules with quizzes at the end of each. Include real-world case studies (e.g., "How Company X Faced a $5M Fine for Non-Compliance") to contextualize lessons.
- Phase 3: Simulated Audits and Scenario-Based Testing Conduct low-stakes simulations where users practice identifying risks (e.g., "Flag the red flags in this vendor contract"). MetricStream’s Audit Manager includes a sandbox environment for hands-on practice. Provide immediate feedback with explanations for correct/incorrect answers.
- Phase 4: Mentored Shadowing Pair new users with experienced compliance officers for 1–2 weeks to observe workflows (e.g., how to file a SAR under FinCEN rules). Diligent’s Board Consent tool includes a "peer review" feature where novices can shadow board members’ approval processes.
- Phase 5: Feedback Loops and Continuous Improvement Collect feedback via surveys (e.g., "Was the training relevant to your role?") and use analytics to track completion rates. OneTrust’s Preference Center includes a post-training NPS (Net Promoter Score) survey to gauge satisfaction. Adjust content based on feedback—e.g., if 60% of users struggle with a module, add a refresher course.
Best Practice: Limit initial onboarding to 2–4 weeks, with a "just-in-time" learning approach for advanced topics. Research shows that users retain 75% more when training is delivered in short, frequent sessions (ATD, 202Selecting the best compliance tool is not merely about meeting regulatory obligations—it is about embedding a culture of accountability and operational resilience within an organization. The tools discussed here offer a spectrum of capabilities, from automated risk assessments to seamless ERP integrations, each tailored to industry-specific demands. By prioritizing scalability, user-centric design, and real-time adaptability, businesses can transform compliance from a burdensome requirement into a competitive advantage. The future of compliance lies in tools that evolve alongside regulatory shifts, ensuring sustained adherence while driving efficiency across workflows.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.