api comprehensive guide e commerce mastering seamless
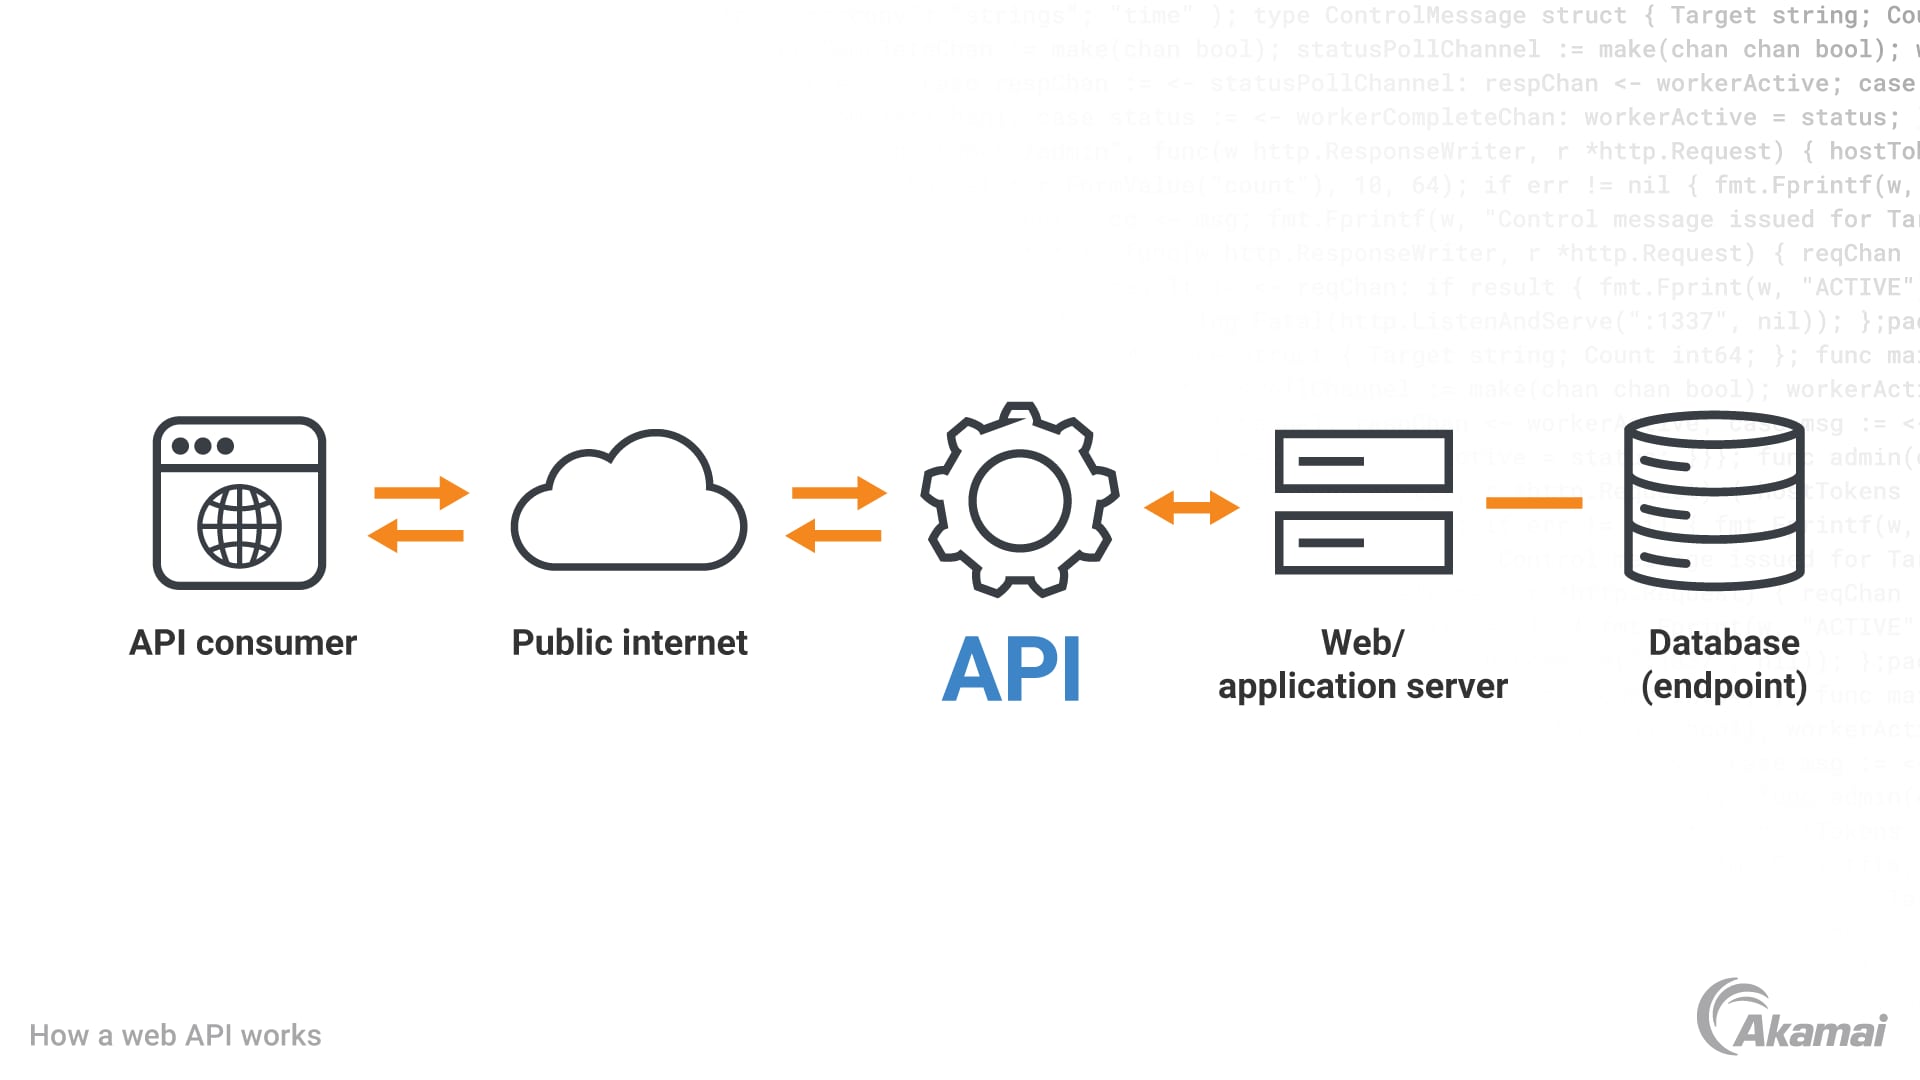
Table of Contents
- APIs as the Backbone of Modern E-Commerce Ecosystems
- Core Functions of APIs in E-Commerce Architecture
- Common API Types in E-Commerce and Their Use Cases
- Comparative Analysis: REST vs. GraphQL in E-Commerce
- Architectural Patterns of Leading E-Commerce APIs
- Core API Features for E-Commerce Functionality
- Essential API Endpoints by Domain
- Security Protocols for E-Commerce APIs
- Best Practices for API Versioning in E-Commerce
- API Development: Tools, Frameworks, and Workflows for E-Commerce
- Top Tools and Frameworks for E-Commerce API Development
- API Development Workflow for E-Commerce
- Performance Optimization and Scalability Strategies for E-Commerce APIs
- Caching Strategies for Faster API Responses
- Load Balancing and Microservices for Scalability
- Monitoring API Performance in E-Commerce
- Implementing API Rate Limiting and Throttling
E-commerce platforms rely on APIs as the invisible yet critical infrastructure that powers real-time transactions, inventory synchronization, and third-party integrations. This API comprehensive guide e commerce explores how REST, GraphQL, and WebSockets enable scalable architectures while addressing security, performance, and compliance challenges.
From authentication protocols like OAuth 2.0 to real-time event handling via webhooks, modern e-commerce APIs must balance flexibility with robustness. The guide dissects architectural patterns from Shopify and Amazon MWS, contrasts synchronous versus asynchronous workflows, and provides actionable benchmarks for payload efficiency. Developers and merchants will gain insights into optimizing APIs for peak traffic, ensuring PCI compliance, and leveraging tools like Swagger and Postman for seamless documentation and testing.
APIs as the Backbone of Modern E-Commerce Ecosystems
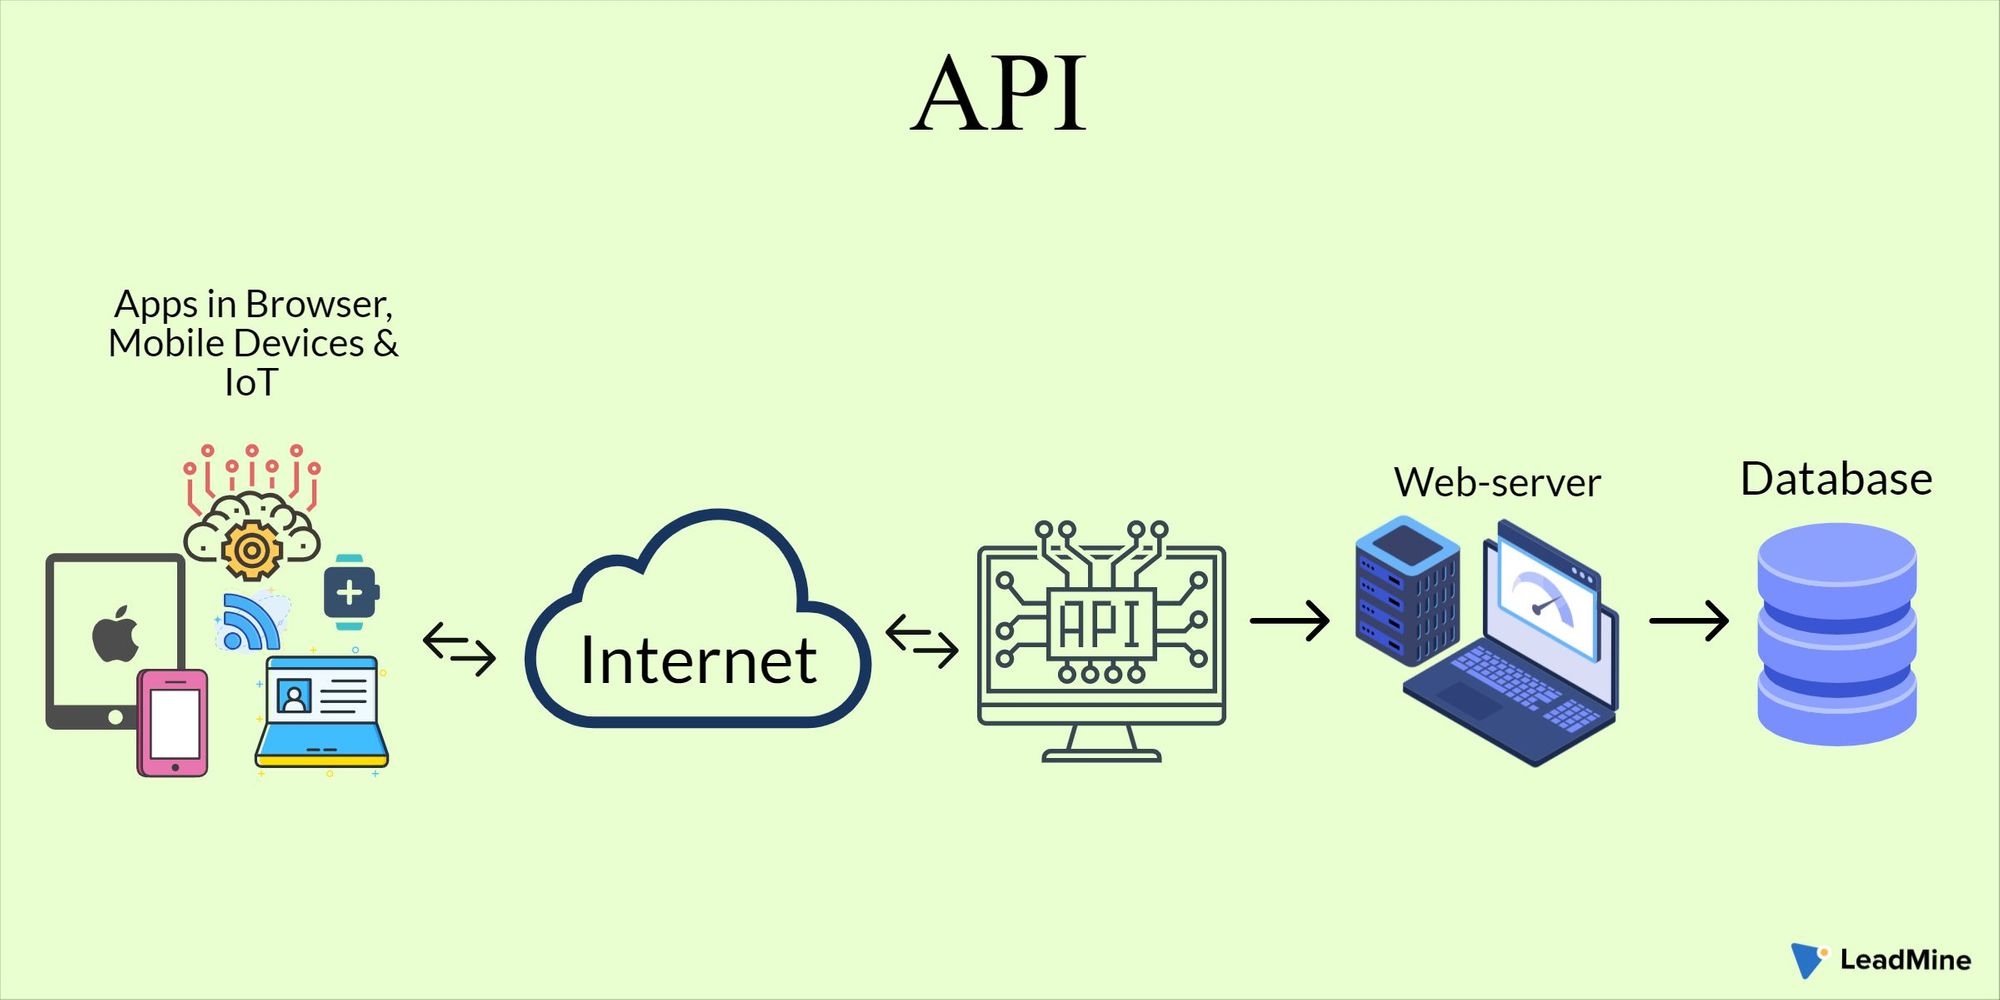
E-commerce platforms rely on seamless data exchange between disparate systems to deliver a cohesive user experience. APIs (Application Programming Interfaces) serve as the critical middleware that connects front-end interfaces—such as product catalogs, checkout pages, and customer dashboards—with back-end infrastructure, including inventory management, payment processing, and logistics networks. Without APIs, real-time synchronization of orders, stock levels, and transactions would be impossible, leading to inefficiencies in high-velocity retail environments. Their role extends beyond internal operations to facilitate third-party integrations, enabling merchants to extend functionality through plugins, marketplaces, and analytics tools.The architecture of modern e-commerce APIs is built on standardized protocols that balance performance, flexibility, and security. REST (Representational State Transfer) remains the dominant choice for its simplicity and widespread adoption, while GraphQL offers granular data fetching for complex queries. WebSockets provide real-time capabilities for live updates, such as order status notifications or inventory alerts. Each protocol is optimized for specific use cases, with trade-offs in payload efficiency, scalability, and development complexity.
Core Functions of APIs in E-Commerce Architecture
APIs in e-commerce perform three primary functions: data synchronization, transaction processing, and system integration. Data synchronization ensures that inventory levels, pricing, and product attributes are consistent across all channels, reducing discrepancies that could lead to overselling or customer dissatisfaction. Transaction processing APIs handle payment authorization, refunds, and fraud detection by interfacing with gateways like Stripe or PayPal, while also logging activities for compliance and auditing. System integration APIs enable connectivity with external services, such as ERP systems (e.g., SAP, NetSuite), CRM platforms (e.g., Salesforce, HubSpot), and logistics providers (e.g., FedEx, DHL), streamlining operations like order fulfillment and customer support.The efficiency of these functions depends on the API’s ability to handle concurrent requests, manage retries for failed operations, and enforce security policies. For example, a high-traffic store during a holiday sale may experience thousands of simultaneous requests for inventory checks and order placements. APIs must implement rate limiting (e.g., 1,000 requests per minute) and exponential backoff mechanisms to prevent system overload while maintaining responsiveness.
Common API Types in E-Commerce and Their Use Cases
The selection of an API protocol depends on the specific requirements of the e-commerce system, including latency sensitivity, data complexity, and scalability needs. Below are the three most prevalent API types in e-commerce, along with their ideal applications and performance benchmarks.-
REST (Representational State Transfer)
REST APIs use HTTP methods (GET, POST, PUT, DELETE) to interact with resources identified by URLs. They are stateless, cacheable, and leverage standard HTTP status codes (e.g., 200 OK, 404 Not Found) for error handling. REST is ideal for:- CRUD operations (Create, Read, Update, Delete) on products, orders, and customers.
- Public-facing endpoints where simplicity and broad compatibility are prioritized.
- Systems requiring caching (e.g., product catalogs) to reduce server load.
- Payload Size: Typically larger due to fixed response structures (e.g., JSON/XML with redundant fields).
- Latency: Low for simple queries (e.g., fetching a single product), but can degrade with nested data.
- Scalability: Handles high traffic well when optimized with CDNs and load balancers.
- Example Use Case: Shopify’s Admin API for managing store operations.
-
GraphQL
GraphQL allows clients to request only the data they need, reducing over-fetching and under-fetching issues common in REST. It uses a single endpoint and resolves queries via a schema-defined structure. GraphQL excels in:- Complex queries requiring multiple data sources (e.g., fetching a product with reviews, inventory, and pricing tiers).
- Front-end applications where dynamic data loading improves performance (e.g., single-page apps).
- Microservices architectures where APIs must aggregate data from disparate back-end services.
- Payload Size: Smaller for targeted queries (e.g., fetching only `id`, `name`, and `price` of a product).
- Latency: Higher initial setup due to schema validation, but faster for deep queries.
- Scalability: Requires careful schema design to avoid N+1 query problems; benefits from tools like DataLoader.
- Example Use Case: BigCommerce’s GraphQL API for headless commerce setups.
-
WebSockets
WebSockets enable full-duplex communication over a single TCP connection, ideal for real-time updates. They are used in:- Live order tracking and notifications (e.g., "Your order is shipping").
- Chat support systems integrated with e-commerce platforms.
- Collaborative tools like shared carts or multi-user product editing.
- Payload Size: Minimal overhead for small, frequent messages.
- Latency: Near-instantaneous for bidirectional communication.
- Scalability: Requires connection management to handle concurrent users; often paired with message brokers (e.g., Redis, RabbitMQ).
- Example Use Case: WooCommerce’s WebSocket-based live chat integrations.
Comparative Analysis: REST vs. GraphQL in E-Commerce
While REST and GraphQL serve similar purposes, their architectural differences significantly impact performance, development effort, and operational costs. The following table contrasts their key attributes in the context of e-commerce:| Attribute | REST | GraphQL |
|---|---|---|
| Payload Size | Larger due to fixed response structures; over-fetching common (e.g., returning 50 fields when only 5 are needed). | Optimized for client-defined queries; eliminates redundant data transfer. |
| Flexibility | Limited to pre-defined endpoints; versioning required for backward compatibility. | Highly flexible schema allows incremental evolution without breaking changes. |
| Scalability | Scalable with horizontal scaling (e.g., load balancers, CDNs); caching improves performance. | Scalability depends on query complexity; N+1 queries can degrade performance without optimization. |
| Development Complexity | Lower for simple CRUD operations; requires multiple endpoints for related data. | Higher initial setup (schema design, tooling); reduces long-term maintenance for complex front-ends. |
| Real-Time Capabilities | Polling or Server-Sent Events (SSE) required for updates; not native. | Supports subscriptions for real-time data (e.g., live inventory updates). |
| Use Case Fit | Best for public APIs, mobile apps, and systems requiring caching. | Ideal for headless commerce, SPAs, and applications needing granular data control. |
For high-traffic e-commerce stores with simple data requirements (e.g., product listings, basic orders), REST remains the pragmatic choice due to its maturity and caching benefits. GraphQL is preferable for complex front-ends (e.g., custom store builders) or when aggregating data from multiple microservices. Hybrid approaches, such as using REST for public APIs and GraphQL for internal tools, are increasingly common.
Architectural Patterns of Leading E-Commerce APIs
Major e-commerce platforms employ distinct API architectures tailored to their scale and use cases. Below are three prominent examples and their design principles:-
Shopify API
- Protocol: REST with GraphQL overlay (Shopify Storefront API).
- Authentication: OAuth 2.0 for merchant access; API keys for public apps.
- Rate Limiting: 40 requests per second per app; burst limits for high-traffic periods.
- Retrieval and Listing
- `GET /products` – Fetch product listings with filters (e.g., category, price range, stock status).
- `GET /products/{id}` – Retrieve detailed product information, including descriptions, images, and attributes.
- `GET /products/{id}/variants` – Access variant-specific data (e.g., size, color) with inventory levels.
- Management and Updates
- `POST /products` – Create new products with metadata (e.g., SKU, taxonomies).
- `PATCH /products/{id}` – Update product attributes (e.g., pricing, availability).
- `DELETE /products/{id}` – Remove products from the catalog (soft/hard delete).
- Inventory Synchronization
- `GET /inventory/{productId}` – Check real-time stock levels across warehouses.
- `POST /inventory/{productId}/restock` – Trigger inventory replenishment events.
- `GET /inventory/low-stock-alerts` – Subscribe to threshold-based notifications (via webhooks).
- Cart Operations
- `POST /carts` – Initialize a new cart (session-bound or anonymous).
- `GET /carts/{cartId}` – Retrieve cart contents with item quantities, discounts, and subtotals.
- `POST /carts/{cartId}/items` – Add/remove items with quantity adjustments.
- `PATCH /carts/{cartId}/apply-coupon` – Apply promotional codes or discounts.
- Checkout Flow
- `POST /carts/{cartId}/checkout` – Initiate payment processing with order confirmation.
- `GET /carts/{cartId}/shipping-options` – Fetch carrier rates and delivery estimates.
- `POST /carts/{cartId}/guest-checkout` – Enable one-click purchases for non-registered users.
- Order Creation and Retrieval
- `POST /orders` – Create an order from a confirmed cart (idempotent operations recommended).
- `GET /orders/{orderId}` – Retrieve order details, including line items, taxes, and shipping addresses.
- `GET /orders?status={status}` – Filter orders by status (e.g., `pending`, `shipped`, `cancelled`).
- Fulfillment and Tracking
- `PATCH /orders/{orderId}/fulfill` – Mark items as shipped with carrier tracking numbers.
- `GET /orders/{orderId}/returns` – Initiate return requests with RMA (Return Merchandise Authorization) generation.
- `POST /orders/{orderId}/cancel` – Cancel orders with refund processing triggers.
- Authentication and Authorization
- `POST /auth/login` – Issue JWT or session tokens (with multi-factor authentication support).
- `POST /auth/register` – Create user accounts with email verification.
- `POST /auth/refresh-token` – Renew expired access tokens.
- Profile and Preferences
- `GET /users/{userId}` – Retrieve user details (e.g., name, email, shipping addresses).
- `PATCH /users/{userId}/addresses` – Update saved addresses or payment methods.
- `GET /users/{userId}/orders` – Fetch order history with pagination.
- Payment Processing
- `POST /payments/intents` – Create payment intents (e.g., credit card, digital wallets).
- `GET /payments/{paymentId}` – Retrieve transaction status (e.g., `succeeded`, `failed`, `requires_action`).
- `POST /payments/{paymentId}/capture` – Finalize authorized amounts.
- Refunds and Disputes
- `POST /payments/{paymentId}/refund` – Process refunds with partial amounts.
- `GET /payments/{paymentId}/disputes` – Retrieve chargeback details.
- Tokenization and Encryption
- Replace raw payment data (e.g., credit card numbers) with tokens issued by PCI-compliant providers (e.g., Stripe, Braintree).
- Implement field-level encryption for PII (Personally Identifiable Information) using AES-256 or TLS 1.2+ for data in transit.
- Authentication and Authorization
- Enforce OAuth 2.0 with scopes (e.g., `orders:write`, `payments:read`) and JWT with short expiration times.
- Use API keys for server-to-server communication with rate limiting (e.g., 1000 requests/minute).
- Implement mutual TLS (mTLS) for high-security endpoints (e.g., financial transactions).
- Compliance Adherence
- PCI DSS: Segregate payment data storage, conduct quarterly scans, and restrict access via role-based permissions.
- GDPR: Provide users with right to erasure (e.g., `DELETE /users/{userId}`) and data portability endpoints (e.g., `GET /users/{userId}/export`).
- SOX/ISO 27001: Log all API requests for audit trails, especially for financial transactions.
- Rate Limiting and DDoS Protection
- Deploy token bucket or leaky bucket algorithms to prevent abuse (e.g., 10 requests/second per IP).
- Integrate with Cloudflare or AWS Shield for DDoS mitigation.
- Input Validation and Injection Prevention
- Sanitize all inputs (e.g., SQL injection via `WHERE id = {userInput}`) using parameterized queries.
- Validate payloads against JSON schemas (e.g., `draft-07` for OpenAPI/Swagger).
- Audit Logging and Monitoring
- Log API calls with metadata (e.g., timestamp, user agent, payload hash) in a centralized system (e.g., ELK Stack).
- Set up alerts for anomalies (e.g., sudden spikes in failed payment attempts).
- URI Path Versioning (e.g., `/v1/products`) – Simple but pollutes the namespace.
- Header Versioning (e.g., `Accept: application/vnd.company.v1+json`) – Cleaner but requires client-side awareness.
- Media Type Versioning (e.g., `Content-Type: application/vnd.company.order-v2+json`) – Semantic but complex to implement.
- Query Parameter Versioning (e.g., `/products?version=2`) – Avoid for production due to caching issues.
Core API Features for E-Commerce Functionality
E-commerce platforms rely on APIs to orchestrate seamless interactions between frontend interfaces, third-party services, and backend systems. A well-designed API architecture ensures scalability, real-time updates, and secure transactions—critical for user trust and operational efficiency. Below, the essential API endpoints are categorized by domain, alongside security protocols and implementation best practices to safeguard data integrity and compliance.
Essential API Endpoints by Domain
E-commerce APIs must support core functionalities across multiple domains to enable end-to-end workflows. These endpoints form the backbone of product discovery, transaction processing, and user management. The following categorization aligns with industry standards and ensures modularity for future integrations.Products and Inventory
Product-related APIs enable dynamic catalog management, real-time stock updates, and variant handling. Key endpoints include:
Shopping Carts and Checkout
Cart APIs manage user sessions, item additions, and checkout workflows. These endpoints must support atomic operations to prevent race conditions during concurrent edits.
Orders and Fulfillment
Order APIs handle transaction records, status updates, and fulfillment tracking. These endpoints integrate with ERP, logistics providers, and customer support systems.
User Accounts and Authentication
User APIs manage identities, permissions, and profile data while adhering to privacy regulations. These endpoints often integrate with OAuth 2.0/OpenID Connect for secure authentication.
Payments and Financial Transactions
Payment APIs must comply with PCI DSS (Payment Card Industry Data Security Standard) and support tokenization to minimize exposure of sensitive data. These endpoints often delegate processing to third-party gateways (e.g., Stripe, PayPal).
Security Protocols for E-Commerce APIs
Security is non-negotiable in e-commerce APIs, particularly for payment processing and user data. Compliance with standards like PCI DSS, GDPR, and HIPAA (where applicable) requires layered defenses against breaches, fraud, and unauthorized access.Data Protection Measures
Threat Mitigation Strategies
Best Practices for API Versioning in E-Commerce
Versioning ensures backward compatibility during API evolution while minimizing disruptions to clients. Poor versioning strategies can lead to deprecation chaos or unexpected breaking changes. Below are proven strategies with trade-offs:
API versioning should prioritize stability (for clients) and flexibility (for developers). Common approaches include:
Versioning Strategy Comparison - Asynchronous processing for handling high traffic during peak sales (e.g., Black Friday).
- Microservices support to modularize functionalities like inventory, payments, and user authentication.
- Built-in security for OAuth 2.0, JWT, and rate limiting to mitigate fraud and abuse.
-
Node.js + Express
- Pros: Non-blocking I/O for high scalability, extensive npm ecosystem for plugins (e.g.,
express-rate-limit,passport-js), and real-time capabilities via WebSockets. Ideal for headless commerce and serverless architectures. - Cons: Callback hell in asynchronous code (mitigated by Promises/async-await), single-threaded nature requires clustering for CPU-heavy tasks.
- Use Case: Shopify Hydrogen (React-based storefronts), custom APIs for marketplace integrations.
- Pros: Non-blocking I/O for high scalability, extensive npm ecosystem for plugins (e.g.,
-
Django REST Framework (Python)
- Pros: Batteries-included ORM (Django), automatic serialization, and built-in authentication (e.g., TokenAuthentication, SessionAuthentication). Strong typing and validation reduce runtime errors.
- Cons: Steeper learning curve for beginners, monolithic design may require refactoring for large-scale microservices.
- Use Case: Magento 2 (PHP/Laravel), SaaS-based e-commerce platforms with complex business logic.
-
Spring Boot (Java/Kotlin)
- Pros: Enterprise-grade performance, Spring Security for OAuth2/OpenID Connect, and seamless integration with databases (JPA/Hibernate). Suitable for high-transaction environments.
- Cons: Verbose configuration, slower development cycle compared to dynamic languages.
- Use Case: Large-scale B2B platforms (e.g., SAP Commerce Cloud), APIs requiring strict compliance (e.g., PCI DSS for payments).
-
Ruby on Rails (API Mode)
- Pros: Convention over configuration accelerates prototyping, ActiveRecord for database interactions, and strong community support for e-commerce gems (e.g.,
spree,solidus). - Cons: Performance bottlenecks under extreme load, declining popularity for new projects.
- Use Case: Legacy systems migration, niche marketplaces with rapid iteration needs.
- Pros: Convention over configuration accelerates prototyping, ActiveRecord for database interactions, and strong community support for e-commerce gems (e.g.,
-
Go (Gin/Gorilla Mux)
- Pros: Compiled binary for low latency, goroutines for concurrent request handling, and minimal memory overhead. Preferred for high-throughput APIs (e.g., order processing).
- Cons: Limited ecosystem for e-commerce-specific libraries, less ideal for complex business logic.
- Use Case: High-frequency trading APIs, real-time inventory synchronization.
-
Shopify Hydrogen
- Pros: React-based storefronts with Shopify’s GraphQL API, optimized for performance (e.g., lazy loading, edge caching). Supports custom checkout flows.
- Cons: Vendor lock-in to Shopify’s ecosystem, higher cost for enterprise plans.
-
BigCommerce Headless API
- Pros: RESTful and GraphQL APIs with built-in support for multi-channel sales (e.g., Amazon, eBay). Strong B2B features.
- Cons: Limited flexibility for custom integrations outside BigCommerce’s partners.
-
Vendure (Node.js)
- Pros: Open-source, modular, and extensible. Supports custom APIs via TypeScript decorators. Ideal for developers seeking full control.
- Cons: Requires in-house expertise for setup and maintenance.
- API Specs: Draft OpenAPI/Swagger documents early to enforce consistency. Example: Define endpoints for `/cart/add`, `/checkout/start`, and `/orders/{id}/cancel`.
- Data Models: Design relational (PostgreSQL) or NoSQL (MongoDB) schemas for entities like `Product`, `Order`, and `PaymentIntent`.
- Security: Implement rate limiting (e.g., 100 requests/minute for public APIs) and input validation to prevent SQL injection or XSS.
- Code Base: Use modular design (e.g., separate services for `auth`, `payments`, `inventory`) with clear separation of concerns.
- SDKs: Generate client libraries for merchants (e.g., Python, JavaScript) using tools like OpenAPI Generator.
- CI/CD: Automate testing and deployment with GitHub Actions or GitLab CI. Example pipeline:
- Redis for In-Memory Caching: Stores session data, product catalogs, and user preferences with sub-millisecond latency. Redis clusters support high availability and horizontal scaling, making it ideal for real-time inventory updates.
- Example: Amazon uses Redis to cache product metadata, reducing database load by 80% during peak traffic.
- CDN-Based Caching: Distributes static assets (images, CSS, JavaScript) globally, reducing latency for geographically dispersed users. APIs can leverage CDNs for edge caching of structured data (e.g., JSON-LD for SEO).
- Database Query Caching: Caches SQL results (e.g., via PostgreSQL’s `pg_cache`) to avoid reprocessing identical queries. Useful for product filters and search suggestions.
- Lazy Loading for Product Catalogs: Loads high-resolution images or detailed descriptions only when requested, reducing initial page load times by 30–50%.
- Identify high-frequency API endpoints (e.g., `/products`, `/cart`) and cache responses with TTL (Time-To-Live) policies.
- Use Redis for session storage and CDNs for static assets, ensuring cache invalidation on product updates.
- Implement cache warming during off-peak hours to preload critical data for anticipated traffic spikes.
- Monitor cache hit ratios (target: >90%) and adjust TTLs based on data volatility (e.g., flash sales vs. static pages).
- Compress cached responses (e.g., gzip) and use HTTP/2 for multiplexed requests.
- Layer 4 (Transport) Load Balancing: Distributes traffic based on IP/port (e.g., NGINX, HAProxy). Best for stateless APIs like inventory checks.
- Layer 7 (Application) Load Balancing: Routes requests based on URL paths or headers (e.g., AWS ALB, Kong). Enables A/B testing and canary deployments for API features.
- Global Server Load Balancing (GSLB): Directs users to the nearest regional API endpoint, reducing latency for international e-commerce.
- Isolated Scaling: Scale the `checkout-service` during holidays without affecting the `blog-service`.
- Fault Isolation: A failure in the `inventory-service` doesn’t disrupt the `user-profile-service`.
- Tech Diversity: Use Node.js for real-time cart updates and Go for high-performance payment processing.
- TTFB (Time to First Byte): Measures backend processing time. Target: <100ms for 95% of requests.
- Error Rates: Track HTTP 5xx errors and 429 (Too Many Requests) responses to detect throttling issues.
- Throughput: Requests per second (RPS) to identify scaling limits (e.g., 10,000 RPS during peak hours).
- Latency Percentiles: P99 (worst 1% of requests) to catch outliers affecting user experience.
- Cache Hit/Miss Ratios: Indicates caching efficiency (e.g., 95% hit rate for product listings).
- New Relic: APM (Application Performance Monitoring) for transaction tracing and dependency mapping.
- Datadog: Log management and custom dashboards for API-specific metrics.
- Prometheus + Grafana: Open-source stack for time-series metrics and visualization.
- Sentry: Error tracking with stack traces for debugging API failures.
- Define SLOs (e.g., 99.9% availability, <200ms TTFB) and configure alerts for breaches.
- Instrument APIs with distributed tracing (e.g., OpenTelemetry) to track request flows across microservices.
- Set up synthetic monitoring (e.g., Pingdom) to simulate user journeys and detect regional outages.
- Correlate monitoring data with business metrics (e.g., abandoned carts during API timeouts).
- Automate scaling policies (e.g., Kubernetes HPA) based on CPU/memory thresholds.
- Fixed Window Counter: Simple but can allow bursts at window edges (e.g., 100 requests per 60 seconds).
- Sliding Window Log: Tracks requests in a rolling window for smoother limits (e.g., 1,000 requests per minute).
- Token Bucket: Allows bursts up to a maximum rate (e.g., 5 tokens per second, bucket size 20).
- Define Rate Limits by Endpoint:
- `/products`: 100 requests/minute (public).
- `/orders`: 10 requests/
Building a high-performance e-commerce API requires strategic decisions at every layer—from selecting the right protocol to implementing granular rate limiting and caching strategies. This guide underscores that API design is not merely a technical exercise but a cornerstone of customer experience, operational efficiency, and competitive differentiation. By adopting best practices in versioning, security, and scalability, businesses can future-proof their platforms while unlocking new integrations for payments, logistics, and CRM systems.
| Method | Pros | Cons | Best For |
|---|---|---|---|
| URI Path | Easy to |
API Development: Tools, Frameworks, and Workflows for E-Commerce
APIs serve as the architectural foundation for modern e-commerce platforms, enabling seamless integration between frontend interfaces, third-party services, and backend systems. The selection of development tools, frameworks, and workflows directly impacts scalability, performance, and developer productivity. This section explores the most effective open-source and proprietary solutions, structured workflows for API development, and practical tools for documentation, testing, and integration.Top Tools and Frameworks for E-Commerce API Development
The choice of framework or toolkit influences development speed, maintainability, and scalability. Below are categorized recommendations for building e-commerce APIs, balancing flexibility, performance, and ecosystem support.Backend Frameworks and Runtimes
E-commerce APIs often require high concurrency, real-time processing, and microservices compatibility. The following frameworks are widely adopted for their robustness and developer experience:
Backend frameworks should prioritize:
For decoupled architectures where the frontend is separate from the backend, these frameworks provide pre-built API layers:
API Development Workflow for E-Commerce
A structured workflow ensures APIs meet performance, security, and scalability requirements. Below is a text-based representation of the workflow, from requirements to deployment:┌───────────────────────────────────────────────────────────────┐
│ API Development Workflow │
├───────────────────┬───────────────────┬───────────────────────┤
│ 1. Requirements │ 2. Design & │ 3. Implementation │
│ Gathering │ Architecture │ │
├─────────┬─────────┼─────────┬─────────┼─────────┬─────────────┤
│ - Jira │ - User │ - API │ - Data │ - Code │ - Unit │
│ Epics │ Stories│ Specs │ Models│ Base │ Testing │
│ - Swagger│ - Wire │ - Graph │ - DB │ - SDKs │ - CI/CD │
│ Mockups│ Frames│ QL │ Schema │ │ Setup │
├─────────┴─────────┴─────────┴─────────┴─────────┴─────────────┤
│ 4. Testing & QA │ 5. Deployment & Monitoring │
├───────────────────┼───────────────────────────────────────────┤
│ - Postman │ - Kubernetes/ │ - Prometheus/ │
│ Collections │ Docker │ Grafana │
│ - Load Testing │ - CDN (Cloudflare│ - Sentry for Error │
│ (Locust) │ Edge Functions)│ Tracking │
└───────────────────┴───────────────────┴───────────────────────┘
Key Stages Explained:
1. Requirements Gathering
Use tools like Jira or Linear to define epics (e.g., "Implement Multi-Currency Checkout") and user stories. API specifications should align with business goals, such as reducing cart abandonment via real-time inventory updates.
2. Design & Architecture
3. Implementation
# .github/workflows/deploy.yml
Performance Optimization and Scalability Strategies for E-Commerce APIs
E-commerce APIs must deliver sub-second response times while handling millions of concurrent requests, particularly during high-traffic events like Black Friday or seasonal sales. Poorly optimized APIs lead to abandoned carts, reduced conversion rates, and degraded user experience. This section explores techniques to minimize latency, scale infrastructure efficiently, and maintain reliability under peak loads, ensuring seamless transactions and real-time inventory updates.
Performance optimization in e-commerce APIs involves a multi-layered approach, combining infrastructure-level improvements with algorithmic efficiency. Caching, database tuning, and intelligent load distribution reduce server workload, while monitoring and rate-limiting prevent abuse and ensure fair resource allocation. Below are structured strategies to achieve high performance and scalability.
Caching Strategies for Faster API Responses
Caching reduces redundant computations and database queries, significantly improving response times for frequently accessed data. E-commerce APIs benefit from multi-tier caching, where static and semi-static content (e.g., product listings, category pages) are stored closer to the user.Key caching techniques include:
Implementation Checklist for Caching:
Load Balancing and Microservices for Scalability
Scalability in e-commerce APIs requires distributing traffic across servers to prevent overload. Horizontal scaling (adding more servers) and vertical scaling (upgrading server resources) serve different use cases, with microservices architectures enabling granular scaling of API modules.Load-Balancing Techniques:
Scaling Approaches Comparison:
| Criteria | Horizontal Scaling | Vertical Scaling |
|---|---|---|
| Definition | Adding more servers to distribute load. | Upgrading existing servers (CPU, RAM). |
| Use Case | Handling sudden traffic spikes (e.g., Black Friday). | Optimizing single-server performance for monolithic APIs. |
| Fault Tolerance | High (failure of one node doesn’t crash the system). | Low (single point of failure). |
| Complexity | Moderate (requires load balancers, service discovery). | Low (simpler to implement). |
| Cost Efficiency | Scalable but higher operational overhead. | Lower upfront cost but limited by hardware constraints. |
| Example Tools | Kubernetes, Docker Swarm, AWS Auto Scaling. | AWS RDS Upgrades, DigitalOcean Droplet Resizing. |
Decompose APIs into independent services (e.g., `auth-service`, `inventory-service`, `payment-service`) to scale components independently. Use API gateways (e.g., Kong, Apigee) to route requests and manage cross-service communication via synchronous (REST/gRPC) or asynchronous (Kafka) protocols.
Key Benefits:
Monitoring API Performance in E-Commerce
Proactive monitoring ensures APIs meet SLAs (Service Level Agreements) and identifies bottlenecks before they impact users. Critical metrics include Time to First Byte (TTFB), error rates, and throughput, with real-time alerts triggering automated remediation.Essential Monitoring Metrics:
Checklist for API Monitoring Setup:
Implementing API Rate Limiting and Throttling
Uncontrolled API requests can lead to denial-of-service (DoS) attacks or excessive cloud costs. Rate limiting enforces fair usage while throttling gracefully degrades performance under load. E-commerce APIs must balance protection with usability, especially for third-party integrations (e.g., marketplaces, affiliate networks).Rate-Limiting Algorithms:
Implementation Steps:
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of ir.msu.ac.zw.